
 Do Son
Banana Squad has compromised over 60 GitHub repos with malicious Python files, using UI quirks to hide malware and steal data from developers via a sophisticated supply chain attack.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.

North Korean APT Famous Chollima (Wagemole) is using a new Python-based RAT, PylangGhost, in fake job interviews to target crypto professionals and steal credentials.

Trend Micro uncovers a new attack method using misconfigured Docker Remote APIs and the Tor network to stealthily deploy cryptominers and establish persistent access.

Threat actors are actively compromising poorly managed MySQL servers, using UDFs to inject Gh0stRAT, XWorm, HpLoader, and legitimate Zoho agents for full system control and data theft.
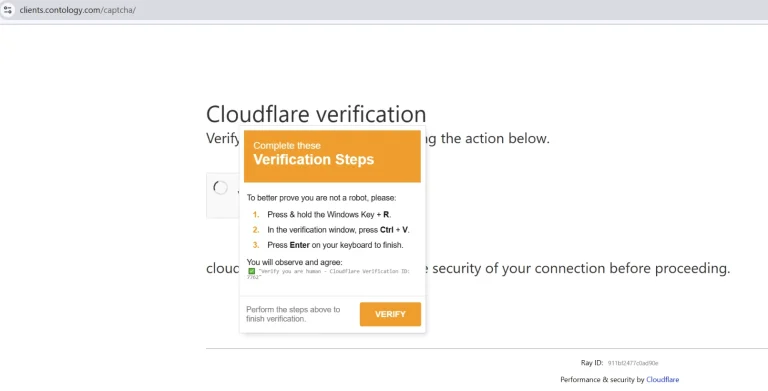
Elastic uncovers a sophisticated ClickFix campaign deploying the GHOSTPULSE loader to deliver ARECHCLIENT2 malware, leveraging social engineering for credential theft and remote access.

Water Curse is using GitHub to distribute malicious open-source projects, weaponizing 76 accounts with multi-stage malware targeting developers, red teamers, and gamers.
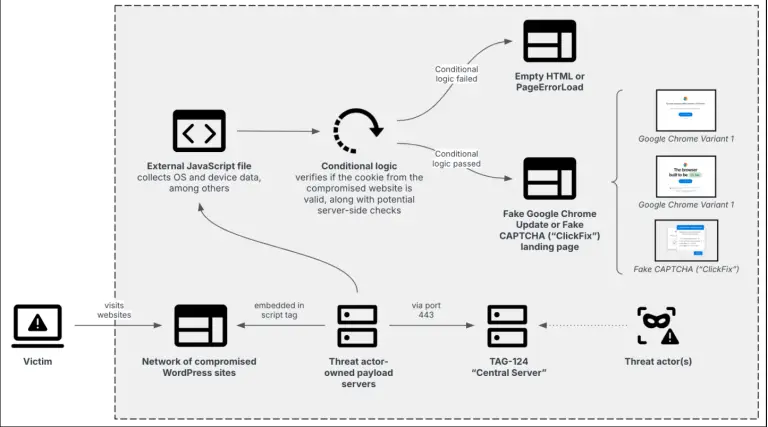
GrayAlpha, linked to FIN7, escalates tactics with fake browser/7-Zip updates and TAG-124 TDS, spreading NetSupport RAT in a multi-pronged infection campaign.

Malicious phishing apps are bypassing Google Play Store security, tricking users into revealing crypto wallet seed phrases and draining funds. Beware and never share your seed

Censys uncovers "sostener.vbs," an obfuscated VBScript launching a multi-stage RAT delivery pipeline, affecting dozens and potentially linked to Blind Eagle APT.

Infoblox unmasks VexTrio, a sprawling malicious adtech ecosystem intertwined with DNS-based malware campaigns and global website compromises, fueled by commercial operators
Attackers are hijacking expired Discord invite links, redirecting users to malicious servers that deploy AsyncRAT and crypto-stealing Skuld Stealer via clever social engineering.

CISA warns of active exploitation of a SimpleHelp RMM flaw (CVE-2024-57727) by ransomware actors, impacting utility billing software providers and their customers.

TeamFiltration is being actively exploited in UNK_SneakyStrike, targeting over 80,000 Microsoft Entra ID accounts with password spraying and data exfiltration.

BrowserVenom malware is spreading via fake DeepSeek-R1 Google Ads, installing a proxy implant that hijacks all browser traffic. Beware of fake LLM installers.

HelloTDS is a sophisticated traffic direction system delivering millions to FakeCaptcha and other malware via advanced fingerprinting and evasive tactics.

Clicking unsubscribe links can be risky, confirming your email is active or leading to phishing. Use email client features or block senders to stay safe.

Interpol and Asian law enforcement blocked 20,000 malicious IPs and seized 41 servers in a major takedown of information-stealing malware infrastructure.

A new Sekoia report reveals a surge in AitM phishing, leveraging industrialized PhaaS kits to bypass MFA and compromise Microsoft 365 and Google accounts.

Rapid7 reveals BlackSuit ransomware affiliates are adopting Black Basta tactics, using email bombing, fake Quick Assist scams, and evolving Java RATs.

Silent Push uncovers "GhostVendors," a massive online fraud operation using 4,000+ fake domains and Facebook ads to impersonate brands and scam consumers.

An international operation led by JC3 and Microsoft DCU has dismantled a large tech support scam ring in India, primarily targeting elderly Japanese citizens.

SentinelLABS exposes China-nexus APTs (ShadowPad, PurpleHaze) targeting SentinelOne and over 70 organizations in extensive cyber-espionage.