
 Do Son
Europol and allies arrested 5, dismantling a global crypto investment fraud ring that laundered €460M from 5,000+ victims, exploiting Hong Kong banking networks.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.

A new Snake Keylogger campaign exploits an undocumented DLL sideloading technique via jsadebugd.exe to target energy and logistics sectors with fake oil deals.

Varonis uncovers a widespread phishing campaign abusing Microsoft 365's Direct Send, spoofing internal users to bypass email security and harvest credentials.

Notorious hacker "IntelBroker" (Kai West) has been arrested, traced by the FBI through his crypto transactions. He's charged with stealing and selling data, causing $25M in damages.

Arctic Wolf Labs reveals UAC-0226 is using evolving GIFTEDCROOK malware in cyber-espionage against Ukrainian military and government, exfiltrating sensitive documents
A sophisticated campaign is exploiting AI tool popularity via Black Hat SEO to poison search results, delivering Vidar, Lumma, and Legion Stealers to unsuspecting users.

Iranian APT "Educated Manticore" (APT42) uses AI-assisted spear-phishing via email/WhatsApp to target critics with React-based phishing kits, bypassing MFA and stealing credentials.

North Korean APTs are using 35 typosquatted npm packages and fake job offers to spread HexEval, BeaverTail, and InvisibleFerret malware, stealing crypto and data from developers.

Palo Alto Networks exposes CL-CRI-1014, an IAB targeting African financial institutions. They use open-source tools like PoshC2 and Classroom Spy, disguised with forged signatures for covert network access.

Trellix uncovers "OneClik," a sophisticated APT campaign abusing Microsoft ClickOnce and AWS cloud services to deploy Go-language backdoors, targeting energy, oil, and gas sectors.

Dire Wolf, a new Golang ransomware, is targeting manufacturing/tech in 11 countries. It uses double extortion, deletes backups, and has a "wipe mode" that permanently destroys files.

SecurityScorecard's STRIKE team exposes "LapDogs," a covert China-Nexus ORB network with 1,000+ infected SOHO devices, using the custom ShortLeash backdoor for cyberespionage.

Taiwan's BitoPro exchange confirms North Korea's Lazarus Group stole $11.5M in crypto via phishing an employee and bypassing MFA on AWS infrastructure.

Hackers are weaponizing legitimately signed ConnectWise ScreenConnect installers by using Authenticode stuffing to deploy malware and fake updates, leveraging social engineering.
North Korean APT Kimsuky is using GitHub private repos, Dropbox, and XenoRAT malware via spearphishing to compromise victims and conduct cyber-espionage.
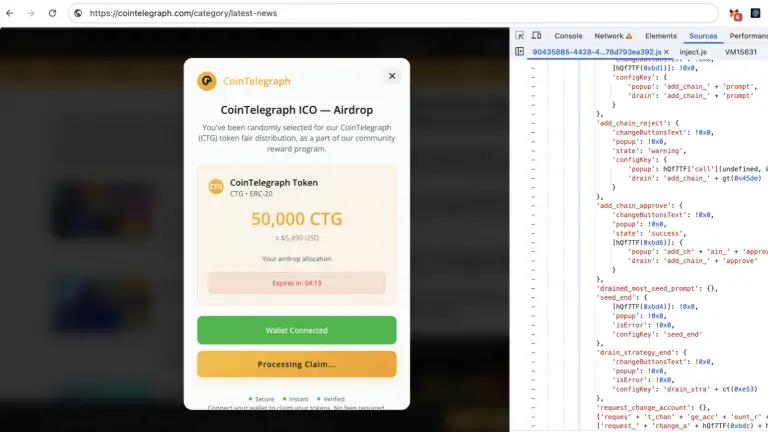
CoinTelegraph was hacked on June 22, 2025, with attackers injecting malicious JavaScript to display fake CTG airdrop pop-ups, stealing crypto by draining connected wallets.

CoinMarketCap suffered a client-side attack on June 20, 2025, using a fake "doodle" graphic to deliver Inferno Drainer, stealing over $43,000 from user wallets.

Cloudflare successfully mitigated a record-breaking 7.3 Tbps DDoS attack in May 2025, delivering 37.4 TB in 45 seconds with no service disruption.

Shadow Vector campaign uses malicious SVGs in phishing emails to deliver AsyncRAT & RemcosRAT in Colombia, leveraging advanced DLL sideloading and in-memory execution.

A new crypto scam impersonates European tax agencies, luring victims with fake tax emails to steal crypto via seed phrase theft or malicious Web3 transactions

Scammers hijack Google ads & brand websites to show fake support numbers. Malwarebytes exposes this new "search hijacking" scam tactic.

The SERPENTINE#CLOUD campaign exploits Cloudflare Tunnel subdomains and LNK files to deliver in-memory RATs like AsyncRAT and Remcos, evading detection.