 Do Son
A suspected supermarket freezer hack altered refrigeration units to 50C across Sweden, Belgium, and Estonia, spoiling food and forcing store closures.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
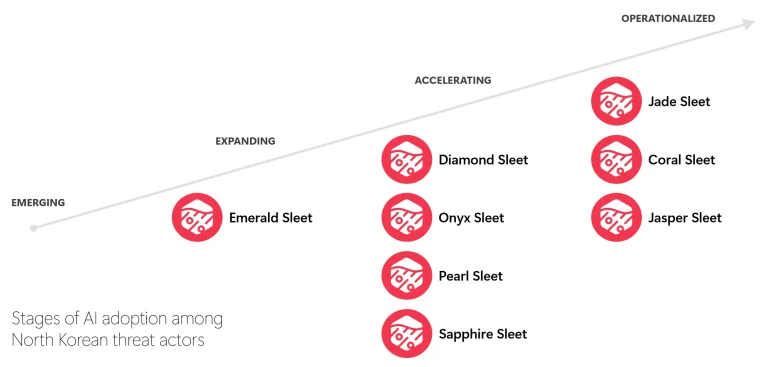
Microsoft reveals how North Korean threat actors use tools like ARTEX. See how AI-enabled North Korean threat actors speed up cyber operations.
The Binance hack investigation reveals a $6.3B breach tied to TraderTraitor, prompting massive stablecoin freezes and an infrastructure overhaul.

A Polymarket supply chain attack compromised a third-party analytics script to deploy a crypto wallet drainer, prompting an immediate trading halt.
A suspected Binance hot wallet breach prompted emergency investigations as issuers froze over $2.3 billion in stablecoins amid massive token outflows.
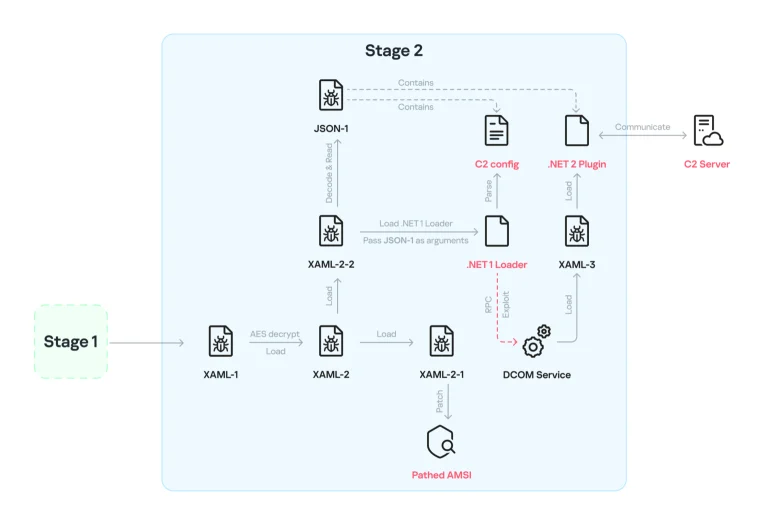
NetamLoader, a new XAML-based .NET loader, points to a supply chain attack on a custom Windows build used by government entities in Asia.
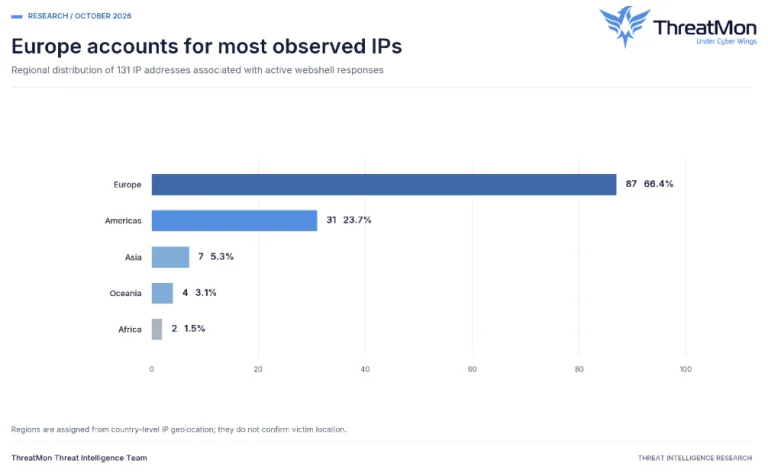
An exposed workspace shows AhsayCBS webshell access turned into SOCKS proxy tunnels with Chisel and GOST across 141 hosts, per the logs.
Hackers reduced the GMO Internet ransom demand from $50M to $1M and leaked victim files after the Japanese conglomerate ignored multiple bug warnings.
Cisco Talos uncovered the KeyDrift malware UAT-11473 campaign exploiting CVE-2026-20127 to steal IPsec keys from Cisco SD-WAN controllers.
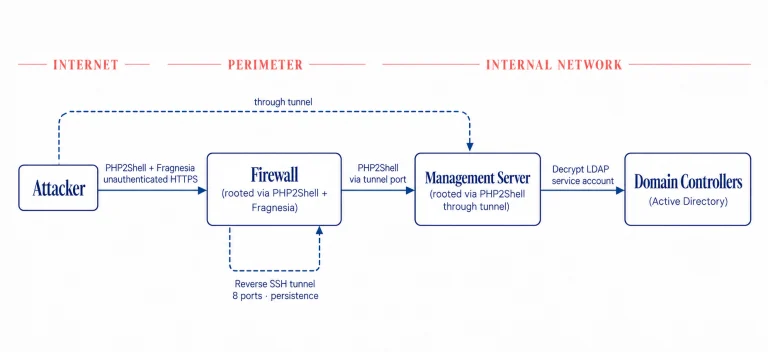
Dream researchers uncovered a Chinese-nexus PHP2Shell exploit Fragnesia chain that rooted 25 firewalls and breached a US government Active Directory.
A Hive ransomware affiliate who also used Nefilim ransomware got 70 months in prison. A co-conspirator remains at large with an $11M reward.
Wiz Research uncovered the Gheist campaign, a Gheist GitHub campaign planting 13,500 rogue branches across 850+ accounts to steal private repo secrets.
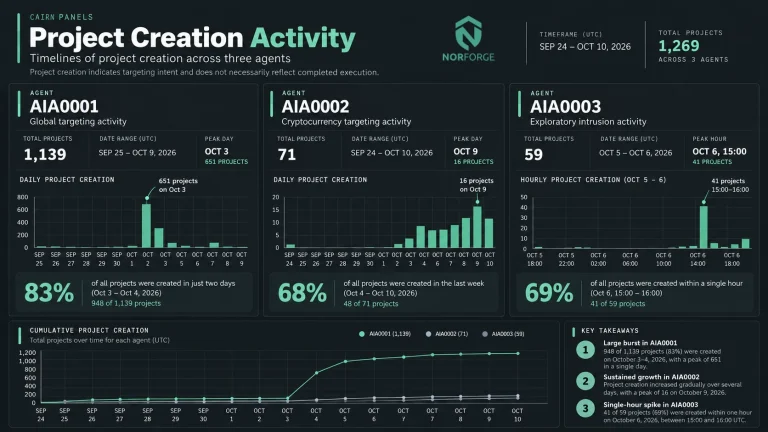
NorForge uncovered 20+ exposed Cairn AI panels showing how threat actors use the Cairn AI hacking tool to breach e-commerce and payment sites.
A devastating GMO Desktop Cloud breach compromised over 26,000 servers, exposing FX trading accounts and prompting a full infrastructure shutdown.
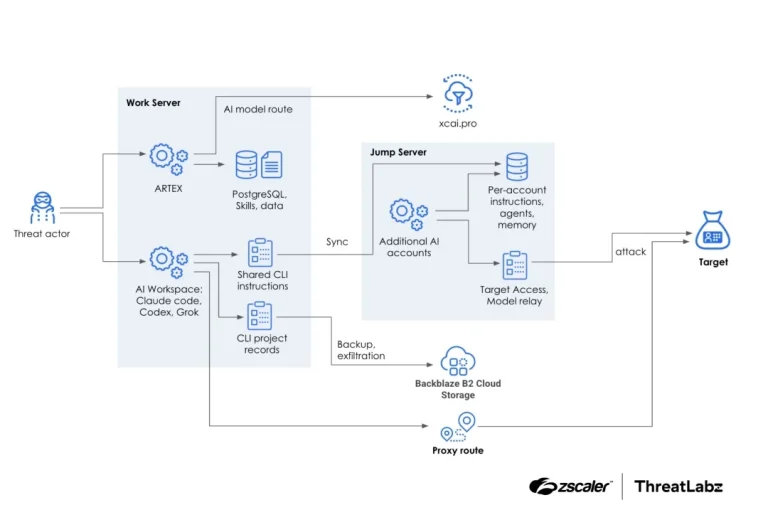
Zscaler ThreatLabz exposes a global ARTEX AI hacking campaign. See how an operator used ARTEX AI hacking tools, DeepSeek, GLM, and Grok to steal data.
DOJ officials announced a Cambodia crypto scam extradition after Zheng Zhao allegedly helped launder $36.9M stolen from 174 US victims via USDT.
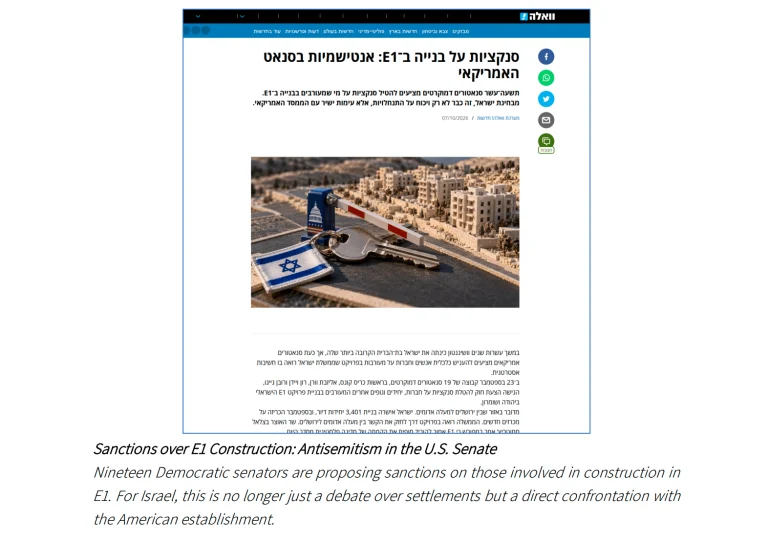
ClearSky exposed the Russian Doppelganger campaign in Israel using 76 fake Walla articles, 66 redirect domains, and AI poisoning ahead of elections.
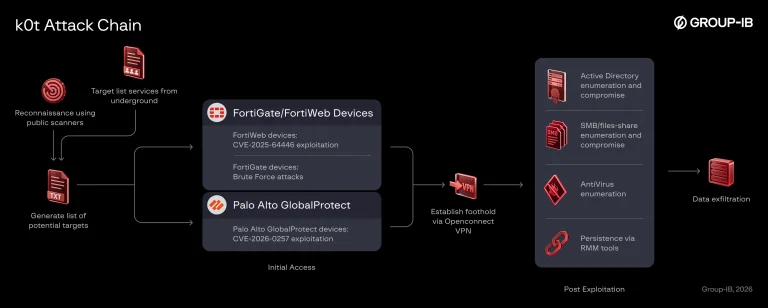
A suspected initial access broker behind FortiGate GlobalProtect attacks exposed 70,000+ credentials. See how k0t operates and how to defend.
An ARTEX AI agent campaign against IT and software vendors overlaps with Storm-0940, targeting Okta, Entra ID, and AWS Cognito logins.
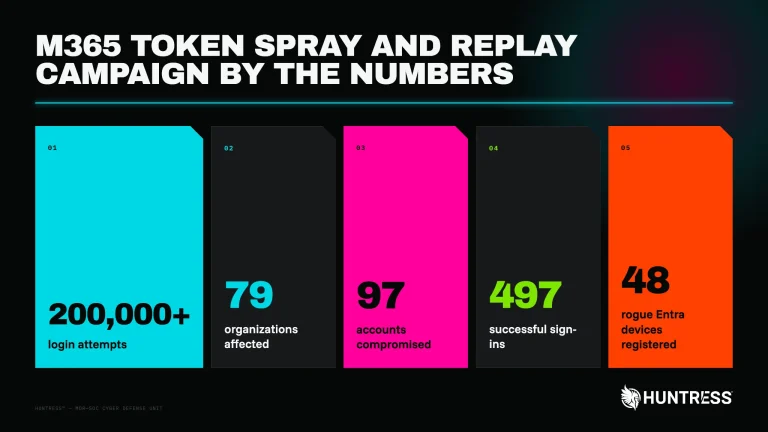
A token replay attack hit 79 organizations, bypassing MFA to set up Microsoft 365 BEC with rogue devices and hidden inbox rules.
Operation Serengeti III, an INTERPOL-led Africa cybercrime crackdown, led to 1,462 arrests and more than USD 105 million recovered.

Kaspersky uncovered the BlackX UEFI bootkit APT41 campaign bypassing Secure Boot via Baton Drop to spy on Central Asian diplomatic agencies.