
 Do Son
Explore how the Operation RapidRust APT36 malware campaign by Zscaler ThreatLabz exposes new tools like RUSTYSHADE and RUSTYMOVE targeting governments.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
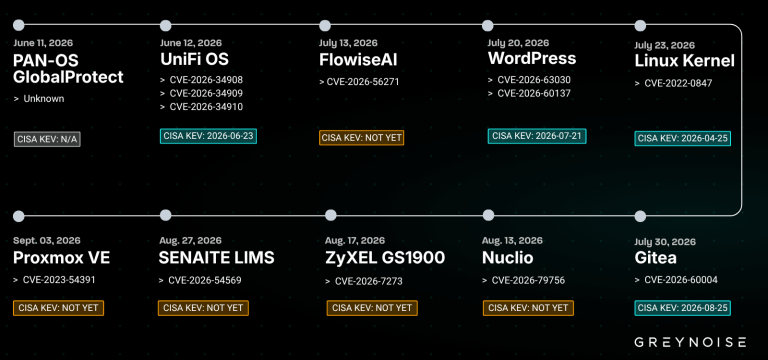
New Kapibala WordPress exploitation attacks steal records. GreyNoise warns that Kapibala WordPress exploitation hits governments.
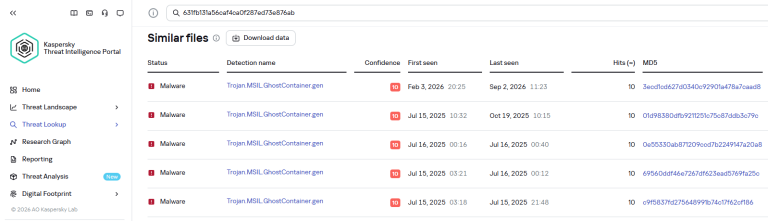
Learn how the NightEagle APT GhostContainer attacks exploit Exchange servers in Russia. Protect your network from the NightEagle APT.
Discover how a Google undercover analyst successfully infiltrated the TeamPCP hacking gang to prevent massive supply chain attacks and secure corporate data.
Security researchers uncovered the new PAPERMILL cybercrime cluster. Learn how the PAPERMILL cybercrime cluster uses tax lures to deploy VenomRAT.
A new Tajin Group phishing network emerged on Telegram. Discover how Tajin Group money laundering fuels illicit guarantee marketplaces across the globe.
Security researchers uncovered a new GhostCode phishing kit. Learn how the GhostCode phishing kit bypasses MFA to hijack enterprise Microsoft 365 accounts.
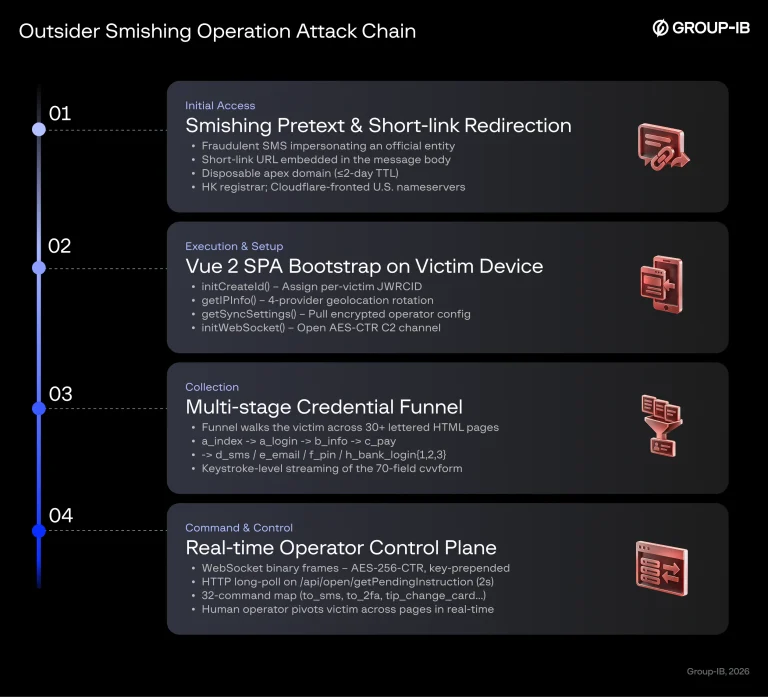
Group-IB exposed a new Smishing Triad phishing kit used by Outsider. Learn how this Smishing Triad phishing kit steals financial data worldwide.
Silent Push uncovered a North Korean IT worker scam recruiting proxies. Learn how a North Korean IT worker uses Discord to bypass corporate hiring filters.
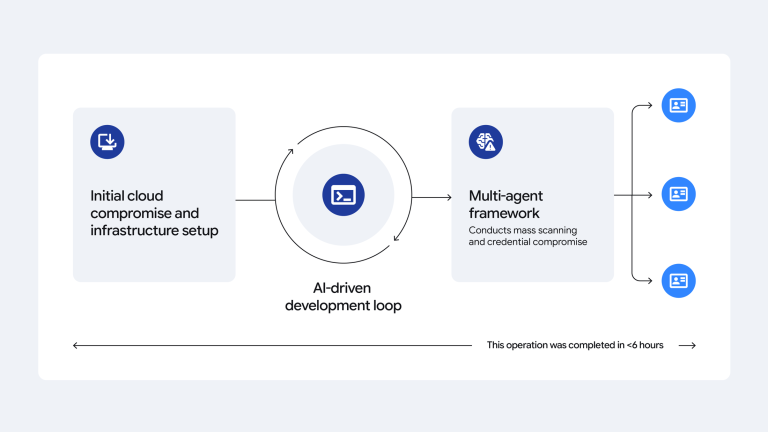
Discover how adversarial AI threats fuel massive AI credential harvesting operations. Attackers use automated agents for fast cyber crime campaigns.

A sophisticated phishing campaign uses redirect chains to abuse Google infrastructure. Learn how attackers abuse Google infrastructure to steal credentials.

An active SonicWall SMA 1000 campaign breached a UK council. Learn how the SonicWall SMA 1000 campaign exposed Active Directory records worldwide.

A Conti ransomware developer sentenced to prison for wire fraud conspiracy. Learn how this Conti ransomware developer faces justice.
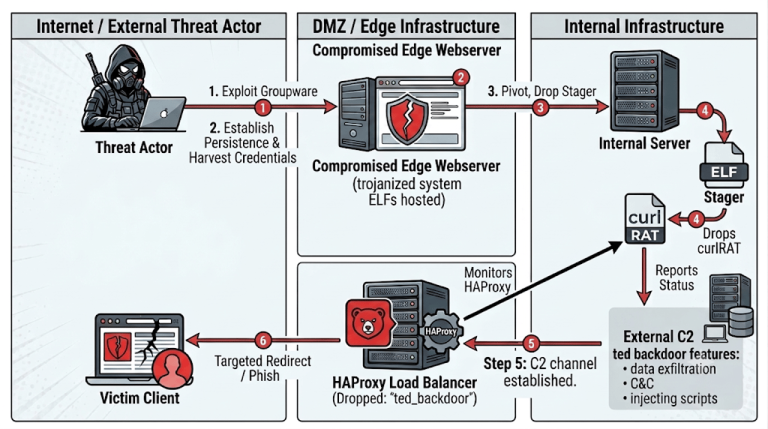
The ted backdoor is DPRK Linux malware hidden inside HAProxy. It pairs with curlRAT to spy on South Korean media and automotive firms, Rapid7 reports.
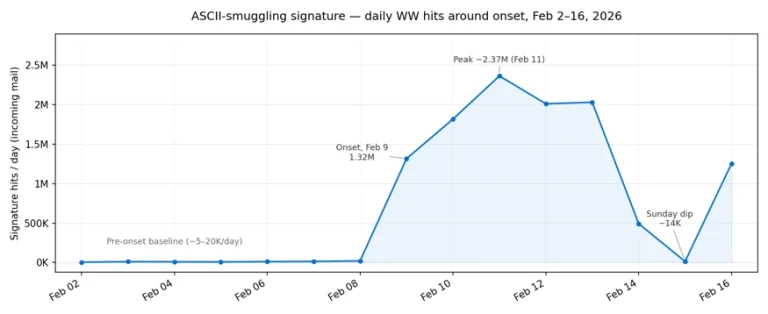
Microsoft uncovered an ASCII smuggling phishing evasion campaign hitting email inboxes. Learn how attackers weaponize invisible Unicode tags.
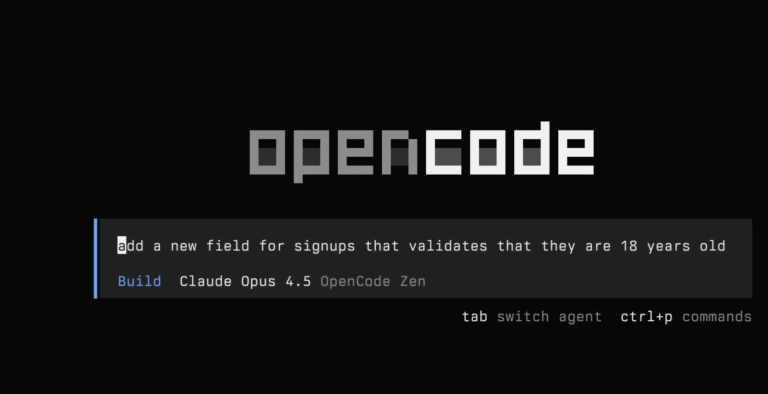
Threat analysts reveal Kimsuky uses AI agent opencode to mass-produce phishing decoys. Discover how the group leverages AI to enhance its LNK attacks.
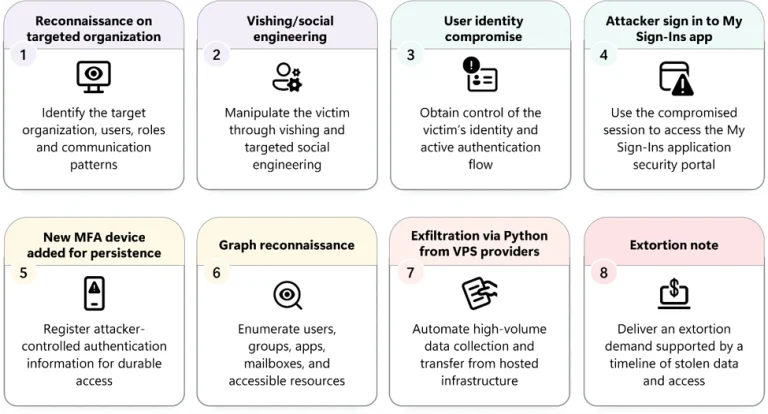
Microsoft warned of passkey social engineering attacks hitting tenants. Learn how passkey social engineering targets enterprise cloud identities.
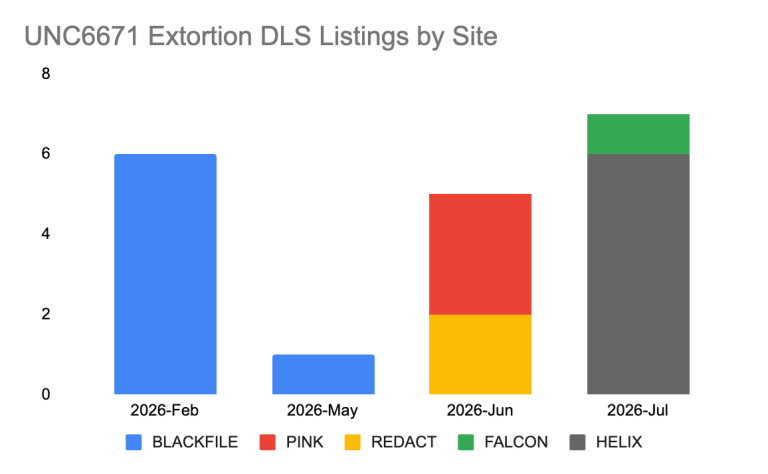
Discover how the PREY-0058 extortion campaign uses Microsoft 365 vishing attacks and AiTM tactics to bypass MFA, steal cloud data, and demand high ransoms.
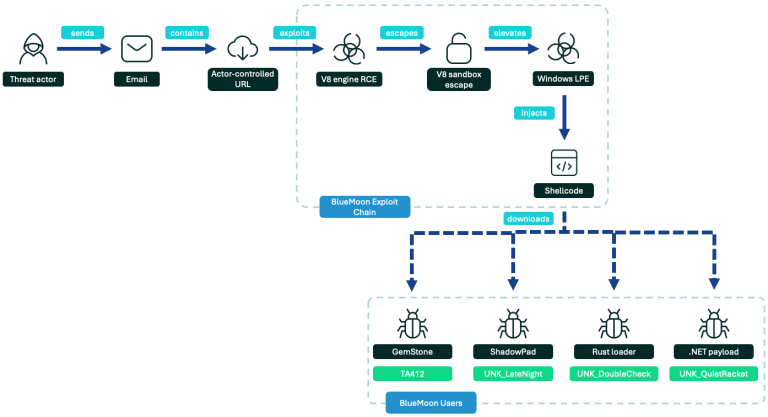
Espionage groups use the BlueMoon exploit kit in new attacks. Discover how BlueMoon exploit kit campaigns exploit Chrome zero-days.
Security teams uncovered trojanized fake macOS installers tied to North Korean campaigns that deploy OtterCookie malware on Apple devices.
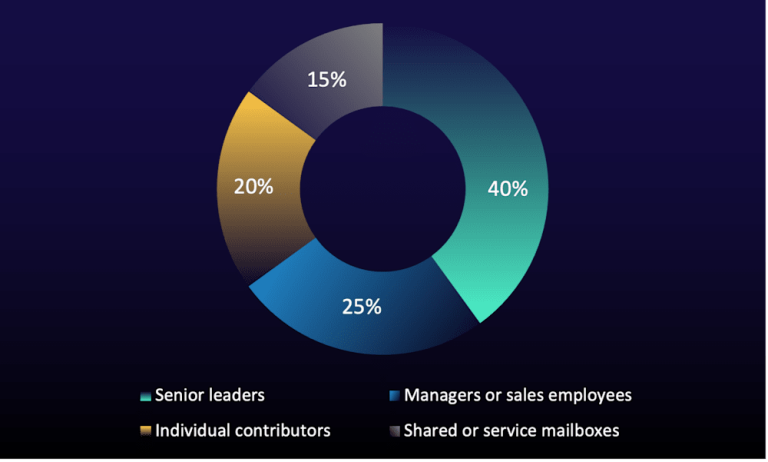
A Microsoft 365 RejectDirectSend bypass lets attackers spoof internal emails. Learn how this RejectDirectSend bypass works and how to protect your tenant.

Unit 42 exposes AI-powered cyberattacks across Latin America, where LLM-assisted actors hit government, water, and financial targets.