 Do Son
Google warns the BREEZE COMET threat actor attacks Brazilian banks to execute mass financial fraud. Learn how to protect your payment systems.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
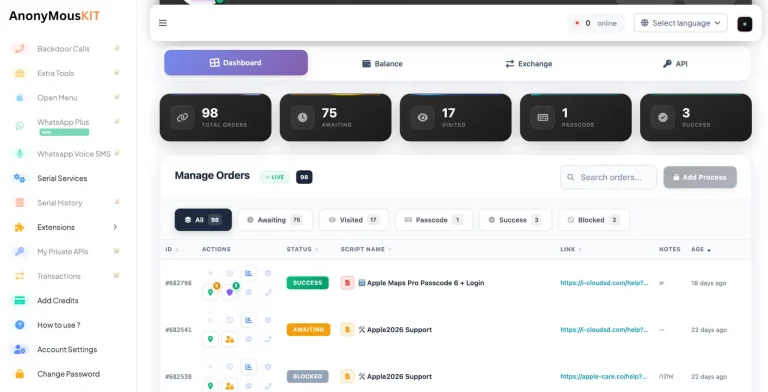
AnonyMousKIT is an AI-powered PhaaS platform that phones iPhone theft victims as fake Apple Support to steal passcodes and beat Activation Lock.
Kaspersky uncovered a ValleyRAT backdoor adware campaign using signed wallpaper apps to drop malware. Learn how to protect your systems.
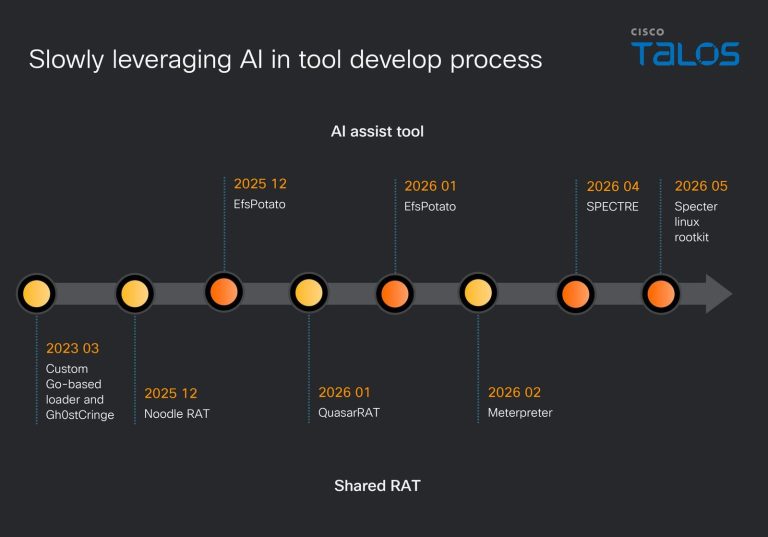
Cisco Talos reveals that Chinese-speaking threat group UAT-10147 deploys the SPECTRE cross-platform implant with Linux rootkits and BYOVD capabilities.
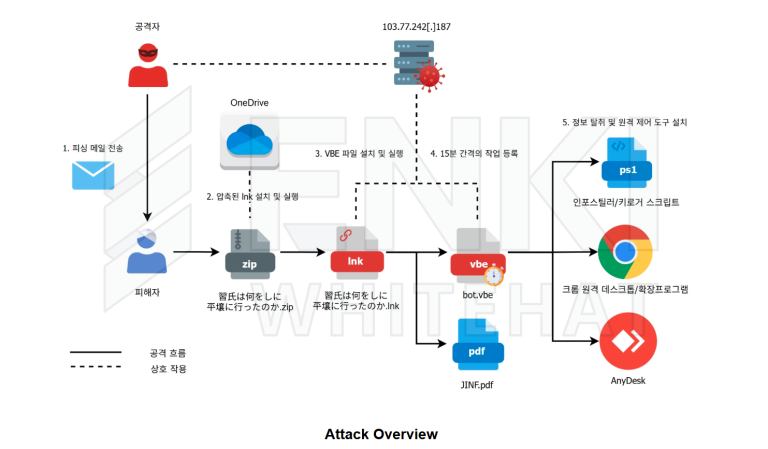
Recent Kimsuky spear phishing campaigns abuse remote control tools and AI extensions to target victims in Japan and South Korea. Read the full analysis.
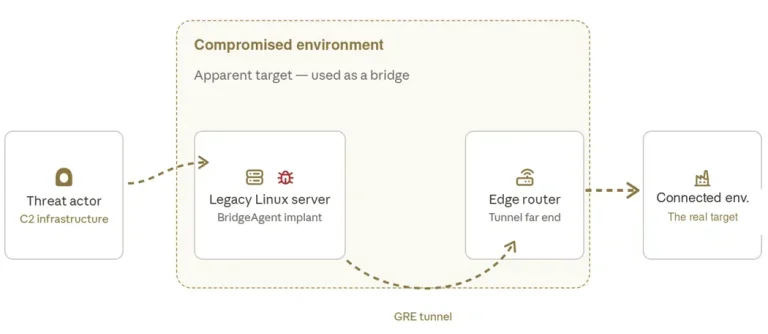
The Fire Ant threat actor uses trusted infrastructure compromise to breach high-value targets. Discover how this group evades detection in networks.
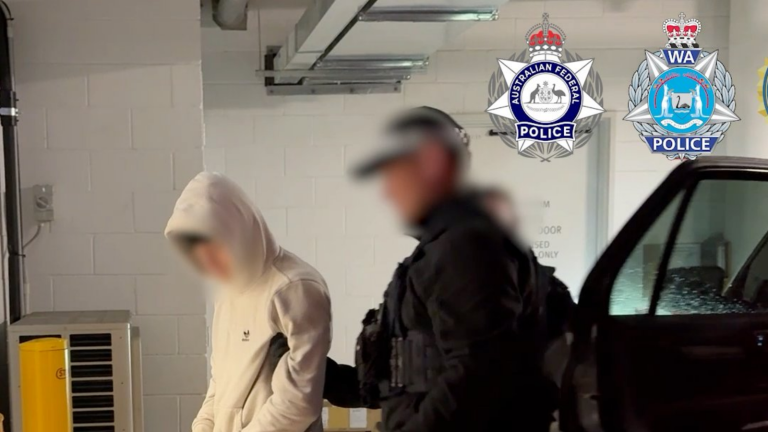
Discover the details of the TeamPCP hackers arrested in Australia for executing devastating open-source supply chain attacks using the Mini Shai-Hulud worm.
The DOJ and FBI seized QScan and QTRouter, platforms run by China state-sponsored hackers to hide attacks on U.S. critical infrastructure.
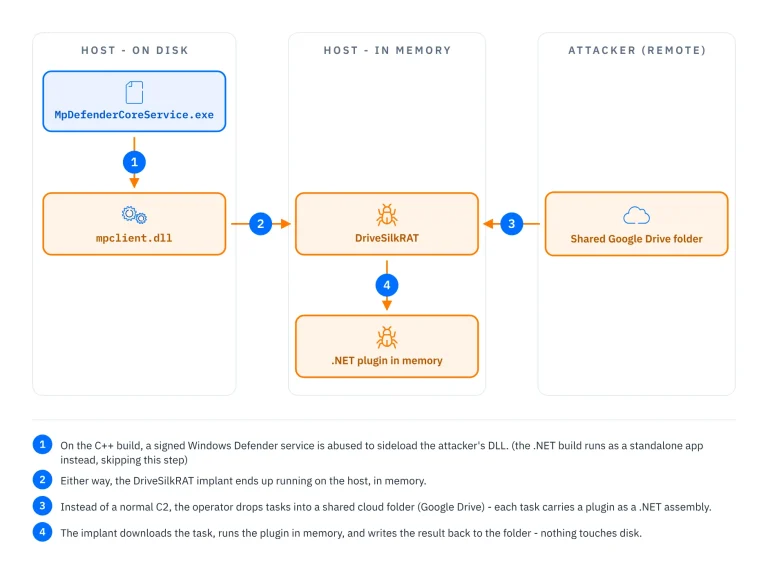
SilkParasite APT ran China-nexus cyberespionage across Central Asia, using 7 custom RATs, DLL sideloading, and AI-assisted malware.

Operation CameraSwarm compromised 14,500+ Dahua cameras in 35 days. Hunt.io traced the camera hacking campaign to an exposed operator directory.
CoreRAT malware powers Core Werewolf attacks on Russian defense and government targets, using fake military PDFs and Telegram phishing.
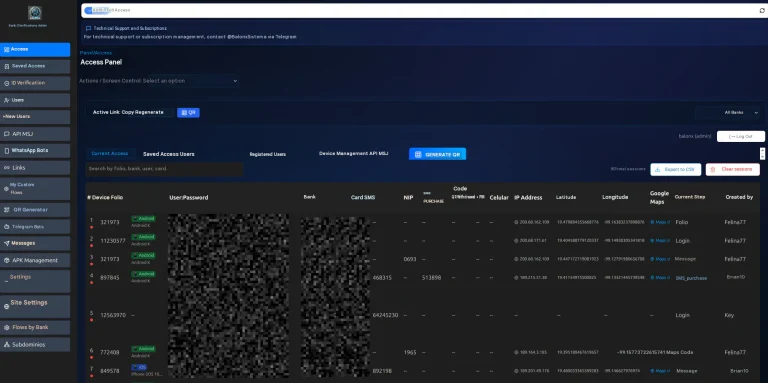
Group-IB exposed Balonx Sistema, a Mexican PhaaS platform bundling real-time phishing, an Android RAT, and AI-driven vishing against 20+ banks.
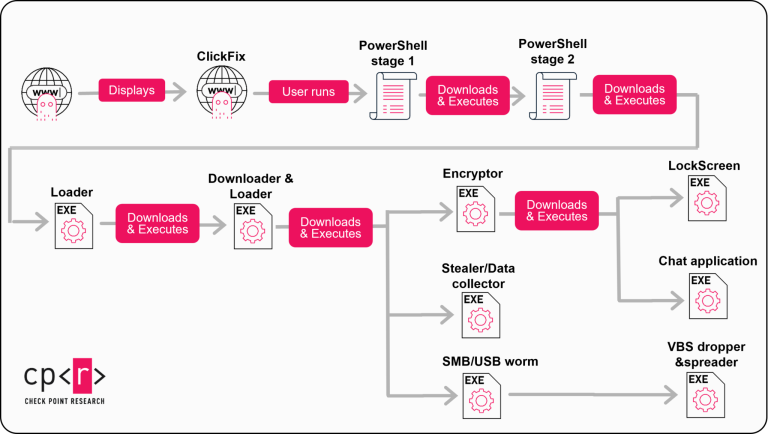
StopAndProtect malware turns hacked WordPress sites into a botnet for ransomware and data theft. Check Point exposed 5,000+ victims.
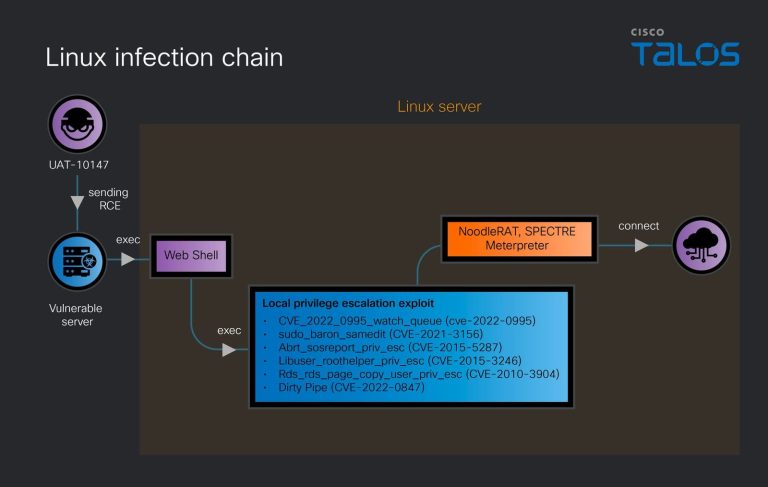
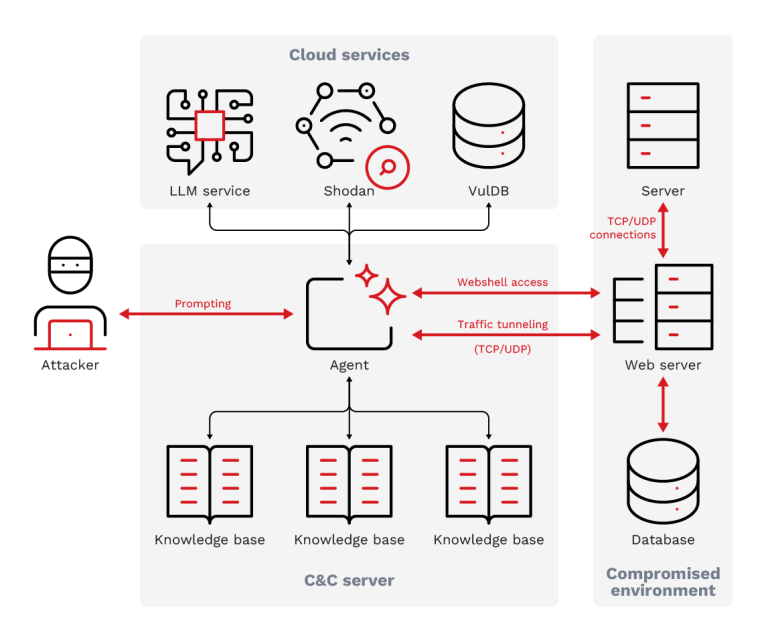
Cisco Talos revealed how UAT-10147 agentic AI attacks target global servers. Learn how UAT-10147 agentic AI tools automate intrusions and data theft.
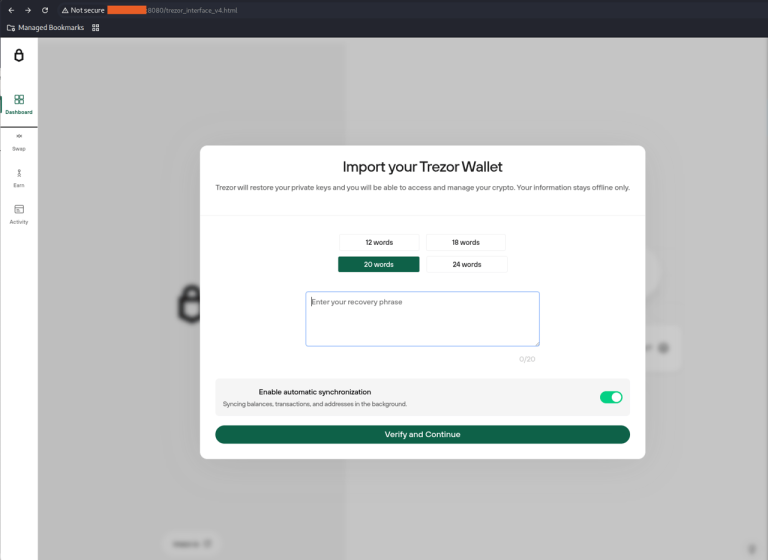
Rapid7 exposed Operation ASTERIX, a crypto fraud operation using AI, vishing, and fake wallet apps to steal seed phrases from validated holders.
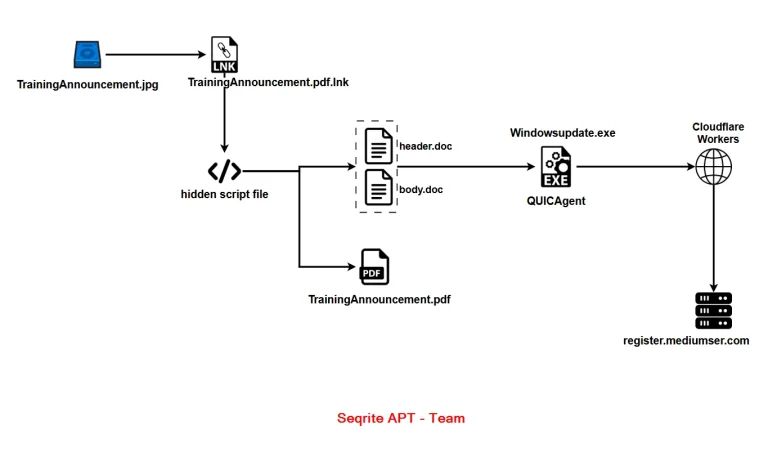
Seqrite links Operation QUICSILVER to a China-nexus actor deploying the QUICAgent Go backdoor against Myanmar government targets via a VHD lure.
A Rust supply chain attack poisoned arrayref and two other crates to run malware at build time. Wiz ties the infrastructure to DPRK campaigns.
The Jewelbug APT group runs espionage alongside cryptocurrency scams. Read our report on Jewelbug APT group operations.

Cisco Talos discovered the JWR phishing framework, a new PhaaS variant. Read our JWR phishing framework analysis to learn about this real-time cyber threat.

CISA and the NSA warn of an active Siemens PLC cyber threat using AI-generated exploit scripts disguised as monitoring tools. Protect your OT now.

Acronis ties a new PATCHCORD malware APT36 campaign to Afghan telecom and Indian targets. SHEETCORD malware abuses Google Sheets for C2.

Kaspersky uncovered the new HoneyMyte CoolClient rootkit. The HoneyMyte CoolClient rootkit deploys a kernel driver to hide malware on Windows.