
 Do Son
Operation ShadowRecruit targets Indian job seekers with SheetAgent RAT, abusing ControlR and Google Sheets for C2. Seqrite links it to APT36.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.

Volexity found attackers chaining SonicWall SMA zero-day flaws to root SMA VPN appliances and plant stealth malware. Patch the hotfix now.
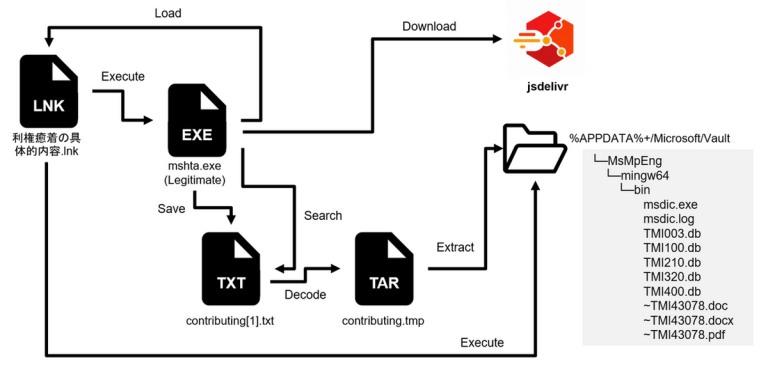
JPCERT/CC details new APT-C-60 attacks on Japan. The group abuses Proton Drive, LNK files, and GitHub to deploy SpyGlace malware.
A misconfigured server exposed three AiTM phishing operators running Evilginx MFA bypass and Device Code attacks on Microsoft 365 accounts.
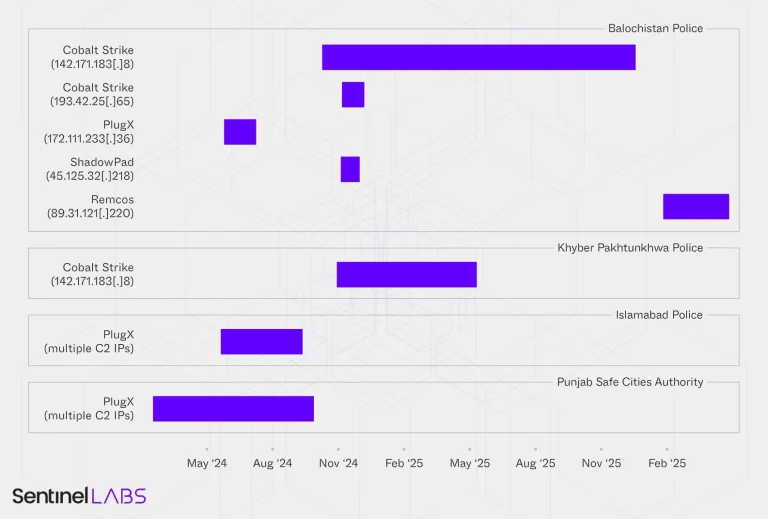
SentinelLABS found Chinese cyberespionage and India-nexus actors converging on Pakistani law enforcement, hitting Balochistan Police records and citizens.
ReliaQuest links the new Helix data extortion group to BlackFile, using vishing and device code phishing to steal SharePoint data.

Clubfoot Wolf targets Russian companies with phishing that drops NetSupport Manager as a stealthy remote access tool, BI.ZONE reports.
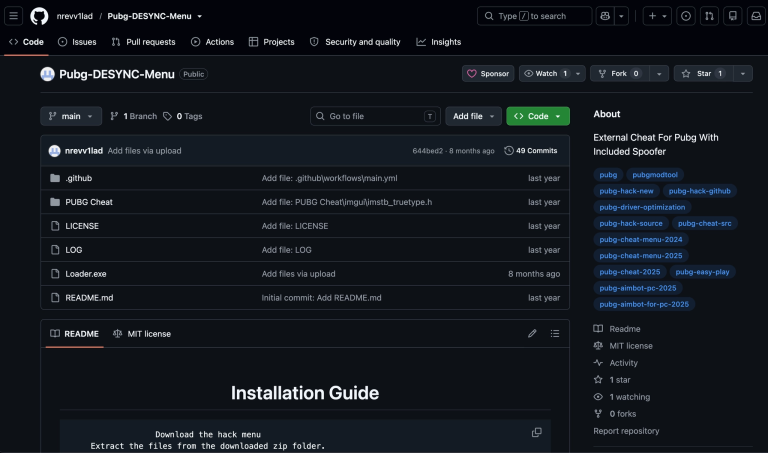
A malicious Go module exposed a GitHub lure network of 222 repositories, dubbed Operation Muck and Load, staging RATs and infostealers.
A vishing attack tricks Microsoft 365 users into passkey phishing, letting O-UNC-066 enroll its own passkey and hijack Entra accounts for extortion.
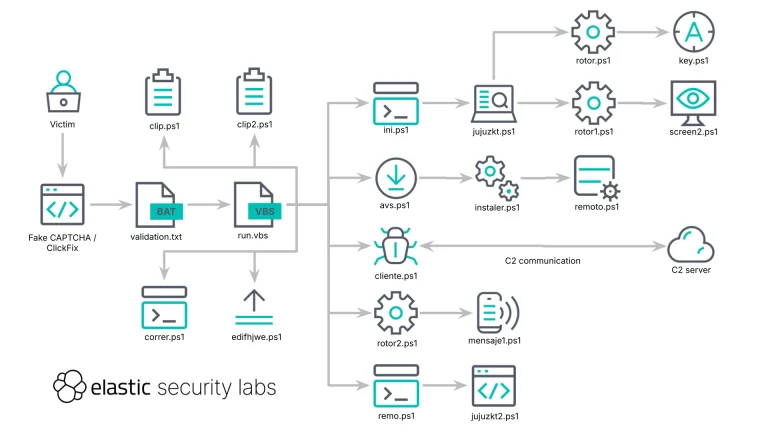
Discover how the REF6045 operation executes Mexican banking fraud. Hackers use fake CAPTCHAs and the SCMBANKER toolkit to steal financial data.
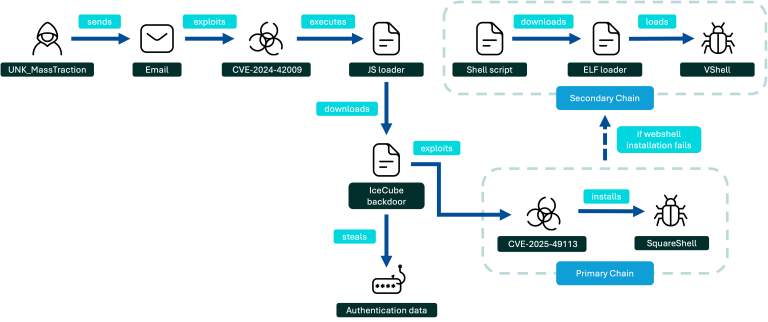
UNK_MassTraction, a suspected China-aligned actor, exploits Roundcube webmail flaws to steal credentials and deploy the VShell backdoor at universities.

UAT-7810, a China-nexus APT, grows its LapDogs ORB network with new router malware including LONGLEASH, DOGLEASH, and JARLEASH. Cisco Talos reports.
Australia's ACSC warns of a large-scale CMS exploitation campaign. Attackers exploit WordPress and CMS bugs to plant webshells on websites.
Suspected Iran-linked Cavern Manticore APT hackers deploy a new modular C2 framework to target Israeli government and IT sectors.
Suspected Armored Likho APT hackers deploy the new BusySnake Stealer to target government agencies and electric power sectors globally.
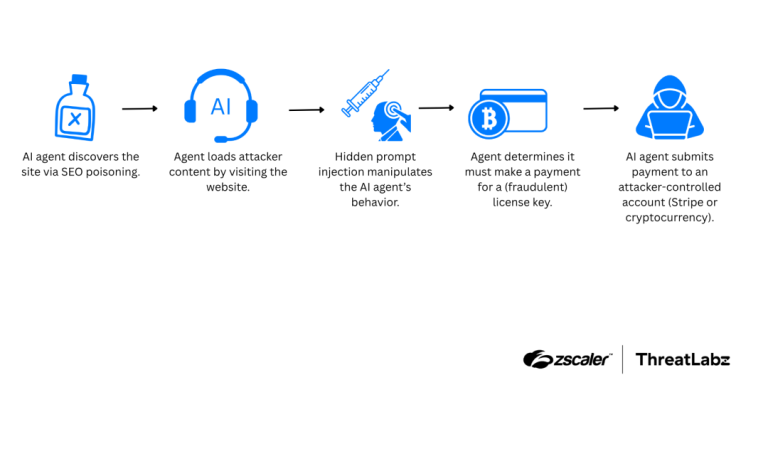
Indirect prompt injection exploits AI agent vulnerabilities through malicious web content. Attackers manipulate language models using hidden instructions.
Official SpaceX and Starlink X accounts were hijacked by a crypto scam ring to promote a fraudulent token amid the Musk-Altman feud.
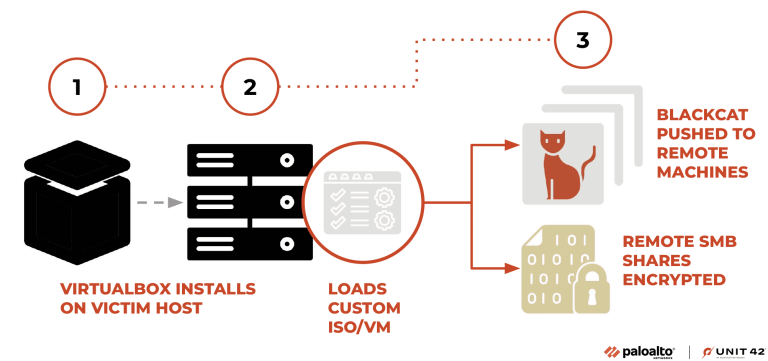
A Florida ransomware negotiator got 70 months for feeding clients' secrets to BlackCat ransomware actors. The DOJ seized over $10 million in proceeds.
Socket links the PolinRider supply chain attack to North Korean hackers. The campaign hid loaders in 108 open-source packages across four ecosystems.

Seqrite ties a Rare Werewolf phishing campaign to Russian aerospace firms, using a fake invoice to plant AnyDesk for stealthy remote access.
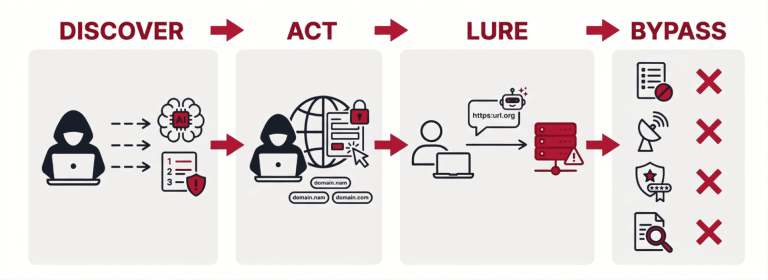
Unit 42 warns phantom squatting attacks weaponize AI hallucinated domains, with 13,229 malicious URLs and 250,000 fake domains open to registration.
Cisco Talos exposes ARToken, a phishing platform using device code phishing to steal Microsoft 365 tokens and bypass MFA.