 Do Son
Authorities dismantled a major crypto laundering service used by ransomware gangs to wash millions. Read about the global AudiA6 dark web takedown.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.

Federal authorities are seizing deepfake porn websites. This historic bust marks a massive win for enforcement of the new TAKE IT DOWN Act.

ShinyHunters leverages a zero-day Oracle PeopleSoft exploit to compromise higher education systems, exposing sensitive data via the CVE-2026-35273 flaw.

Read this Proofpoint cybercrime analysis on the surge of TA4922 malware campaigns targeting organizations globally with advanced evasion tactics.

Discover how stealthy Outlook mailbox theft fueled a 5-month executive espionage campaign at a global stock exchange using trusted cloud tools.

Read the Group-IB phishing report detailing the massive Smishing Error524 campaign targeting millions across 72 countries with advanced evasion tactics.

A massive wave of APAC malvertising scam campaigns floods Meta advertising platforms, targeting health and financial anxieties across 13 countries.

Europol dismantled a counterfeit document production facility in Spain distributing fraudulent identity documents across Europe through an online marketplace.

Europol targets illegal streaming networks run by complex criminal enterprises. The joint action dismantled nine crime groups and removed 27,000 URLs.

The active DriveSurge threat cluster is compromising thousands of websites. Discover how its customized Traffic Distribution System redirects victims.
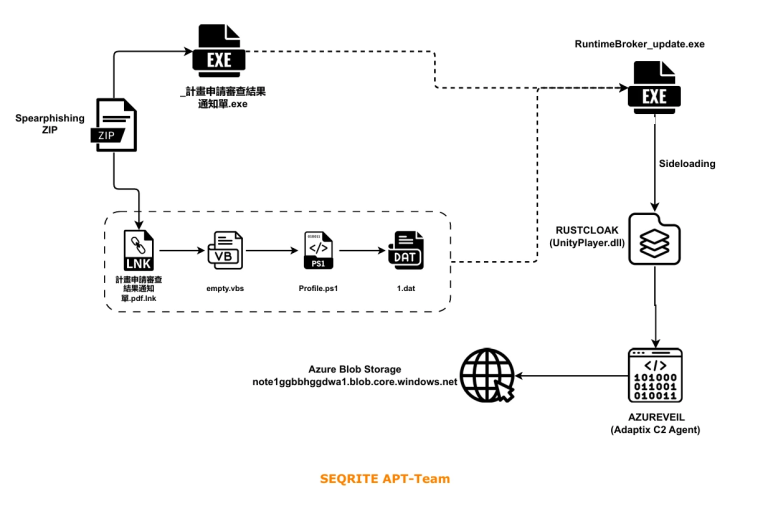
Learn how Operation Dragon Weave uses a dead-drop C2 channel on Azure Blob Storage to target global officials in a new espionage campaign.

Discover how the GREYVIBE threat actor group leverages AI. WithSecure details this Russia nexus threat group targeting Ukraine.
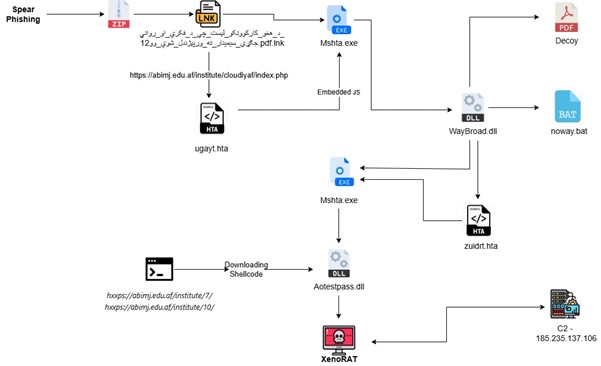
A deep look at the SideCopy XenoRAT malware attack targeting the Afghan Ministry of Finance. Learn how Operation XENOFISCAL bypasses defenses.

Learn how the Kimsuky HttpSpy malware campaign leverages a novel JSONPing execution check to target South Korean networks and evade modern security.

A dangerous macOS cryptocurrency malware wave drives the latest JINX-0164 developer campaign. Learn how to secure your repositories now.

A novel Remcos RAT phishing campaign utilizes a network blackout technique to evade defense systems. Learn how to protect your enterprise network.

Bad actors are running FIFA website spoofing scams. Read the latest FBI World Cup alert to stay safe from fake ticket sites and data theft.

A massive elderly lottery fraud scam broker receives a prison sentence for a DOJ wire fraud conspiracy that targeted millions.

Cybercriminals are ramping up football fan scams and World Cup 2026 fraud. Protect yourself from fake merchandise, phishing, and lottery traps today.

Intrinsec uncovers how abusive bulletproof hosting networks host dangerous malware infrastructure distributing malicious JavaScript payloads.

A Romanian hacker sentenced to prison following an identity theft conviction and selling access to a US government network infrastructure.

Discover how the Chinese PhaaS ecosystem uses real-time interception and AI automation to bypass MFA and exploit digital wallets.