
 Do Son
PRC national Xu Zewei extradited to the US for HAFNIUM intrusions and targeting COVID-19 research. He faces a 9-count indictment for state-sponsored hacks.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
North Korean group HexagonalRodent stole millions in Q1 2026 using AI-generated lures and backdoored VS Code tasks. Protect your Web3 wallet now.
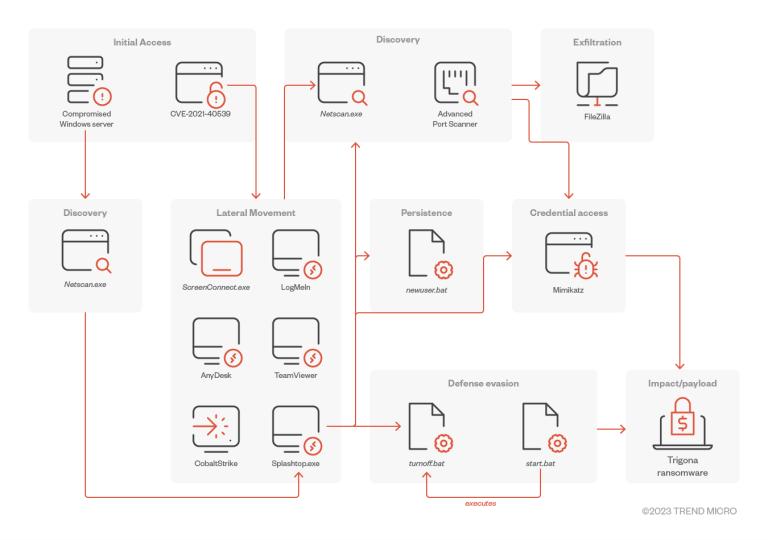
Trigona ransomware swaps Rclone for a custom tool that rotates connections to evade monitoring. Learn how uploader_client.exe powers their data theft.

Cato Networks reveals 235,500+ Modbus probes on PLCs across 70 countries. Learn how attackers fingerprint and hijack industrial control systems. Patch now.

Dabai Guarantee emerges as the new hub for Chinese cybercrime, using Telegram and "ghost-tapping" to coordinate global retail fraud and USDT money laundering.

Dr. Tube’s AI-assisted Bissa scanner exploited 900+ companies using React2Shell (CVE-2025-55182) to steal 30,000 .env files. See the AI-led attack workflow.

Tropic Trooper's 2026 campaign uses trojanized SumatraPDF and VS Code tunnels for stealthy East Asian espionage. Learn how to defend your infrastructure.
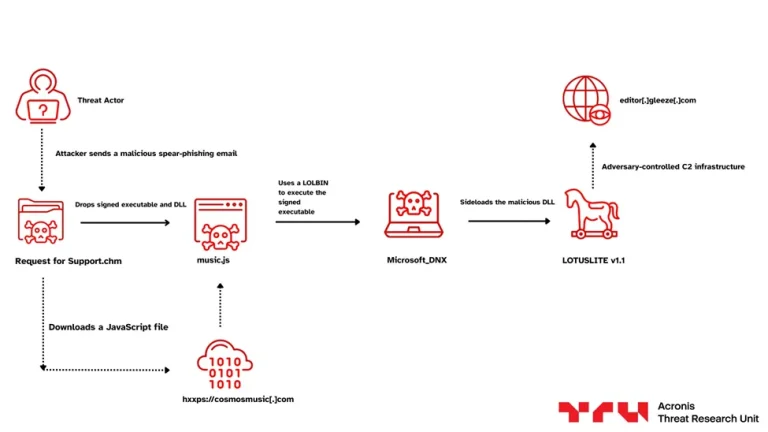
Mustang Panda targets India’s financial sector with the LOTUSLITE malware. Learn how this DLL sideloading campaign bypasses defenses for cyber-espionage.

Microsoft warns of a Teams campaign using fake IT support to hijack workstations via Quick Assist, move laterally with WinRM, and steal data using Rclone.

Former ransomware negotiator Angelo Martino pleaded guilty to working with BlackCat to extort his own clients. $10M in luxury assets seized. Facing 20 years.

Tyler Buchanan pleads guilty in US court for an $8M cyber heist. Discover how SMS phishing and SIM swapping bypassed 2FA to drain corporate & crypto assets.

Proofpoint monitors a 30-day supply chain attack using "signing-as-a-service" to bypass Windows security. Protect your load boards and fleet payments now.

A new QR code "drainer" targets Trust Wallet users on Telegram. It exploits the ERC-20 approve mechanism to wipe USDT. Learn how to protect your assets now.

North Korea's UNC1069 uses fake video calls and "ClickFix" prompts to drain crypto assets and record victims for deepfakes. Audit your meetings now!
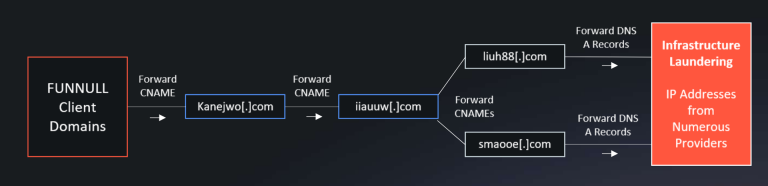
Triad Nexus has built a $300M fraud engine using "Infrastructure Laundering" on AWS and Google. See how they use geo-fencing and CNAME chains to evade the law.
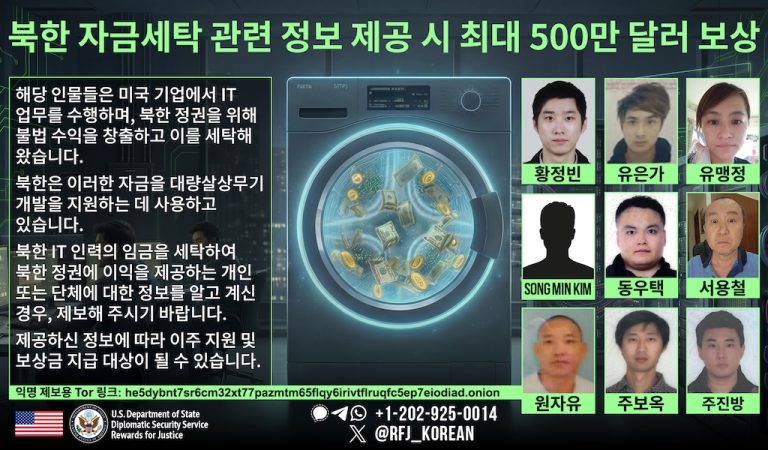
Two NJ residents sentenced for running a "laptop farm" allowing North Korean workers to infiltrate 100+ U.S. companies and steal $5M in revenue.
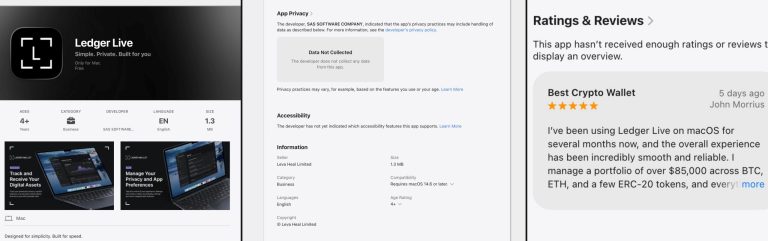
A malicious fake Ledger Live app on the Mac App Store has stolen $9.5M from users. Learn how the scam bypassed Apple's security and why your seed phrase is at risk.
Proofpoint warns that 10% of M365 account takeovers use malicious mailbox rules to steal data and hide alerts. Secure your cloud identity—check your rules!
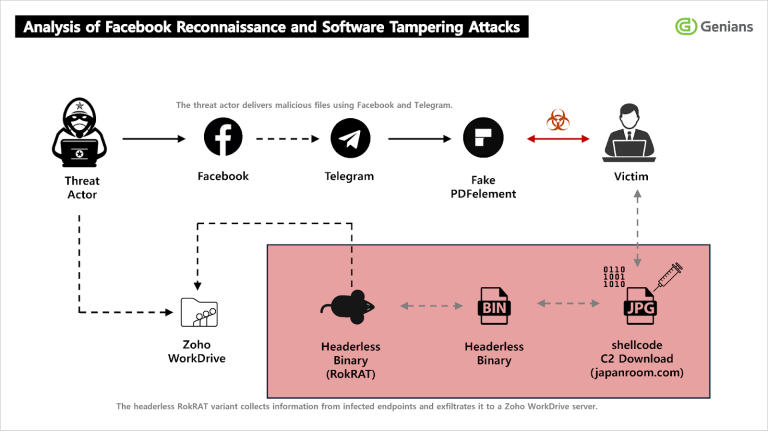
APT37 pivots to Facebook social engineering, using Wondershare PDFelement "code caves" to deploy RokRAT. Learn how they bypass EDR with memory-only payloads.

North Korea’s "graphalgo" campaign uses fake job interviews and real Florida LLCs to infect developers. Learn how to spot this sophisticated state-sponsored trap.
The FBI and Indonesia dismantle W3LL, a $20M phishing kit that bypassed MFA and hijacked live sessions. Learn about the takedown of this MaaS powerhouse.

Microsoft DART uncovers Storm-2755, a "payroll pirate" using AiTM traps and SEO poisoning to steal salaries. Protect your organization from this MFA bypass.