 Do Son
North Korean group UNC1069 (BlueNoroff) targets Web3 with fake Zoom/Teams links. 164 domains blocked. Secure your crypto assets and browser extensions now!
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.

Cisco Talos reveals UAT-10362’s "Lucid" malware family targeting Taiwan. Using Lua, Rust, and regional locks, this threat prioritizes extreme stealth.
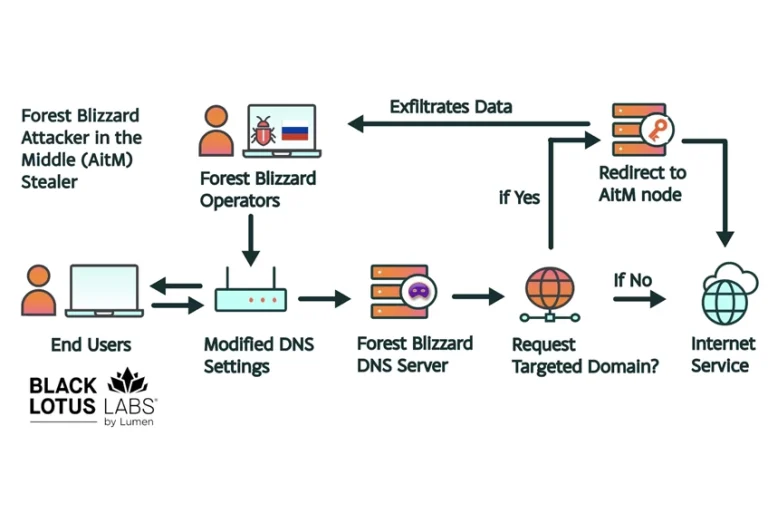
Russian-linked Forest Blizzard's FrostArmada campaign hijacked 18,000+ routers to steal OAuth tokens via DNS redirection. Learn how they stayed invisible.

Cisco Talos exposes "Platform-as-a-Proxy" (PaaP). Hackers are abusing GitHub and Jira's trusted mail servers to bypass SPF/DKIM and deliver phishing lures.
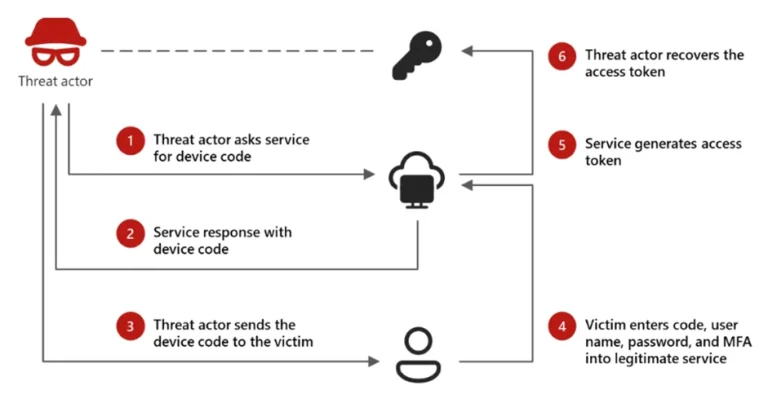
Microsoft uncovers EvilToken, an AI-powered PhaaS toolkit using Dynamic Device Code Generation to bypass MFA and breach high-value accounts. Patch now!
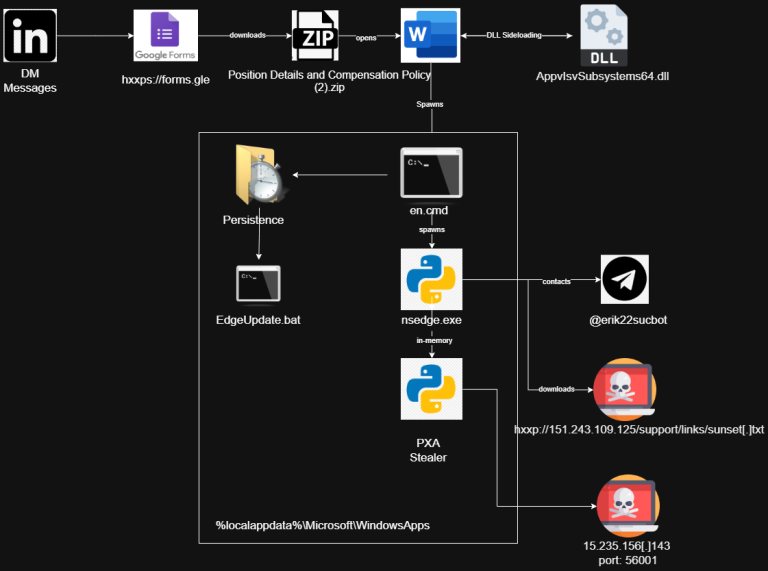
LinkedIn job seekers are being targeted by a sophisticated Vietnam-based group using PXA Stealer. This 100MB malware bypasses MFA and drains crypto wallets.
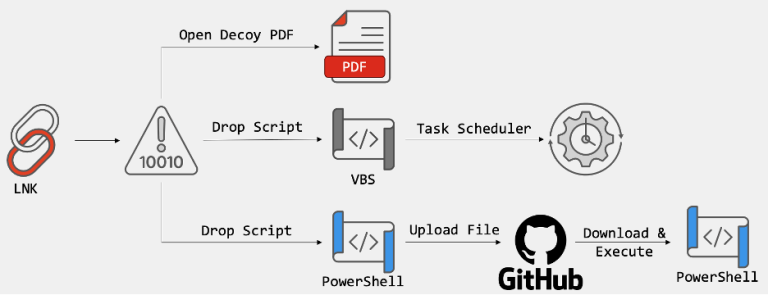
FortiGuard Labs unmasks a South Korean espionage wave abusing the GitHub API for C2 and using LNK files to stay invisible. Protect your network from LotL.
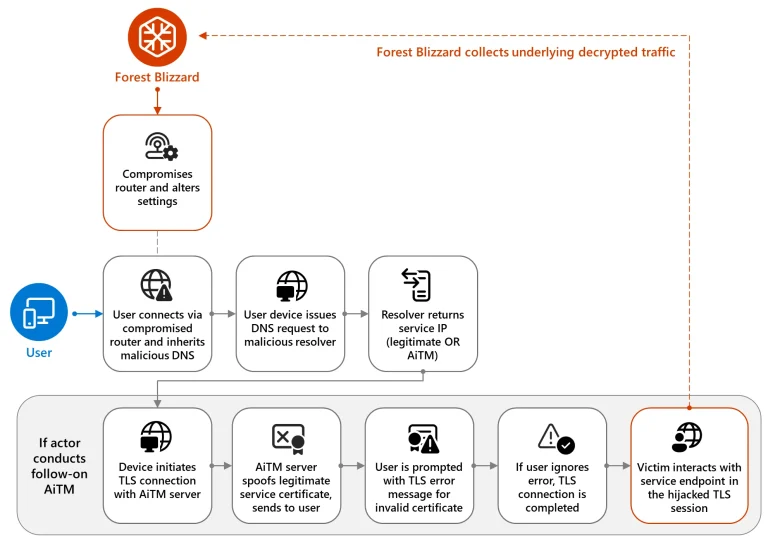
Microsoft exposes Forest Blizzard’s hijacking of 5,000+ SOHO routers for DNS spying and AiTM attacks on Microsoft 365 and governments. Patch your router now!

Attackers drained $285M from Drift Protocol in just 12 minutes using a fake token and pre-signed transactions. Learn how the 2026 DeFi heist went down.

Attackers are impersonating Linux leaders on Slack to drop malware via fake Google Workspace links. Protect your dev environment—verify before acting!

NCSC unmasks APT28’s "digital funnel" using router DNS hijacking to steal OAuth tokens and passwords. Protect your remote workforce—patch your routers now.

Cisco Talos uncovers UAT-10608, an automated campaign using "NEXUS Listener" to harvest Next.js credentials via React2Shell. Patch your cloud tokens now!

Sophos MDR uncovers STAC6405, a phishing campaign abusing RMM tools like LogMeIn for unattended access. Learn how to spot the "Special Invitation" lure.

Proofpoint identifies a surge in 2026 tax scams using RMM tools (39%) to bypass security. Learn how TA4922 and TA2730 target your data this filing season.

The Axios npm hijack exposed millions to a RAT. Discover how North Korean-nexus actor UNC1069 used a masterful phishing ruse to bypass 2FA and steal credentials.
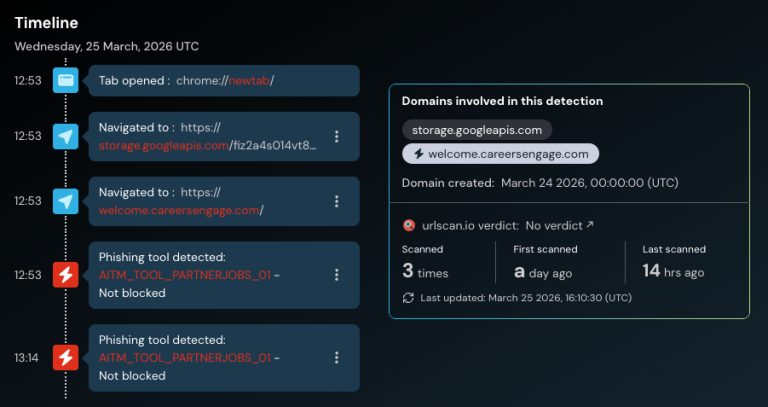
Researchers uncover a novel AiTM campaign targeting TikTok for Business. Attackers bypass MFA to steal Google SSO tokens and hijack corporate ad accounts.

NCSC warns high-risk individuals of Russian and Chinese state actors hijacking WhatsApp and Signal. Protect your chats with these essential 2026 defense tips.

Gen Digital warns of a reservation hijack scam using real stay dates and hotel names to steal credit cards via WhatsApp. Don't tap that link!
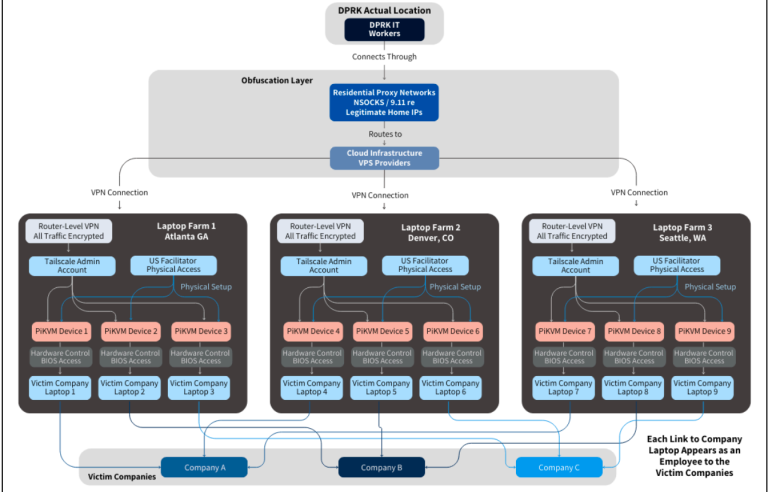
Nisos exposes a North Korean IT worker scheme involving a Florida-based laptop farm, AI-generated resumes, and PiKVM devices. Don't fall for the ruse.

Sekoia TDR reveals Silver Fox's latest tactics. From tax-themed phishing to WhatsApp clones, this China-based group combines espionage with financial theft.
RedLine architect Hambardzum Minasyan is extradited to the U.S. to face 50 years in prison for his role in the global malware empire and Operation Magnus.

North Korean group NICKEL ALLEY targets tech pros with "Contagious Interview" scams. Using fake job tests and RATs, they steal crypto and corporate access.