
 Do Son
The Scattered Lapsus$ Hunters "supergroup" is paying $1,000 per successful vishing call. Discover how they use female recruits to bypass corporate IT security.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
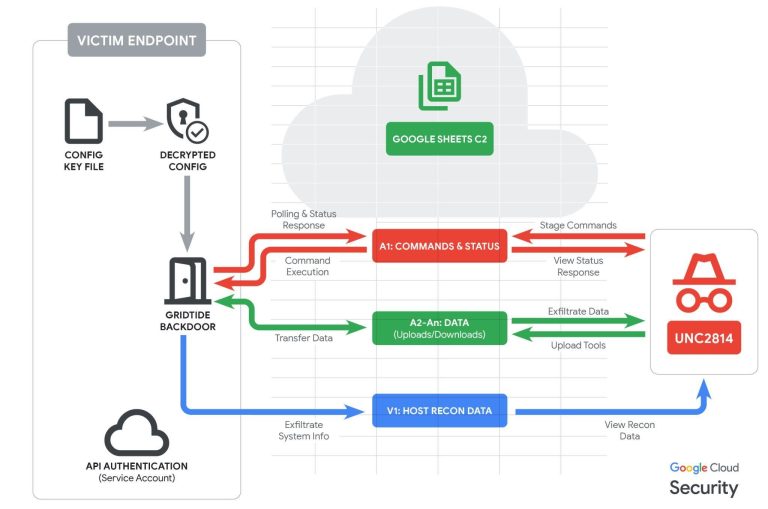
Google and Mandiant disrupt UNC2814, a China-nexus group using the GRIDTIDE backdoor to hide command-and-control traffic inside Google Sheets across 42 nations.

GreyNoise detects a coordinated surge in SonicWall reconnaissance. With over 84,000 scans, attackers are mapping VPNs for Akira and Fog ransomware strikes.
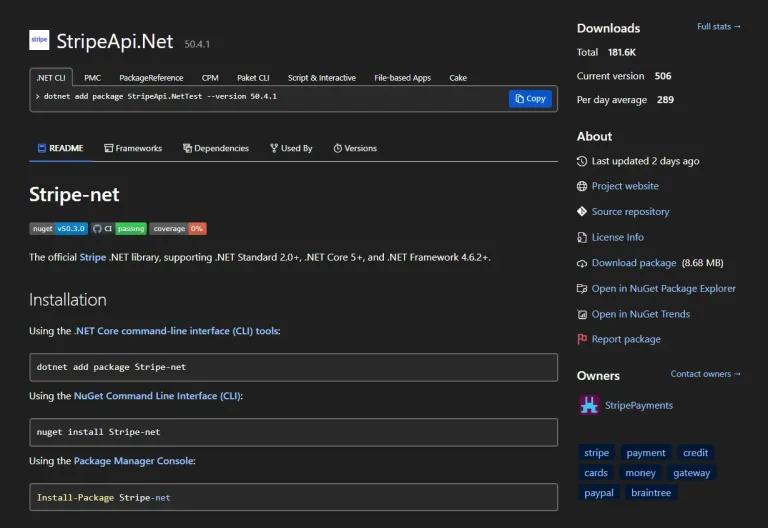
ReversingLabs uncovers a malicious NuGet package mimicking Stripe.net. Discover how attackers are targeting the financial sector via supply chain poisoning.

Cofense uncovers a stealthy campaign abusing legacy WebDAV in Windows File Explorer to bypass browsers and EDR, delivering XWorm and Async RAT via UNC paths.

BlueVoyant uncovers a shift in Mercenary Akula (UAC-0050) tactics, targeting European financial institutions via spoofed judicial lures and RMS malware.

Varonis uncovers 1Campaign, a sophisticated tool by 'DuppyMeister' that helps hackers bypass Google Ads security to deliver phishing and crypto drainers.
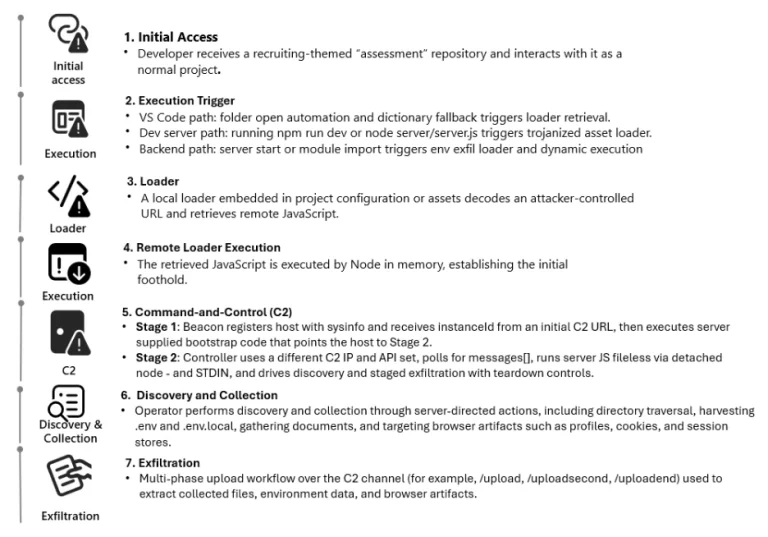
Microsoft warns of a new campaign targeting engineers via fake Next.js technical assessments. Malware hides in VS Code tasks and npm scripts to steal secrets.
Threat hunters expose North Korean state actors using Medusa ransomware to fund global espionage. U.S. healthcare and non-profits are the primary targets.

The DFIR Report reveals how a persistent attacker exploited CVE-2023-46604 twice in 18 days to deploy LockBit ransomware. Patch your ActiveMQ servers now!

Researcher @goyaramen exposes "ARXON," an AI-automated pipeline using LLMs to manage simultaneous global attacks on Fortinet devices. The future of scale is here.

GitLab reveals how North Korean fake IT workers use 'Contagious Interview' scams to bypass hiring, steal data, and hijack executive digital identities.
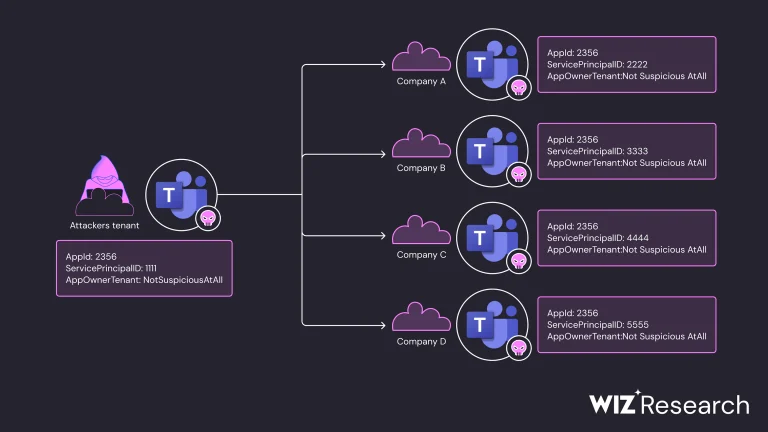
Wiz Research exposes a stealthy threat using malicious OAuth apps and Cyrillic homoglyphs to bypass Microsoft Entra ID security. Protect your cloud tenant.
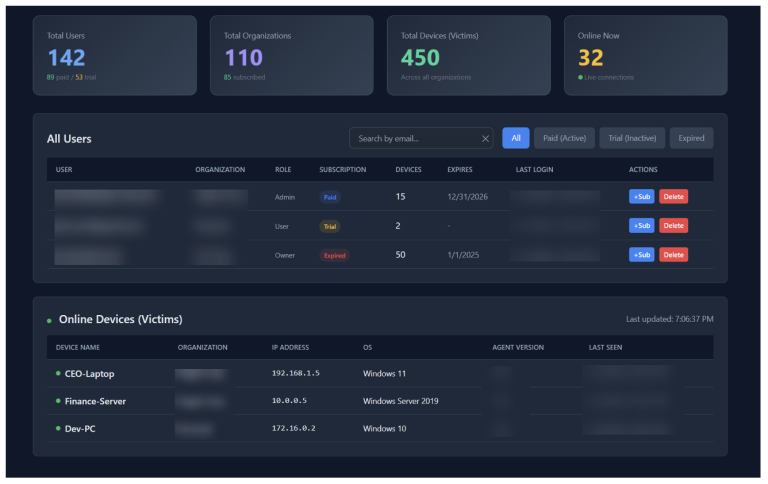
Proofpoint exposes TrustConnect, a new Malware-as-a-Service masquerading as an IT tool. The AI-assisted fake RMM software replaces dismantled threats.
Group-IB exposes an industrialized mobile banking fraud campaign in Indonesia. GoldFactory hackers use fake Coretax apps and Gigabud.RAT to drain accounts.

Ukrainian hacker Oleksandr Didenko receives a 60-month sentence for orchestrating a massive laptop farm scheme aiding North Korean IT operatives.
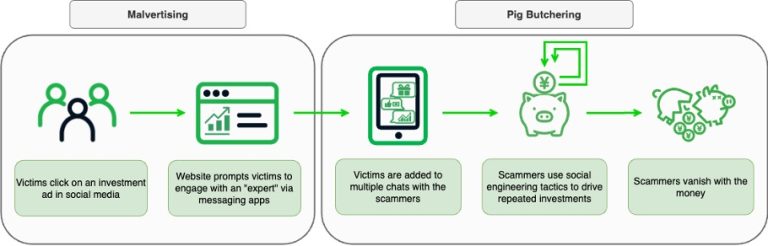
Infoblox Threat Intel exposes a highly scalable hybrid scam merging automated malvertising with "pig butchering" to drain global crypto investors' funds.

North Korean hackers target IT pros with "Contagious Interview" malware. Fake job offers install trojanized MetaMask extensions to steal crypto.

Bridewell warns of Russian hackers targeting Booking.com. Phishing kits steal hotel staff creds to scam guests with "I Paid Twice" messages.

Hackers abuse Atlassian Jira notifications to bypass spam filters. Trend Micro warns of scams targeting enterprise users via trusted alerts.

Okta exposes North Korean IT workers using AI photos & stolen LinkedIn profiles to land remote jobs. Learn how "JJ" bypassed checks.
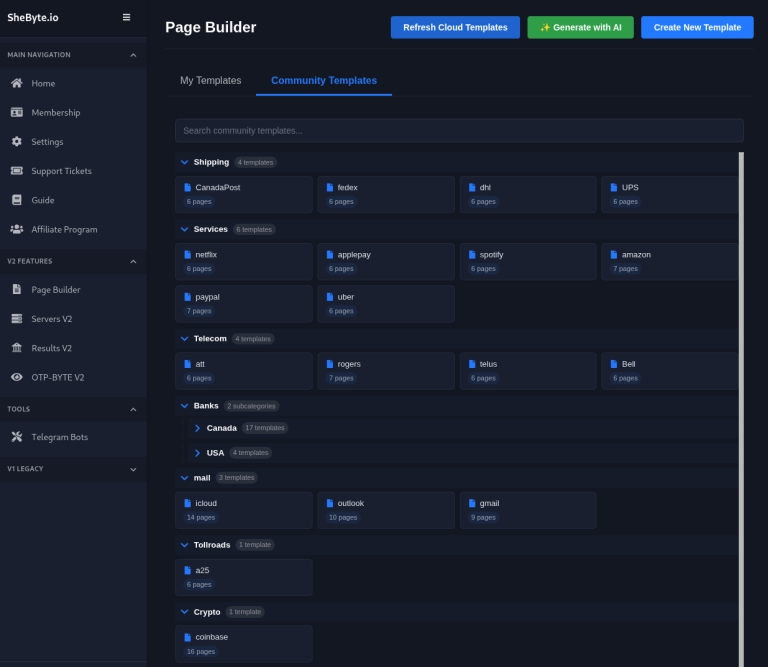
Rapid7 reveals how "Carding-as-a-Service" mimics legitimate e-commerce. Fraud markets now offer refunds & "Fullz" data. Learn about the new threat.