
 Do Son
New "PayTool" fraud cluster targets Canadians via fake Gov & Air Canada sites. CloudSEK reveals how this PhaaS operation steals Interac logins.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.

Attackers exploit GitHub forks ("Repo Squatting") to push HijackLoader malware via official-looking URLs. Technique remains active; verify all downloads.
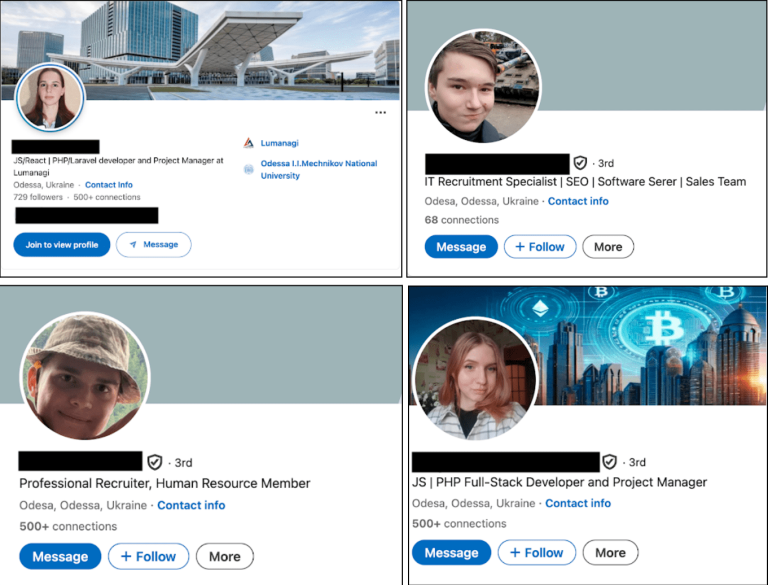
North Korean group PurpleBravo uses fake job offers to breach IT firms. The "Contagious Interview" campaign deploys malware via coding tests.
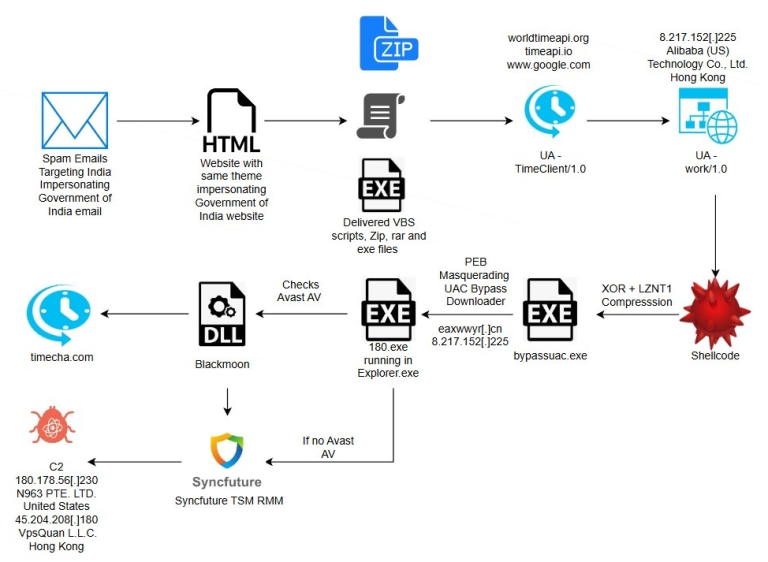
"SyncFuture" spies on Indian users via fake Income Tax emails. This advanced campaign bypasses antivirus & installs Chinese IT tools for total surveillance.

KONNI APT targets APAC developers with AI-generated malware disguised as crypto projects. The "polished" backdoor steals wallets & credentials.

Unit 42 reveals "living" phishing pages built by GenAI on the fly. These polymorphic attacks evade detection by generating unique code for every victim.

Okta reveals new vishing kits that "drive" victim browsers. These real-time tools sync phone calls with phishing pages to bypass MFA number matching.
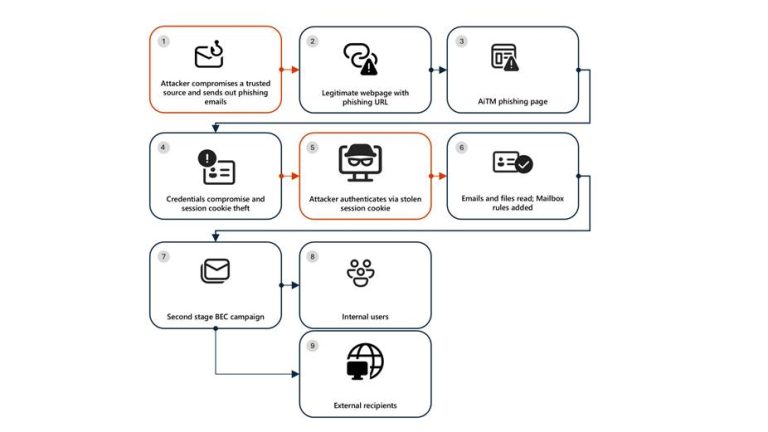
Microsoft warns of an AiTM phishing campaign targeting the energy sector. Hackers steal session cookies and abuse SharePoint to launch internal attacks.

Group-IB reveals a sophisticated loan phishing campaign in Peru. Scammers use the Luhn algorithm to validate stolen credit cards via fake ads.

Arctic Wolf warns of automated FortiGate SSO attacks stealing configs and creating backdoors. Disable admin-forticloud-sso-login immediately.

Scammers target PNB MetLife users via mobile phishing. Attackers use Telegram bots to steal data & manipulate clipboards for UPI fraud.

Attackers are hijacking Linux Snap Store apps by registering expired developer domains. Malicious updates target crypto wallets. Secure your accounts now.
Seqrite exposes "Operation Covert Access": A Rust RAT targeting Argentina's legal system via fake court rulings. Includes anti-analysis & encryption tools.

Infoblox researchers hijacked a scam network using the "Sitting Ducks" DNS flaw. 57M logs reveal how abandoned domains fuel global push notification spam.

CloudSEK exposes "RedLineCyber," an impostor hijacking crypto clipboards on Discord. This stealthy malware drains wallets without a C2 server.

Group-IB uncovers DeadLock ransomware using Polygon smart contracts for resilient C2. This "EtherHiding" tactic signals a new era of blockchain abuse.

Check Point reveals Sicarii ransomware is a Russian false flag operation. Despite Israeli branding, the group relies on machine-translated Hebrew.

Microsoft & police seize RedVDS, a service providing disposable VMs for crime. The takedown stops a network responsible for over $40M in fraud losses.

Trellix warns: "Browser-in-the-Browser" phishing creates perfect fake Facebook login pop-ups. Learn how this invisible trap steals credentials.

New Magecart campaign mimics Stripe forms to skim credit cards. Malware hides from admins & tricks users with fake errors. Active since 2022.

ASEC warns: Hackers abuse Syncro, SuperOps & NinjaOne RMM tools via fake PDF lures. Learn how this phishing campaign installs persistent backdoors.

Team Cymru exposes the carding supply chain: How criminals use the Soviet .su domain and bulletproof hosting to run resilient fraud markets.