 Do Son
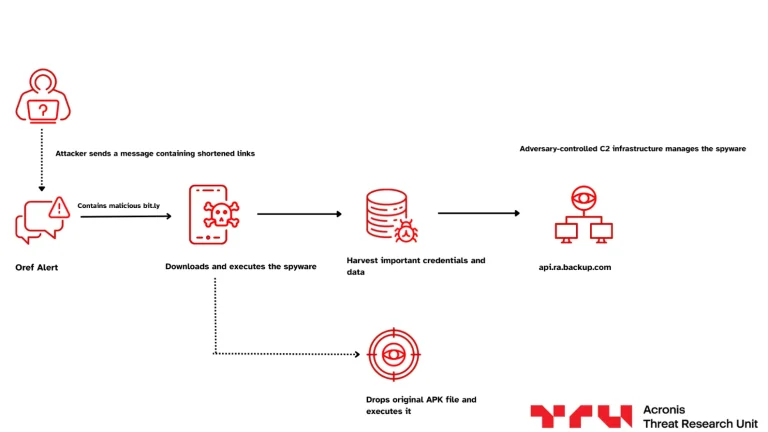
Acronis TRU uncovers a trojanized Red Alert rocket warning app targeting Israelis. Linked to APT-C-23, this Android malware steals data while alerting users.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
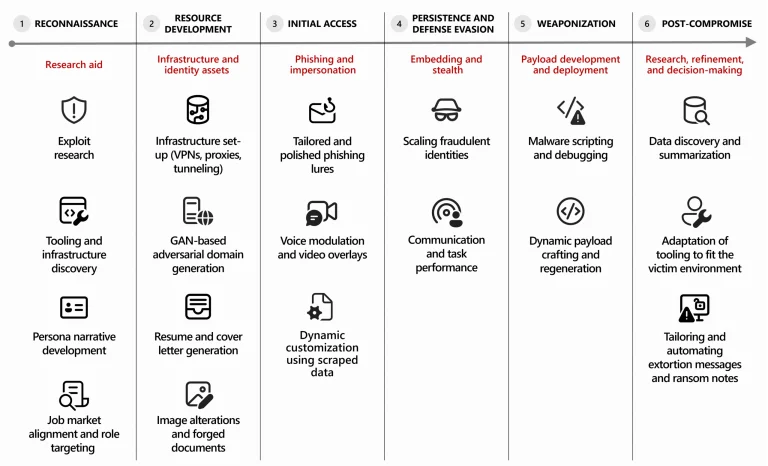
Microsoft Threat Intelligence reveals how cybercriminals and North Korean APTs are weaponizing generative AI to scale attacks and poison AI assistants.

Zscaler ThreatLabz reveals a surge in Middle East conflict-themed cyberattacks, uncovering 8,000+ malicious domains, LOTUSLITE backdoors, and scams.
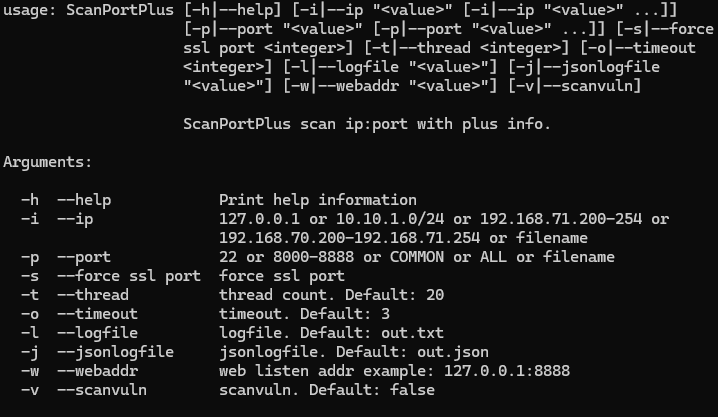
Unit 42 uncovers CL-UNK-1068, a Chinese APT targeting Asian critical infrastructure using stealthy web shells, LOLBINs, and screen-printed exfiltration.

Dutch intelligence (MIVD/AIVD) warns of a global campaign using social engineering to silently hijack Signal and WhatsApp accounts of high-profile targets.
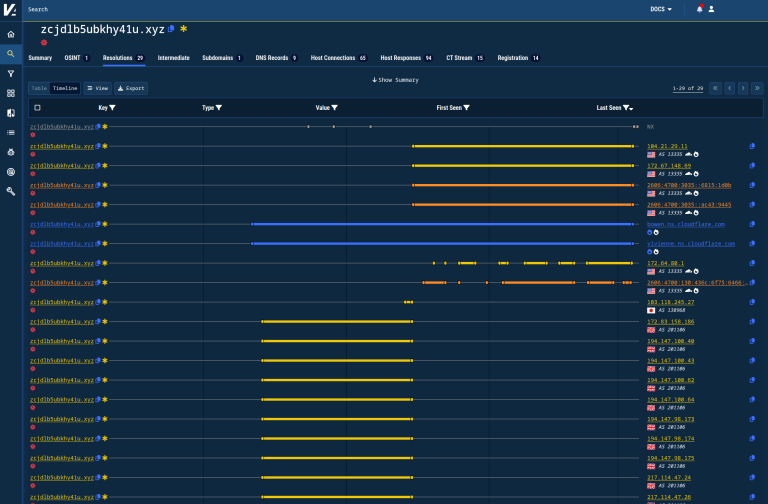
Validin reveals how the Coruna iOS exploit kit evolved from targeted surveillance to mass crypto-draining and geopolitical watering hole attacks.
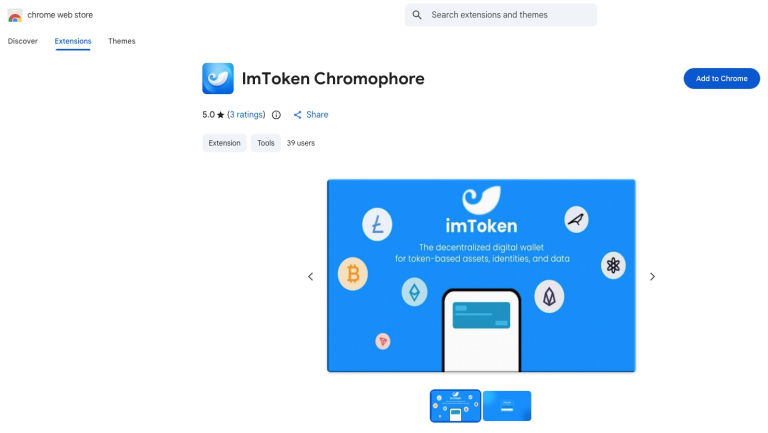
Socket researchers uncover "ImToken Chromophore," a malicious Chrome extension using fake branding and homoglyphs to steal crypto wallet seed phrases.

A joint advisory warns of INC Ransom's devastating pivot to the Pacific. Discover how this RaaS group uses double extortion to target healthcare sectors.
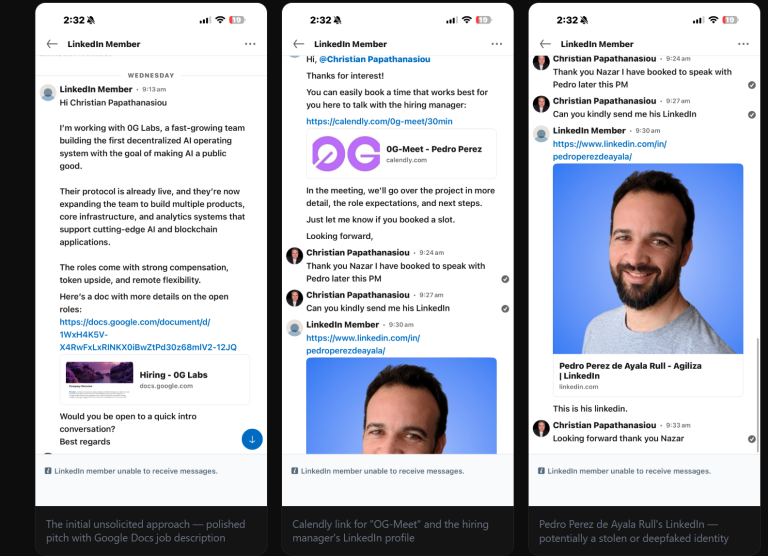
A fake LinkedIn recruiter and a poisoned GitHub repo: See how a CEO uncovered the North Korean "Contagious Interview" malware targeting Web3 developers.
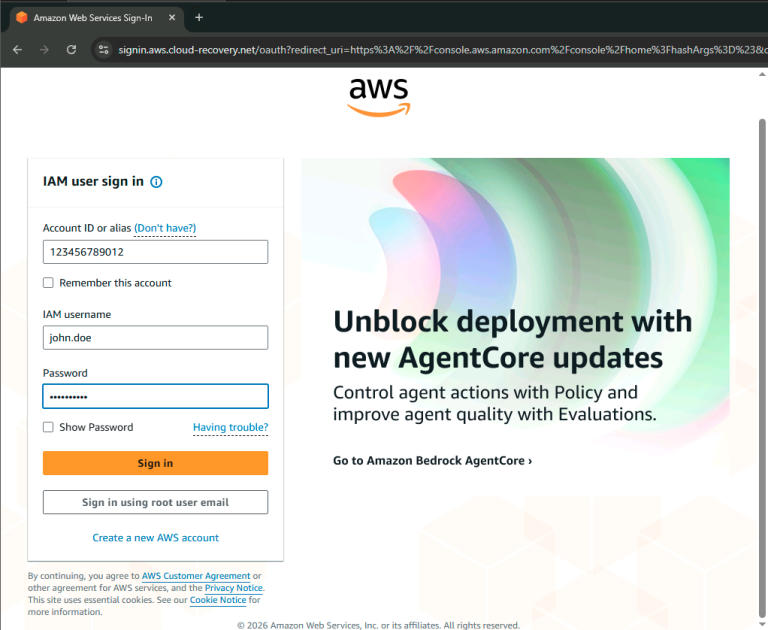
Datadog Security Research uncovers a sophisticated AiTM phishing campaign using real-time proxies to steal AWS Console credentials and bypass MFA in minutes.

Unit 42 reveals the first real-world cases of Indirect Prompt Injection (IDPI), where hackers weaponize website content to bypass AI security filters.

Microsoft Defender exposes a new phishing campaign using EV certificates and fake Teams invites to silently deploy RMM backdoors on corporate networks.

Law enforcement from 14 countries just seized LeakBase.ws. With 142k accounts and 215k messages exposed, the DOJ sends a clear message: No hacker is anonymous.

Microsoft and Europol lead a global coalition to dismantle Tycoon 2FA, a massive AiTM phishing platform that bypassed MFA for over 500,000 organizations.
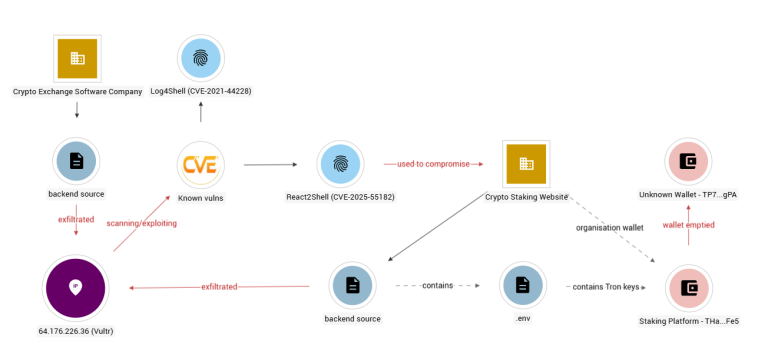
Ctrl-Alt-Intel exposes a suspected DPRK campaign using an 'Amazon Kill Chain' and React2Shell to systematically breach crypto exchanges and steal code.
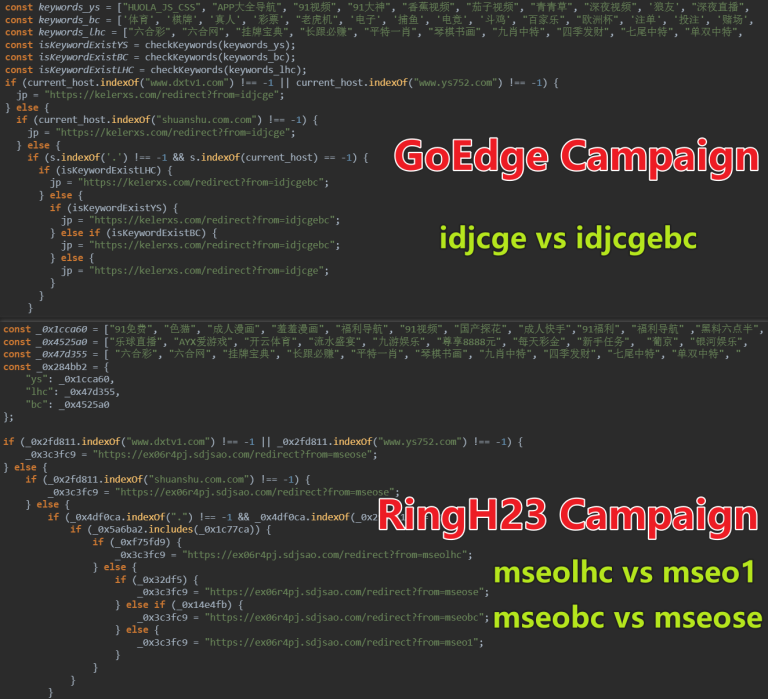
XLab researchers reveal the return of OFAC-sanctioned Funnull. The group is using the new RingH23 framework to hijack CDNs and poison supply chains.
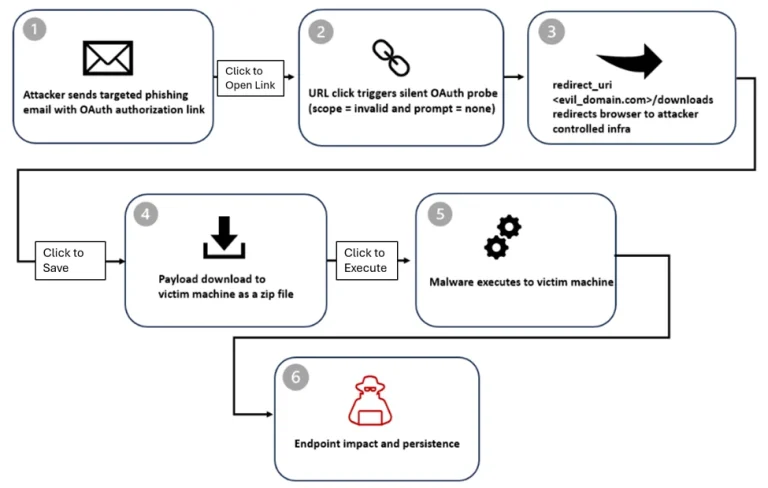
Microsoft Defender reveals a new phishing campaign abusing OAuth redirect URIs to bypass security and deliver stealthy malware to your system.

Cyfirma reveals how Telegram has replaced the dark web as the ultimate digital black market, making tools like malware and data theft available to anyone.

Cybercriminals are using a fake Google security checkup (google-prism) to trick you into installing powerful PWA malware. Learn how to spot the trap.

Infoblox uncovers a novel phishing tactic abusing the .arpa TLD. Attackers hijack internet "plumbing" to bypass firewalls and deliver brand-impersonation scams.

OpenAI’s Feb 2026 report reveals "cyber special operations," Cambodian "Date Bait" scams, and Russian content farms using AI to automate global disruption.
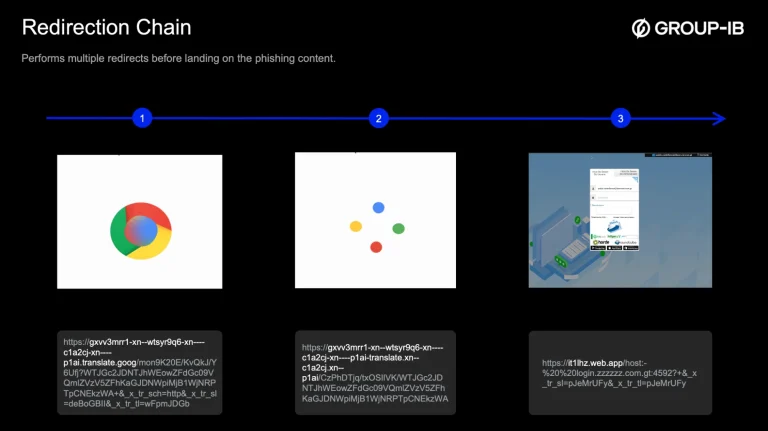
Group-IB uncovers "GTFire," a massive credential-harvesting operation abusing Google Firebase and Translate to bypass security filters in 100+ countries.