 Do Son
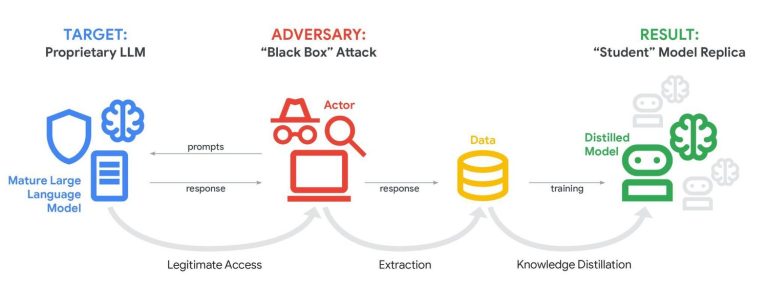
Google Threat Intelligence reports a surge in "model extraction" attacks. Private entities are cloning AI models & stealing API keys. Stay alert.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
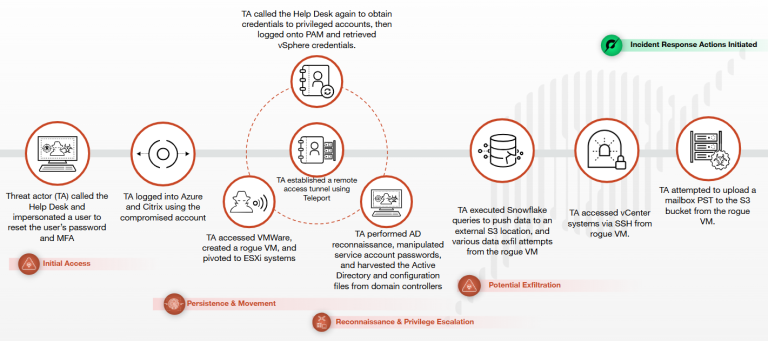
Unit 42 reveals Muddled Libra (Scattered Spider) uses rogue VMs in vSphere to persist. Learn how they bypass defenses without malware. Read more.

New Telegram phishing campaign abuses the "This is me" feature for account takeover. CYFIRMA reveals a global framework evading detection. Stay alert.

Silent Push's Traffic Origin technology strips away VPN masks to reveal the true location of threat actors. Detect North Korean & Russian proxies now.

Hackers abuse PayPal & Apple to send "perfect" phishing emails. Learn how DKIM Replay attacks bypass security filters & DMARC checks.

Rublevka Team's "scam-as-a-service" has stolen $10M+ in crypto. Their automated Solana drainers target Phantom & Solflare wallets. Don't be next.
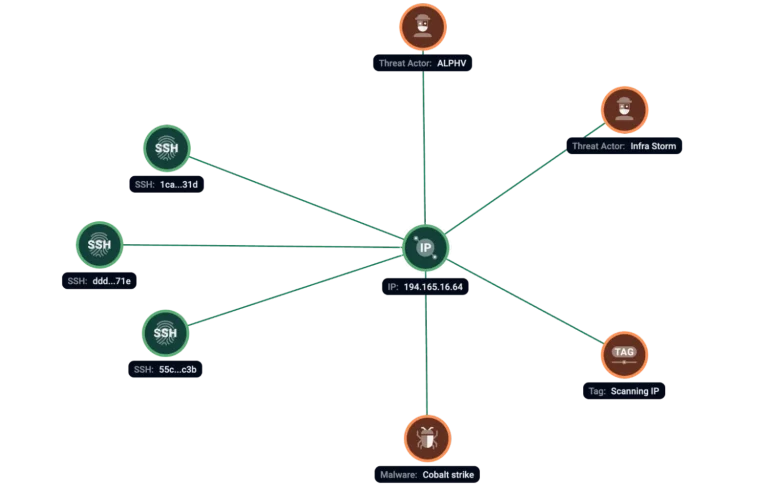
Group-IB reveals ShadowSyndicate is evolving. The cybercrime cluster now rotates SSH keys to hide its infrastructure. Is it a BPH or IAB?

Hackers are hijacking NGINX servers via malicious config injections. Datadog warns of silent traffic redirection for SEO poisoning. Check your proxy_pass.

Sophisticated phishing abuses Vercel Blob & PDFs to bypass filters. Stolen credentials are exfiltrated via Telegram bots. Learn how to spot this attack.

New "directory shadowing" malware creates physical folders to hijack WordPress URLs. It feeds gambling spam to Googlebots while staying invisible.
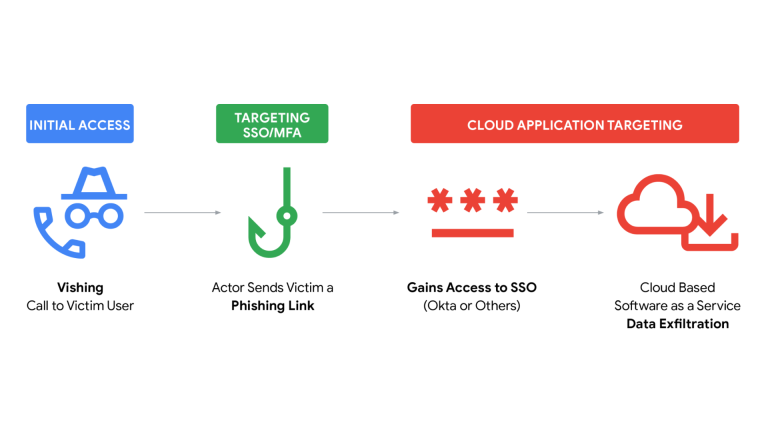
Mandiant warns of vishing rings like ShinyHunters impersonating IT support to bypass MFA and steal corporate cloud data. Verify your callers.

"ConsentFix" phishing tricks users into pasting OAuth codes from Azure CLI, bypassing MFA and Conditional Access. Detect this "fix" scam now.

New "APT IRAN" framework targets energy grids & military networks. Lab52 links the tool to the IRGC. See the threat to critical infrastructure.

INJ3CTOR3 hackers target FreePBX with EncystPHP web shell via CVE-2025-64328. Malware uses cron jobs for persistence. Patch immediately.

TA584 triples activity with new "Tsundere Bot" malware. Attackers use invisible Registry keys to hide persistence. Read the Proofpoint analysis.

Google disrupts IPIDEA proxy network. Fake VPNs and hijacked apps turned millions of devices into unwitting exit nodes. Play Protect is removing them.
"SessionReaper" (CVE-2025-54236) targets Magento stores. Attackers use zombie tokens to gain root access. 200+ sites compromised. Patch now.
"Amazon Ads Blocker" extension exposed for stealing creator revenue. It hijacks affiliate links to divert commissions to the developer. Uninstall it now.
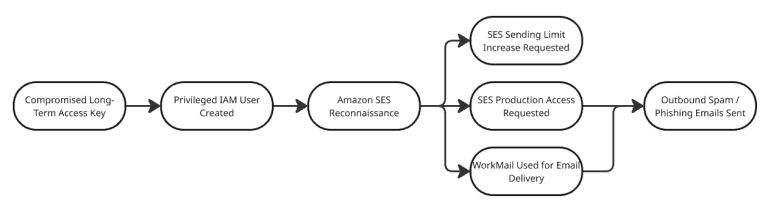
Attackers are bypassing AWS SES sandbox limits by pivoting to WorkMail. Rapid7 reveals how this abuse creates a blind spot for defenders.

Critical WinRAR flaw CVE-2025-8088 is exploited by spies & cybercriminals. "Zeroplayer" sells the exploit. Update to v7.13 to stop Startup folder attacks.

ZachXBT unmasks an alleged $40M theft of U.S. government crypto in Jan 2026. The suspect? The son of the USMS contractor hired to protect it.
Jingliang Su sentenced to 46 months for laundering $36.9M in "pig butchering" proceeds. The scheme funneled crypto to Cambodian fraud hubs.