 Do Son
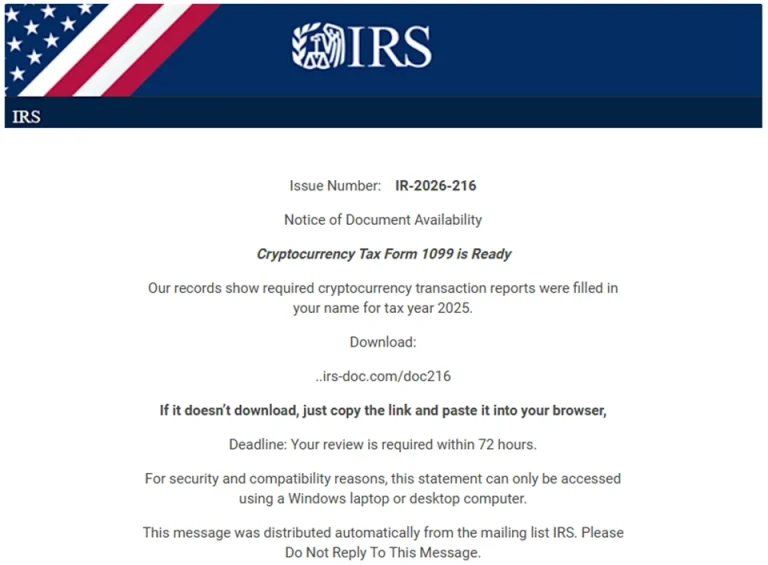
Microsoft warns of a surge in tax-themed phishing using PhaaS and ScreenConnect RATs to bypass MFA and hijack systems. Protect your W-2 data this season.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
Russian national Aleksei Volkov was sentenced to 81 months in prison and ordered to pay $9.1M for his role as an access broker in major U.S. ransomware attacks.

Infoblox and Confiant reveal a global operation using generative AI deepfakes and commercial "cloaking" tools to scale high-fidelity investment scams.

Cybercriminals are targeting OpenClaw developers with a fake $5,000 CLAW token airdrop. Learn how this GitHub-based wallet drainer works and stay protected.
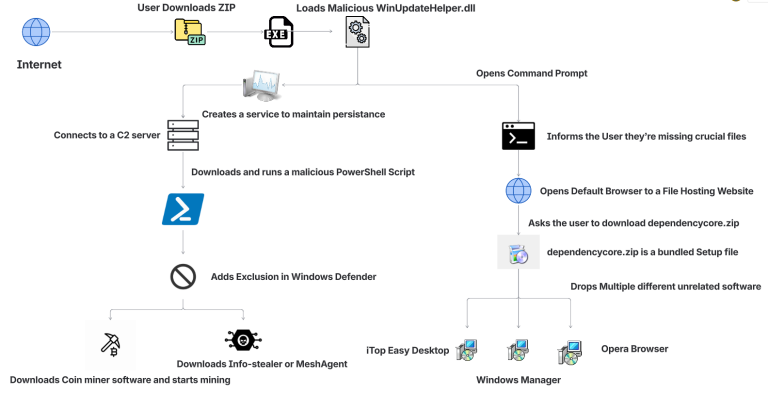
McAfee researchers found a massive malware campaign using LLMs to "vibe code" 1,700+ fake downloads. From Roblox mods to AI tools, your PC is the target.

BI.ZONE uncovers Forbidden Hyena using AI-generated code to deploy the new BlackReaperRAT and Milkyway ransomware in highly evasive cyberattacks.

The US DOJ has seized four domains used by Iran's MOIS to orchestrate global cyberwarfare, doxing, and death threats against dissidents and governments.
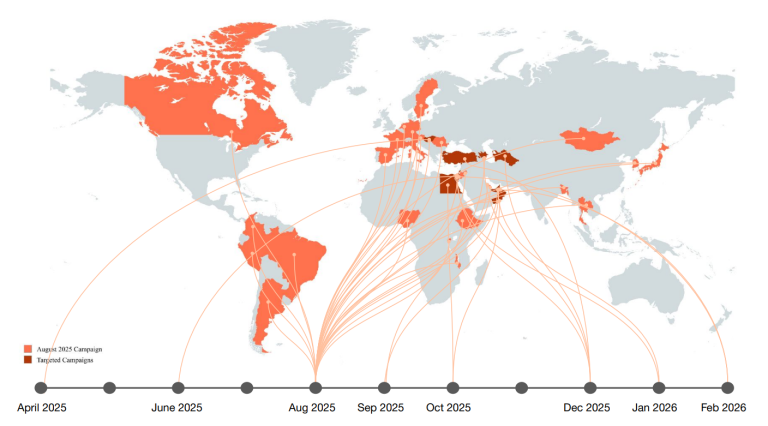
Unit 42 reveals Iranian APT Boggy Serpens is weaponizing hijacked accounts, AI-generated code, and Rust malware to infiltrate critical infrastructure.

In a move to protect the nation’s critical infrastructure, the Cybersecurity and Infrastructure Security Agency (CISA) has...
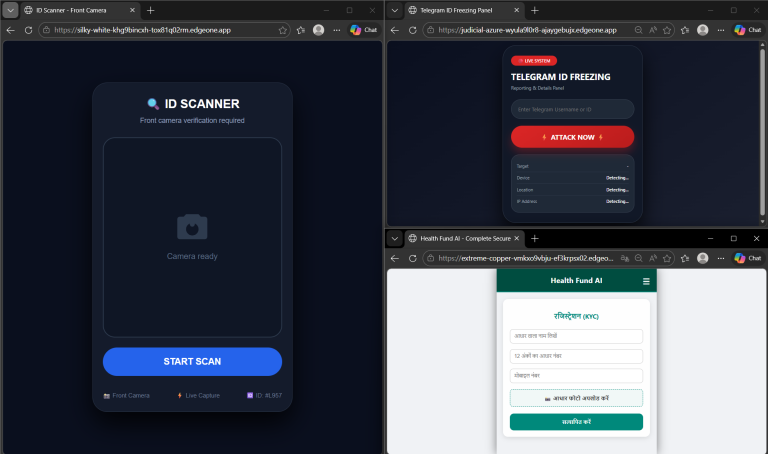
Cyble exposes a phishing campaign abusing browser permissions to silently steal biometric data, audio, and locations for deepfakes and identity fraud.
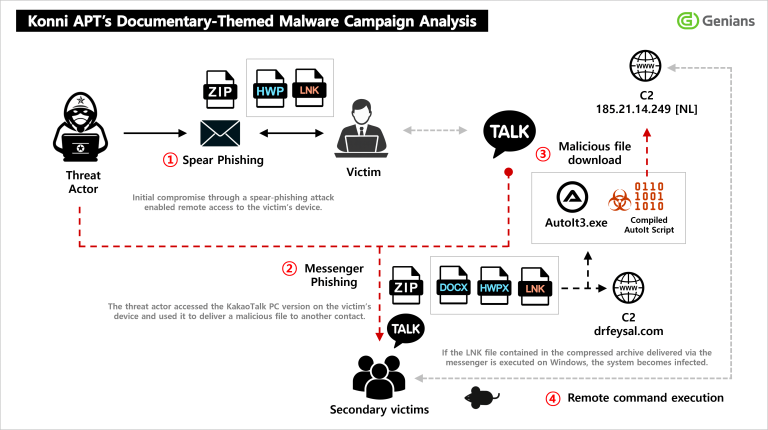
Genians Security Center reveals a new Konni APT campaign hijacking KakaoTalk PC sessions to distribute EndRAT, RftRAT, and RemcosRAT to trusted contacts.

The EU Council hits Chinese and Iranian cyber threat actors with severe sanctions for hacking critical infrastructure and spreading Olympic disinformation.
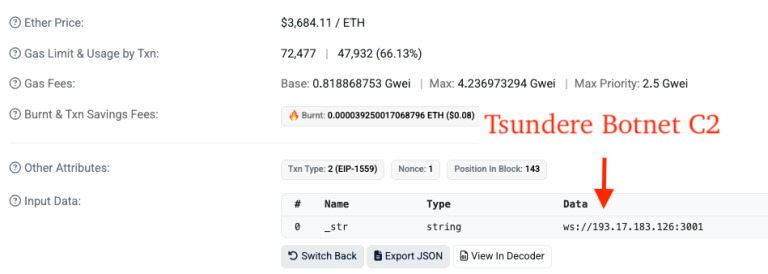
eSentire TRU reveals Iranian group Muddy Water deploying the Russian-linked Tsundere botnet, utilizing Ethereum smart contracts for stealthy C2 communication.

Seqrite Labs exposes Operation CamelClone, a global cyber espionage campaign using the HOPPINGANT loader and public cloud services to evade detection.

Microsoft Defender Experts warn of Storm-2561 using SEO poisoning to distribute fake enterprise VPN clients like Pulse Secure, stealing user credentials.

OFAC sanctions a North Korean IT worker network and global facilitators for defrauding U.S. businesses of nearly $800M to fund the regime's WMD programs.
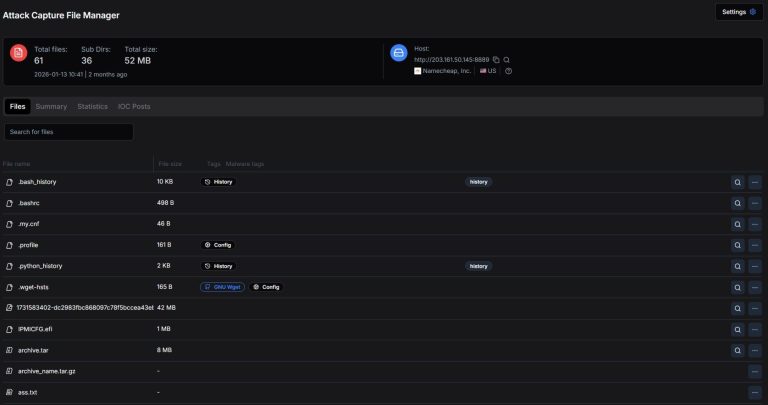
Hunt Intelligence unmasks APT28's 'Roundish' toolkit from an exposed server, revealing advanced CSS side-channel attacks and stealthy Linux implants.
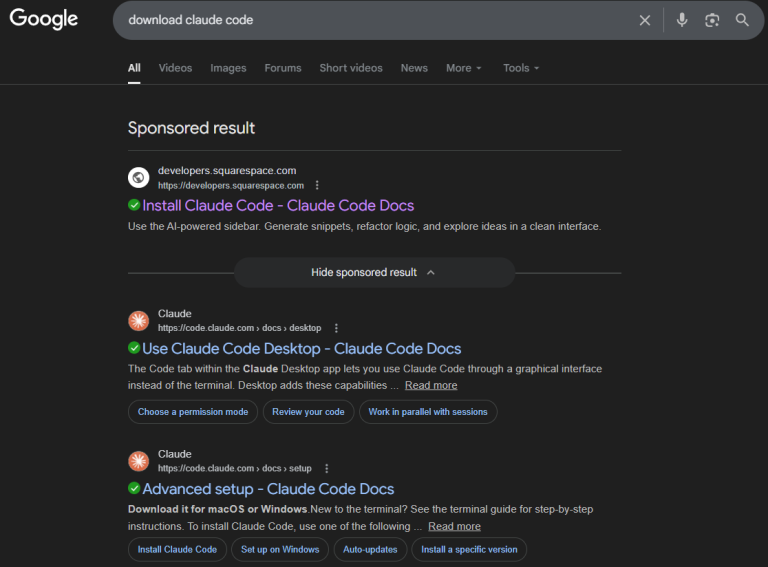
Bitdefender exposes a malvertising campaign targeting developers searching for Claude Code. Fake Google Ads deploy Windows stealers and macOS backdoors.
Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground

Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground
Check Point Research reveals Iranian state hackers (Void Manticore) are weaponizing RaaS and criminal malware like Rhadamanthys for plausible deniability.
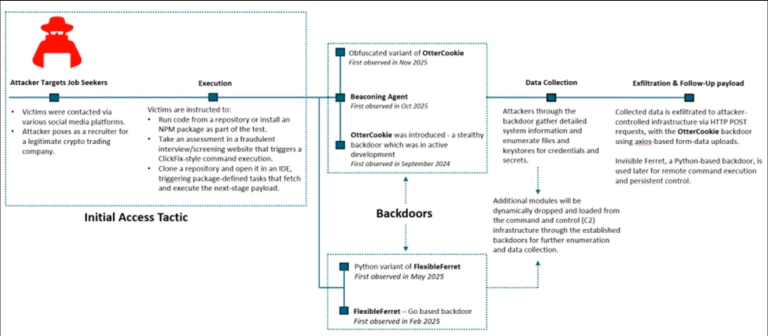
Microsoft exposes the "Contagious Interview" campaign. Fake recruiters trick developers into installing Invisible Ferret malware during coding tests.
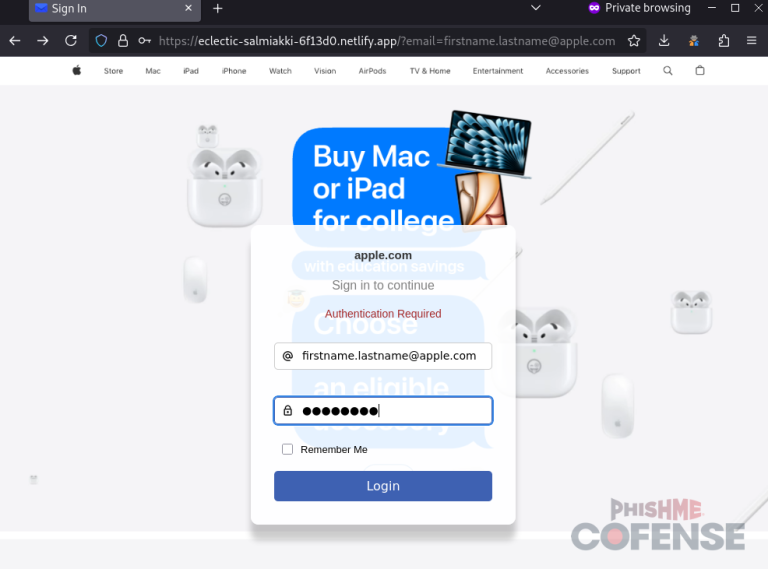
A new Cofense report reveals how hackers abuse legitimate Telegram Bot APIs to create stealthy Command and Control (C2) centers for data exfiltration.

Discover how Operation False Siren weaponizes Israel's Red Alert app via smishing, deploying advanced Android spyware for geo-fenced mobile espionage.