 Do Son
Google GTIG confirms the first AI-built zero-day exploit used in the wild. Discover how AI is industrializing cyber warfare and how Big Sleep is fighting back.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.

DOJ sentences U.S. enablers for running North Korean "laptop farms." Learn how the DPRK breached 70 companies and funded weapons via stolen identities.
SEQRITE Labs uncovers Operation Silent Rotor, a targeted Rust-based cyberattack on the Eurasian unmanned aviation sector ahead of the 2026 Moscow forum.
Cisco Talos reveals the rise of TOAD attacks. 55% of scam campaigns now use VoIP "anchors" to bypass email filters and trick victims into calling fraud centers.
Securonix exposes an 80+ organization breach using "self-healing" RMM tools and Safe Mode persistence. Standard antivirus is blind—learn how to hunt it!

Google AppSheet is being abused by "AccountDumpling" to steal 30,000 Facebook accounts. Learn how this Vietnamese-linked group bypasses SPF/DKIM filters.

Ransomware "closer" Deniss Zolotarjovs is sentenced to 102 months for extorting 50+ firms. See how the Conti-linked "Destroyer" was caught and prosecuted.
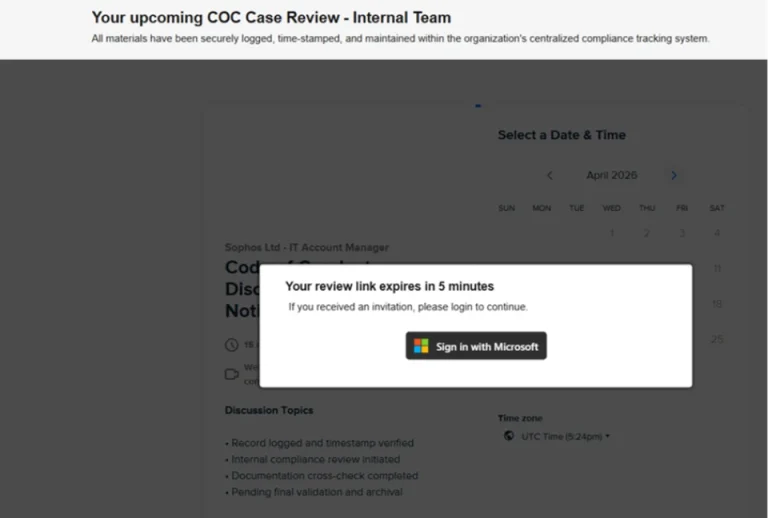
Microsoft warns of a massive AiTM phishing campaign targeting 13,000+ orgs. Using fake disciplinary lures, attackers bypass MFA to hijack active sessions.

Scammers are leveraging Amazon SES and leaked IAM keys to bypass security filters. Learn how to protect your organization from this high-trust phishing surge.

Varonis uncovers Bluekit, a new phishing-as-a-service kit using AI and 40+ templates to automate session hijacking and credential theft. See how it works.

Trend Micro uncovers a phishing campaign abusing Kuse.ai and VEC to steal credentials via markdown notes. Don't trust a domain just because of its reputation.
Two US cybersecurity professionals get 4 years in prison for acting as ALPHV BlackCat ransomware affiliates, extorting victims and leaking patient data.

The alleged mastermind behind the massive "Versus Project" dark web market has been extradited to the US. He faces life in prison for cybercrime and drugs.

Bitdefender uncovers a massive smishing campaign targeting drivers with fake toll and parking fines. Over 79,000 messages sent across 12 countries.

Group-IB unmasks the Phoenix System: a PhaaS platform using rogue cell towers and live-dashboards to bypass MFA across 2,500+ domains. Read the full report.
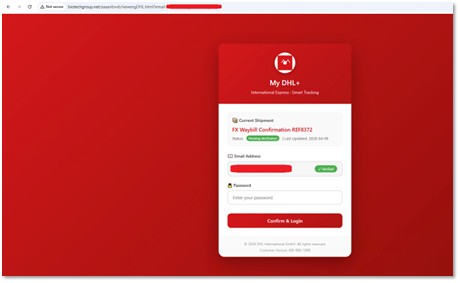
Forcepoint X-Labs uncovers a clever 11-step DHL phishing scam using a fake OTP interface to build trust and steal passwords. See how the trick works.

Yeeth Security uncovers a sophisticated Open VSX campaign using string-fragment reconstruction to hide malware. 16 malicious extensions identified.

FBI, Dubai, and China dismantle 9 "pig-butchering" centers and arrest 276. Operation Level Up saves victims $562M in massive crypto fraud crackdown.
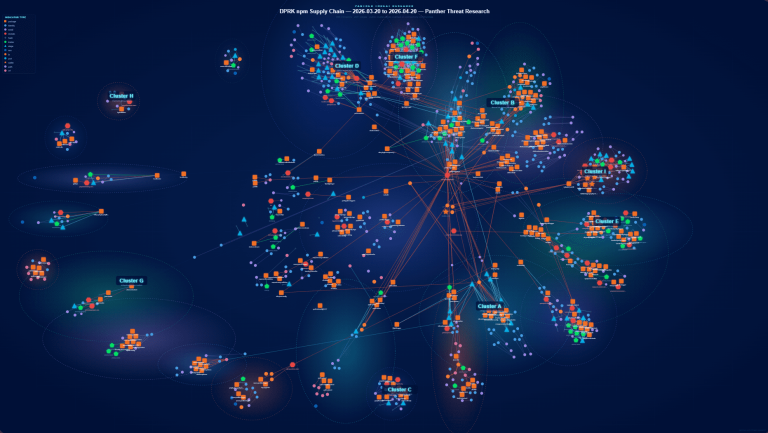
Panther Research exposes a massive 2026 DPRK npm campaign using blockchain dead-drops to steal crypto keys and AI secrets. Secure your CI/CD pipelines now.

Checkmarx discloses a major GitHub breach via a Trivy supply chain flaw. Attackers injected malicious code and exfiltrated data for a month. Get the facts.

BlueNoroff uses a "self-reinforcing" deepfake pipeline to target crypto CEOs. Fake Zoom meetings and stolen footage lead to a 5-minute system compromise.
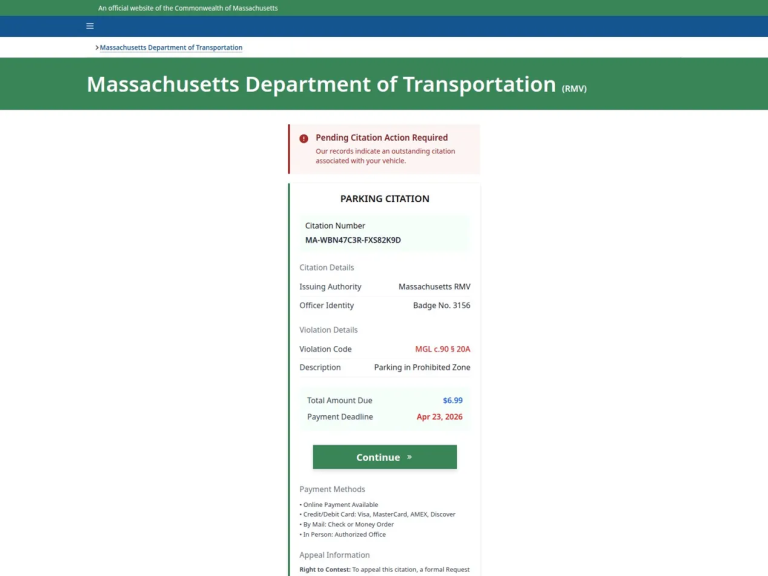
Cyble uncovers "Operation Trust Trap," a 16,800-domain network weaponizing *.gov trust to steal credentials. See how APT36 and others hijack the human eye.