 Do Son
Discover how AI generated malware from DeepSeek turns hallucinated ideas into real browser native ransomware using the File System Access API.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
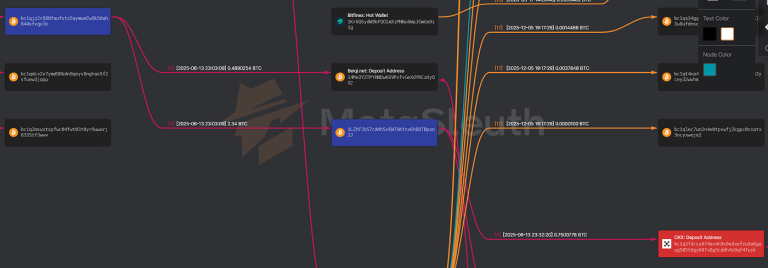
A case study on Kairos ransomware data extortion highlights the futility of paying a $1 million ransom without data encryption.

Discover how Microsoft GDID tracking helped the FBI apprehend a Scattered Spider hacker, revealing the hidden power of Windows device telemetry.

Insikt Group discovered the TAG-182 threat cluster spreading MarkiRAT malware via fake VPN apps to spy on Iranians and alleged dissidents globally.

Vietnamese police made several HiAnime piracy arrests, dismantling a massive anime streaming network that generated over $12 million in illegal revenue.

The FBI issued an alert about a TeamPCP supply chain attack. The group uses malicious code to conduct a software supply chain compromise against developers.

New Lazarus npm malware masquerades as Rollup polyfills, hiding remote-access and wallet-theft payloads. JFrog uncovered six malicious packages.

The suspected ToddyCat APT Umbrij tool executes OAuth token theft to hijack corporate Gmail accounts. Learn how attackers breach cloud security.

Mustang Panda targets India's government and hydropower sectors, abusing Zoho WorkDrive for C2. Acronis found new ZOHOMURK and MINIRECON implants.

Kaspersky details The Gentlemen ransomware, a fast-growing RaaS group with new Go and C lockers, EDR killers, and worldwide victims. Here's how it works.
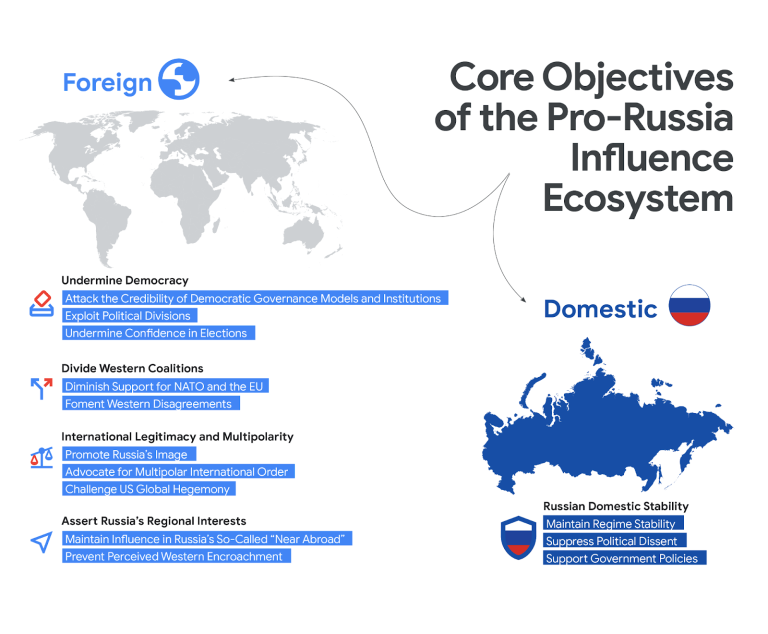
The pro-Russia influence ecosystem is expanding information operations beyond Ukraine. Discover how global targets face new cyber threats and AI tactics.
Following a Scattered Spider arrest, Peter Stokes faces extradition to the US for his alleged role in a $100M cyber extortion and hacking scheme.
A suspected UNC1151 phishing campaign targets Belarusian politicians and Ukrainian portals to steal credentials using deceptive login pages.

Operation DragonReturn is a suspected China-nexus cyber espionage campaign targeting India's tax infrastructure using deceptive phishing emails and DcRAT.
An active hospitality malware campaign uses photo lures and authentication laundering to infect hotel networks with a persistent Node.js implant.
Chinese-speaking actors deploy TinyRCT backdoor attacks against Southeast Asian government and energy sectors. Discover the CL-STA-1062 cyber espionage tactics.

Threat actors are using RAR archive phishing to deploy Thailand healthcare malware. The campaign targets hospitals to steal credentials and sensitive data.

US authorities halted illegal World Cup streaming via nearly 400 domain seizures. Discover how Operation Offsides protects viewers from malware.
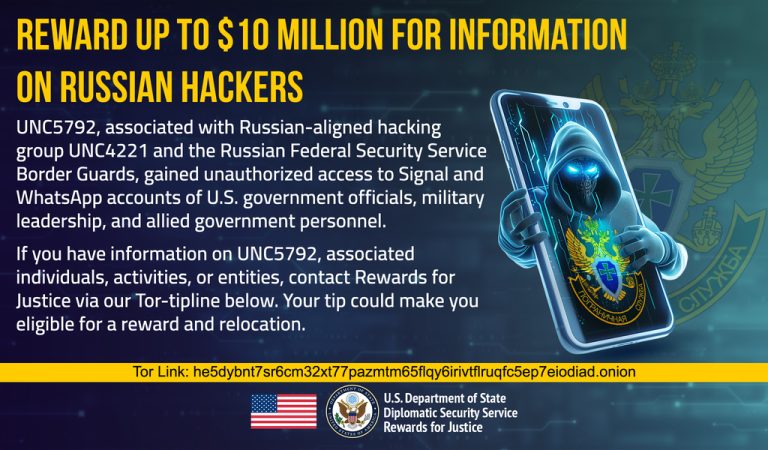
The U.S. offers a $10 million reward for UNC5792, a Russian FSB-linked group behind Signal and WhatsApp phishing of officials.
A threat actor exploited a Cisco SD-WAN zero-day (CVE-2026-20245) to gain root access. Learn how this attack happened and how to secure your networks.

A new WhatsApp malware campaign uses a multi-stage VBScript infection chain to silently install RMM software on victim devices across multiple countries.

Researchers uncovered massive fake shop campaigns targeting Europe. Attackers sell counterfeit goods by impersonating major brands and exploiting World Cup.