
 Do Son
A suspected Indonesian threat actor exploited the Laravel Livewire vulnerability (CVE-2025-54068) to steal credentials from over 6,000 web applications.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.

Operation Endgame disrupts the SocGholish malware network, seizing EUR 41M in crypto and 326 servers. WordPress site owners must act now.

Cyble's Operation FanTrap uncovered a FIFA 2026 fraud ecosystem with nearly 4,000 fake domains pushing ticket scams, streaming lures, and phishing.
Trend Micro tracked a ClickFix malvertising campaign that abused claude.ai shared chat to deliver the MacSync infostealer to Mac developers.

The 2026 national health care fraud takedown charged 455 defendants. Authorities allege these telemedicine fraud schemes cost taxpayers over $6.5 billion.

The GitBait phishing campaign abuses GitHub Pages and the SheetBest API to steal banking credentials from at least 12 Mexican financial institutions.

A massive cloud DNS takeover campaign exploits abandoned enterprise domains to serve Thai gambling content. 163 organizations are currently compromised.
The FBI warns that cyber criminals increasingly use traffic distribution systems to redirect users to malicious websites, phishing pages, and malware scams.

Google uncovers UNC6508 cyber espionage using INFINITERED malware to target US medical and defense research. Learn how to protect your organization.

Attackers exploit ArcGIS Account Recovery flaws. Read this security bulletin to secure your enterprise by disabling default accounts and enabling SMTP.

A new device code phishing campaign abuses Microsoft's OAuth flow to hijack Microsoft 365 accounts, no password stealing needed. How to spot it.

The UNC1151 Gmail phishing campaign by Ghostwriter steals passwords and 2FA codes from Polish targets via fake Google login pages. Stay alert.

Velvet Ant ran Operation Highland for nearly a decade, backdooring PAM and OpenSSH to hide inside an isolated critical infrastructure network.

The FortiBleed campaign exposed working logins for 30,791 Fortinet firewalls across 194 countries. This Fortinet credential leak hits every sector.
OpenAI's June 2026 threat report exposes China influence operations that used banned ChatGPT accounts to target US AI and tariff debates.

A WooCommerce payment skimmer mimics Stripe to steal card data during real checkouts. Inside this Magecart-style attack and how merchants can fight back.

Threat actors are using AI social engineering lures to distribute malware and steal credentials. Learn how fake ChatGPT and DeepSeek campaigns work.

ReliaQuest uncovers OP-512, a China-linked cluster using a unique IIS web shell framework with RSA/RC4 encryption and timestomping.

Mandiant details the UNC3753 vishing campaign targeting US law firms with fake IT calls, RMM abuse, and rapid data theft extortion.
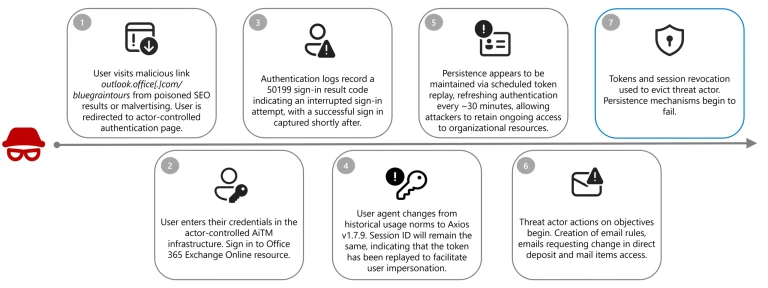
The active Payroll Pirate campaign uses AiTM session hijacking and token replay to target corporate payroll and HR personnel across multiple industries.

A patched WinRAR vulnerability in Ukraine is still exploited via CVE-2025-8088 to deploy GIFTEDCROOK and espionage tools, says Trend Micro.

A massive Conti ransomware guilty plea reveals how these devastating ransomware attacks extorted $150 million from thousands of global victims.