 Do Son
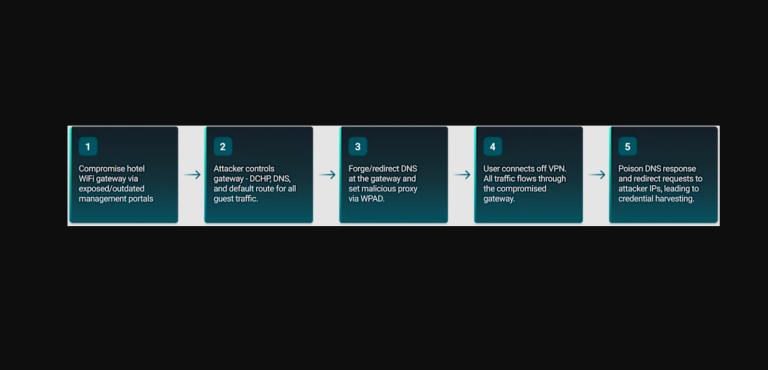
ReliaQuest found hotel Wi-Fi DNS poisoning sending travelers to fake Microsoft 365 pages. Full-tunnel VPN stops the Microsoft 365 account compromise.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
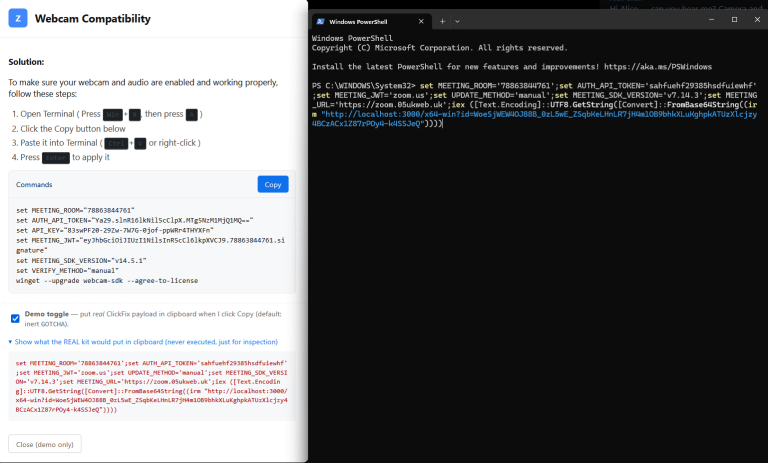
JUMPSEC analyzed the BlueNoroff phishing kit's source code. The DPRK ClickFix attack fakes Zoom and Teams calls to profile and drain crypto wallets.

A TA488 half-click exploit abuses CVE-2026-42897 in Outlook Web Access to drop OWAReaper, a stealthy implant that survives device reimaging.

Insikt Group found four new Golden Chickens malware families, including ChonkyChicken malware, TinyEgg, and a modular plugin variant with ClickFix lures.
Group-IB found an exposed server that revealed JadeProx, a China-nexus cluster running TriBack Loader against targets in Vietnam, Malaysia and Hong Kong.

North Korea's ClickFake Interview campaign targets crypto pros with fake skill tests, dropping the PylangGhost RAT on Windows and GolangGhost on macOS.

VMRay Labs details Operation STANDOFF, a Russian-speaking threat group running malware, a proxy-botnet and AI influence tools behind fake GitHub traffic.

ENKI WhiteHat traced a Kimsuky Gomir variant into South Korean groupware vendors, plus a new DriveTroy backdoor that hides its C2 in Google Drive.

TELESHIM malware hits Middle East governments and abuses Telegram C2 to hide traffic. Zscaler ThreatLabz found the new backdoor and its tooling.
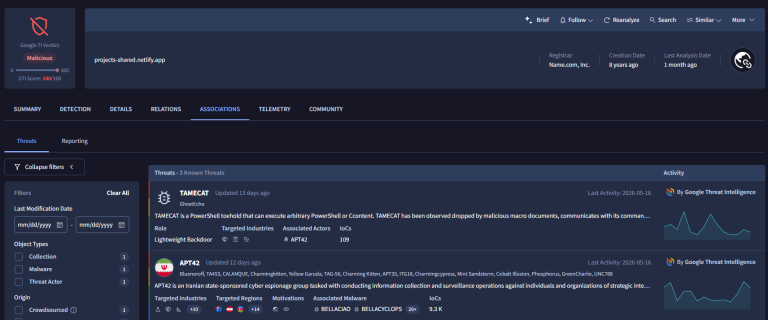
APT42 TAMECAT malware now blends AI-assisted phishing with cloud C2 to steal credentials from defense and nuclear-sector targets.

Elastic found a Contagious Interview campaign using fake coding interviews and SVG steganography to steal developer credentials and crypto wallets.

DOJ charged a Chinese national with wire fraud conspiracy in a gift card fraud scheme that shipped electronics from a New Hampshire warehouse to China.
Varonis Threat Labs analyzed Dolphin X stealer, a forum-sold RAT with 300+ credential targets and an AI Profiler that ranks victims for operators.
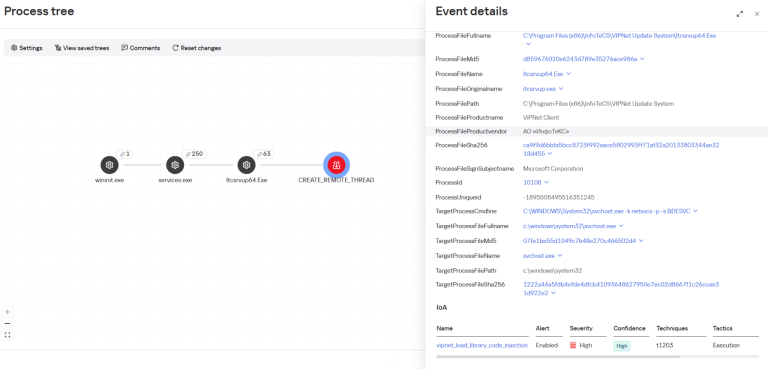
The HelloNet campaign spreads malware through the ViPNet update system, hitting Russian government and energy firms. Kaspersky suspects a China link.

The DoNot APT hit Bangladesh military targets with a fake officer biography. Cyderes traced a live, multi-stage implant to active C2 servers.

A GitHub Actions abuse campaign turned thousands of workflows into cPanel and WHM exploitation infrastructure, harvesting cloud and payment credentials.

Starland RAT is new malware from Russian-speaking actor UAT-11795. It steals crypto wallets and credentials via fake Zoom and WebEx installers.

Discover the details behind the Nextcloud website hacked incident. Hackers exploited a vulnerability to redirect users to a dangerous phishing domain.
An AI-powered botnet was migrated in six minutes by a solo actor using Gemini CLI. TrendAI Research analyzed 200 session logs from "bandcampro".
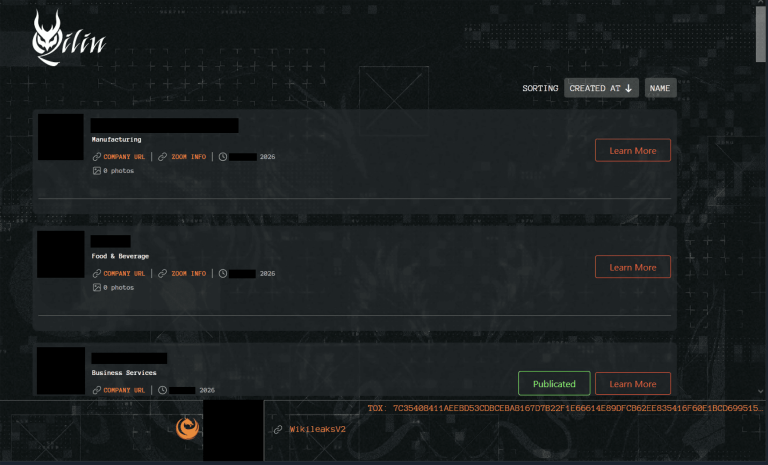
Arctic Wolf links Qilin ransomware attacks to CVE-2026-0257, a Palo Alto GlobalProtect auth bypass used for initial access. Patch PAN-OS now.

The US seized 1,000+ domains in an illegal World Cup streaming crackdown, part of global streaming domain seizures under Operation Offsides.

Proofpoint details OAuth client ID spoofing, a stealthy account enumeration technique probing Microsoft Entra ID without a successful sign-in event.