 Do Son
TL;DR
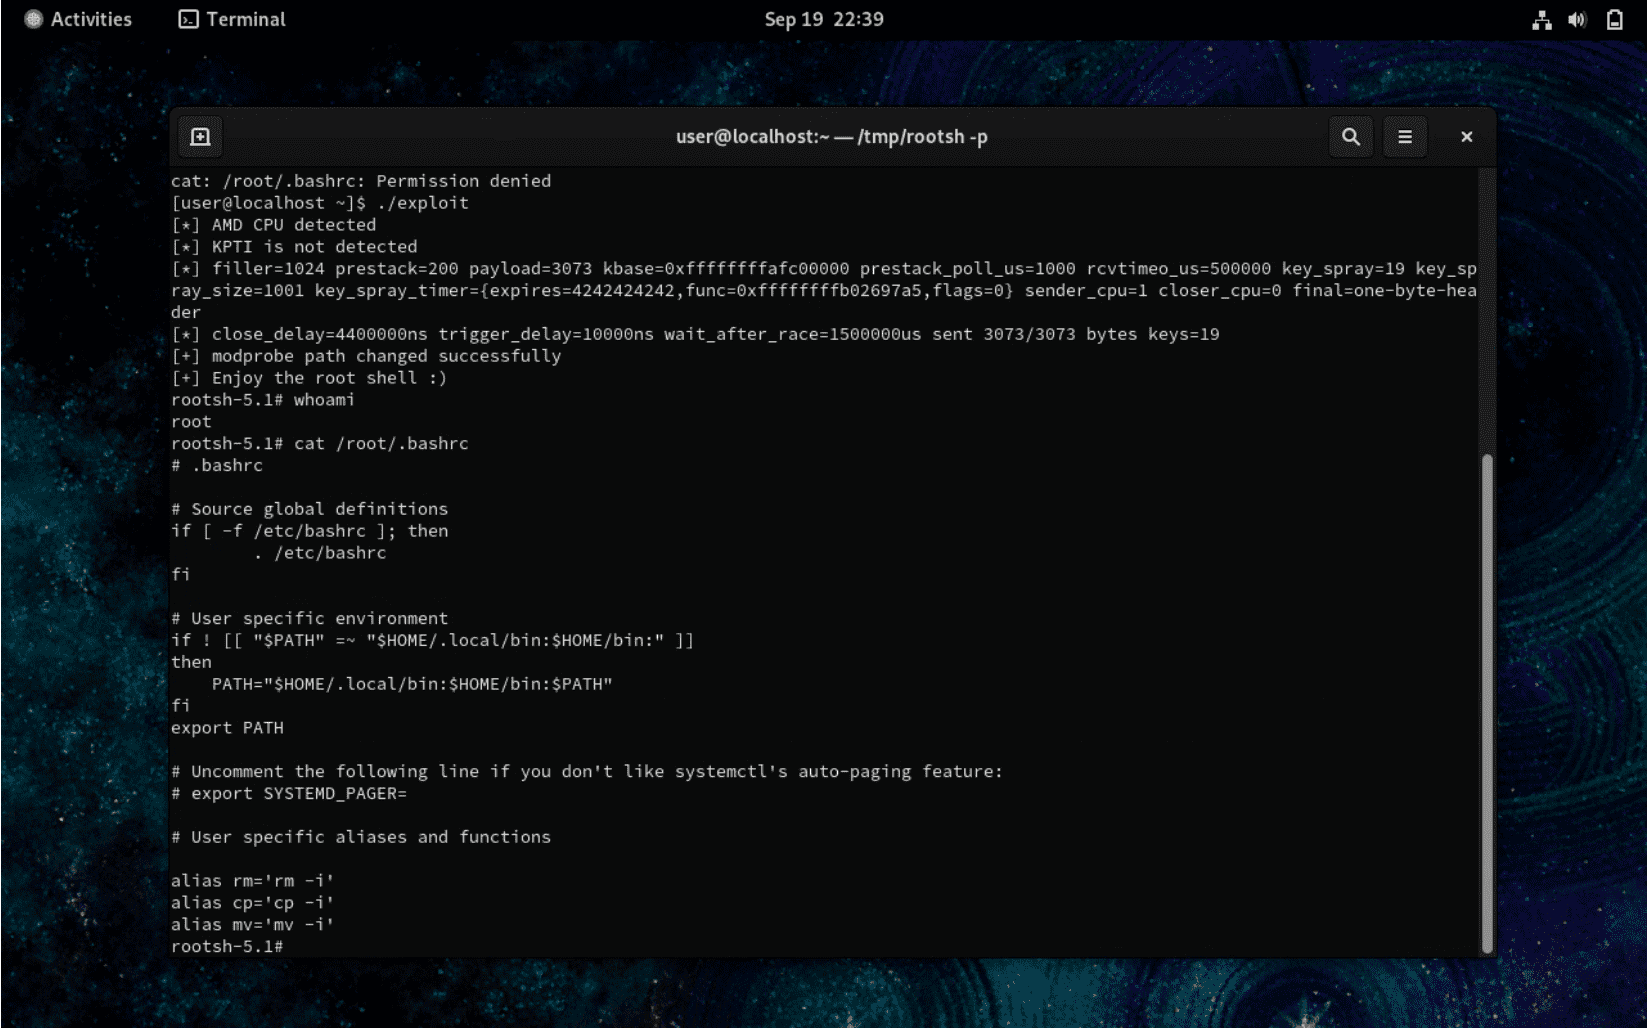
A researcher published RustyTux, a working proof-of-concept for a Linux kernel privilege escalation flaw. It abuses an ESP-in-TCP use-after-free race in the strparser and espintcp code. Both the vulnerability details and the exploit code are now public. No exploitation in the wild has been confirmed.
- CVE: CVE-2026-23239
- CVSS: 7.8 (High · CVSSv3)
- Product: Linux
- Affected: e27cca96cd68fa2c6814c90f9a1cfd36bb68c593, 5.6
- Impact: espintcp: Fix race condition in espintcp_close()
- Status: No confirmed exploitation yet
- Patched in: f7ad8b1d0e421c524604d5076b73232093490d5c, 664e9df53226b4505a0894817ecad2c610ab11d8, 022ff7f347588de6e17879a1da6019647b21321b, e1512c1db9e8794d8d130addd2615ec27231d994 (+4 more)
- EPSS: 0.1% (30-day)
- Action: Update to f7ad8b1d0e421c524604d5076b73232093490d5c, 664e9df53226b4505a0894817ecad2c610ab11d8, 022ff7f347588de6e17879a1da6019647b21321b, e1512c1db9e8794d8d130addd2615ec27231d994 (+4 more) now
Track every Linux kernel CVE the moment it's exploited.
Get free email alertsWhy This Linux Kernel Privilege Escalation Matters
The espintcp module ships in kernels from many major distributions. As a result, this Linux kernel privilege escalation reaches common server and desktop builds. The developer confirms the race is present as of September 2026 in standard kernels for CentOS Stream 9 and Ubuntu 26.04 LTS.
The bar to attempt it is low. An unprivileged local user can reach the flaw without any Linux capabilities. You can review the publicly released RustyTux proof-of-concept on GitHub, which was disclosed alongside the underlying race on the Linux kernel mailing list.
How the Attack Works
The race centers on socket teardown. An active receive parser overlaps with a closing socket. The exploit rearms strparser’s message timer after strp_done() has already canceled it. That timing window frees the espintcp context while another path still uses it.
Next, the exploit reclaims the freed object with attacker-shaped data. It first derives the randomized kernel base through an x86 prefetch timing side channel. A replacement callback then redirects a kernel path to gain root. The technique is timing-sensitive, so delays must be tuned per target.
Affected Versions
The public PoC targets a specific CentOS Stream 9 kernel build, 5.14.0-745.el9. However, the developer notes the race also affects Ubuntu 26.04 LTS standard kernels. The associated upstream issue is tracked as CVE-2026-23239, rated High severity (CVSS 7.8). A crash-only variant can trigger an unprivileged kernel denial of service instead.
Patch and Mitigation Steps
Apply your distribution’s latest kernel updates without delay. The upstream fix replaces the unsafe work-cancel logic in the espintcp close path. Until you patch, restrict local access on shared systems. Where espintcp is not needed, blocking the module load reduces exposure. Reboot after updating to load the fixed kernel.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
