
 Do Son
A Linux SCTP kernel use-after-free (CVE-2026-64564) enables local privilege escalation and full container-to-host escape.
use after free

PoC exploit code is public for CVE-2026-64561 (Zapscape), a KVM escape that runs commands with kernel root privilege on the host. Details inside.

Chrome's stable channel update patches 41 flaws, including 6 critical use-after-free and memory bugs. Update to 151.0.7922.108 now.

A Linux kernel vulnerability, CVE-2026-53264, lets a local user run arbitrary code via a net/sched use-after-free. A public PoC is now available.

Debian 13 pushes a kernel update fixing 68 vulnerabilities including four critical use-after-free flaws. Upgrade to kernel 6.12.100-1 and reboot now.
A public PoC now details CVE-2026-42530, an NGINX HTTP/3 RCE from a QPACK use-after-free. Upgrade to NGINX 1.31.2 to close the flaw now.

Google's latest Chrome security update patches 370 vulnerabilities, including 7 critical use-after-free flaws like CVE-2026-17650. Update Chrome now.

Node.js patched 11 vulnerabilities in its July 2026 release. The high-severity bugs include a HTTP/2 use-after-free (CVE-2026-56848). Update now.

Apache Fory vulnerabilities hit Java, C++, and Rust deserialization, including CVE-2026-64606. Upgrade to Fory 1.4.0 to fix all four flaws.

Google's Chrome security update fixes four high-severity bugs, including CVE-2026-16807, a Codecs flaw that could enable a sandbox escape. Update now.

Google's Chrome security update patches 12 high-severity flaws in Chrome 150, including V8 and WebAudio bugs. Update to 150.0.7871.181 today.

Chrome security update 150.0.7871.128 patches 7 flaws, including three critical use-after-free bugs in CameraCapture, GPU, and Network. Update now.
Google's Chrome security update 150.0.7871.124 fixes 15 flaws, including critical use-after-free bugs CVE-2026-15764 and CVE-2026-15765. Update now.

X.Org Server ships fixes for two flaws, including CVE-2026-56000, a CVSS 9.0 use-after-free. Update xorg-server and Xwayland now.
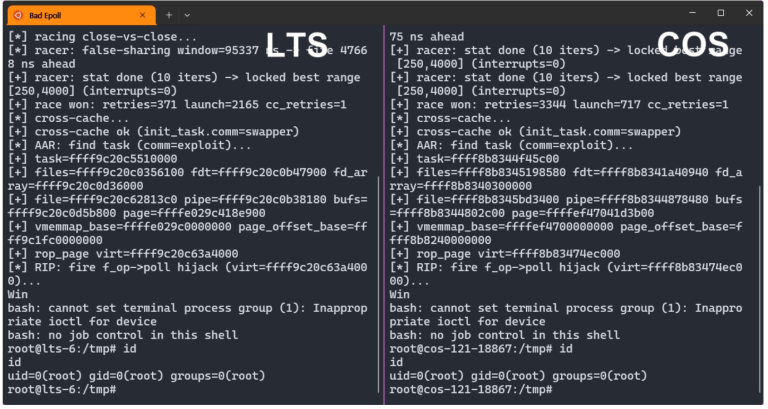
Bad Epoll (CVE-2026-46242) is a Linux kernel UAF enabling root privilege escalation. Full details and PoC exploit code are now public. Patch now.
Three FreeBSD privilege escalation flaws, including a kernel use-after-free, let local users gain root. Patch FreeBSD 14 and 15 now.
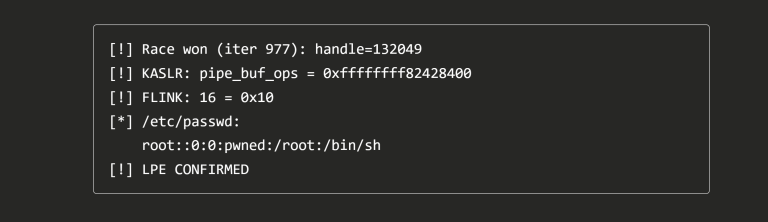
Public PoC and write-up detail a Linux kernel privilege escalation flaw (CVE-2026-46215) in DRM GEM. A local user gets root in ~99% of runs.

Google's latest Chrome security update fixes 27 flaws, including two critical use-after-free bugs. Update to 150.0.7871.114 now.

Foxit fixed 28 flaws in Foxit PDF Reader and PDF Editor. Twenty allow arbitrary code execution via crafted PDFs. Update to 2026.1.2 now.

OpenSSH 10.4 ships eight security fixes, including a client use-after-free (CVE-2026-60002) plus SFTP and SCP path bugs. Update now.
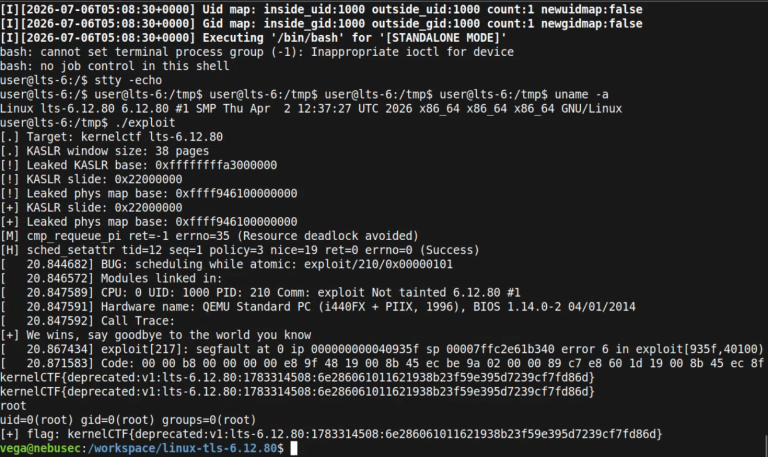
Researchers disclosed GhostLock (CVE-2026-43499) with public PoC code. The 15-year Linux kernel bug enables privilege escalation and container escape.
A Linux kernel vulnerability (CVE-2024-26582) has a public PoC that turns a TLS use-after-free into a root shell. Details and exploit are out.