 Do Son
TL;DR
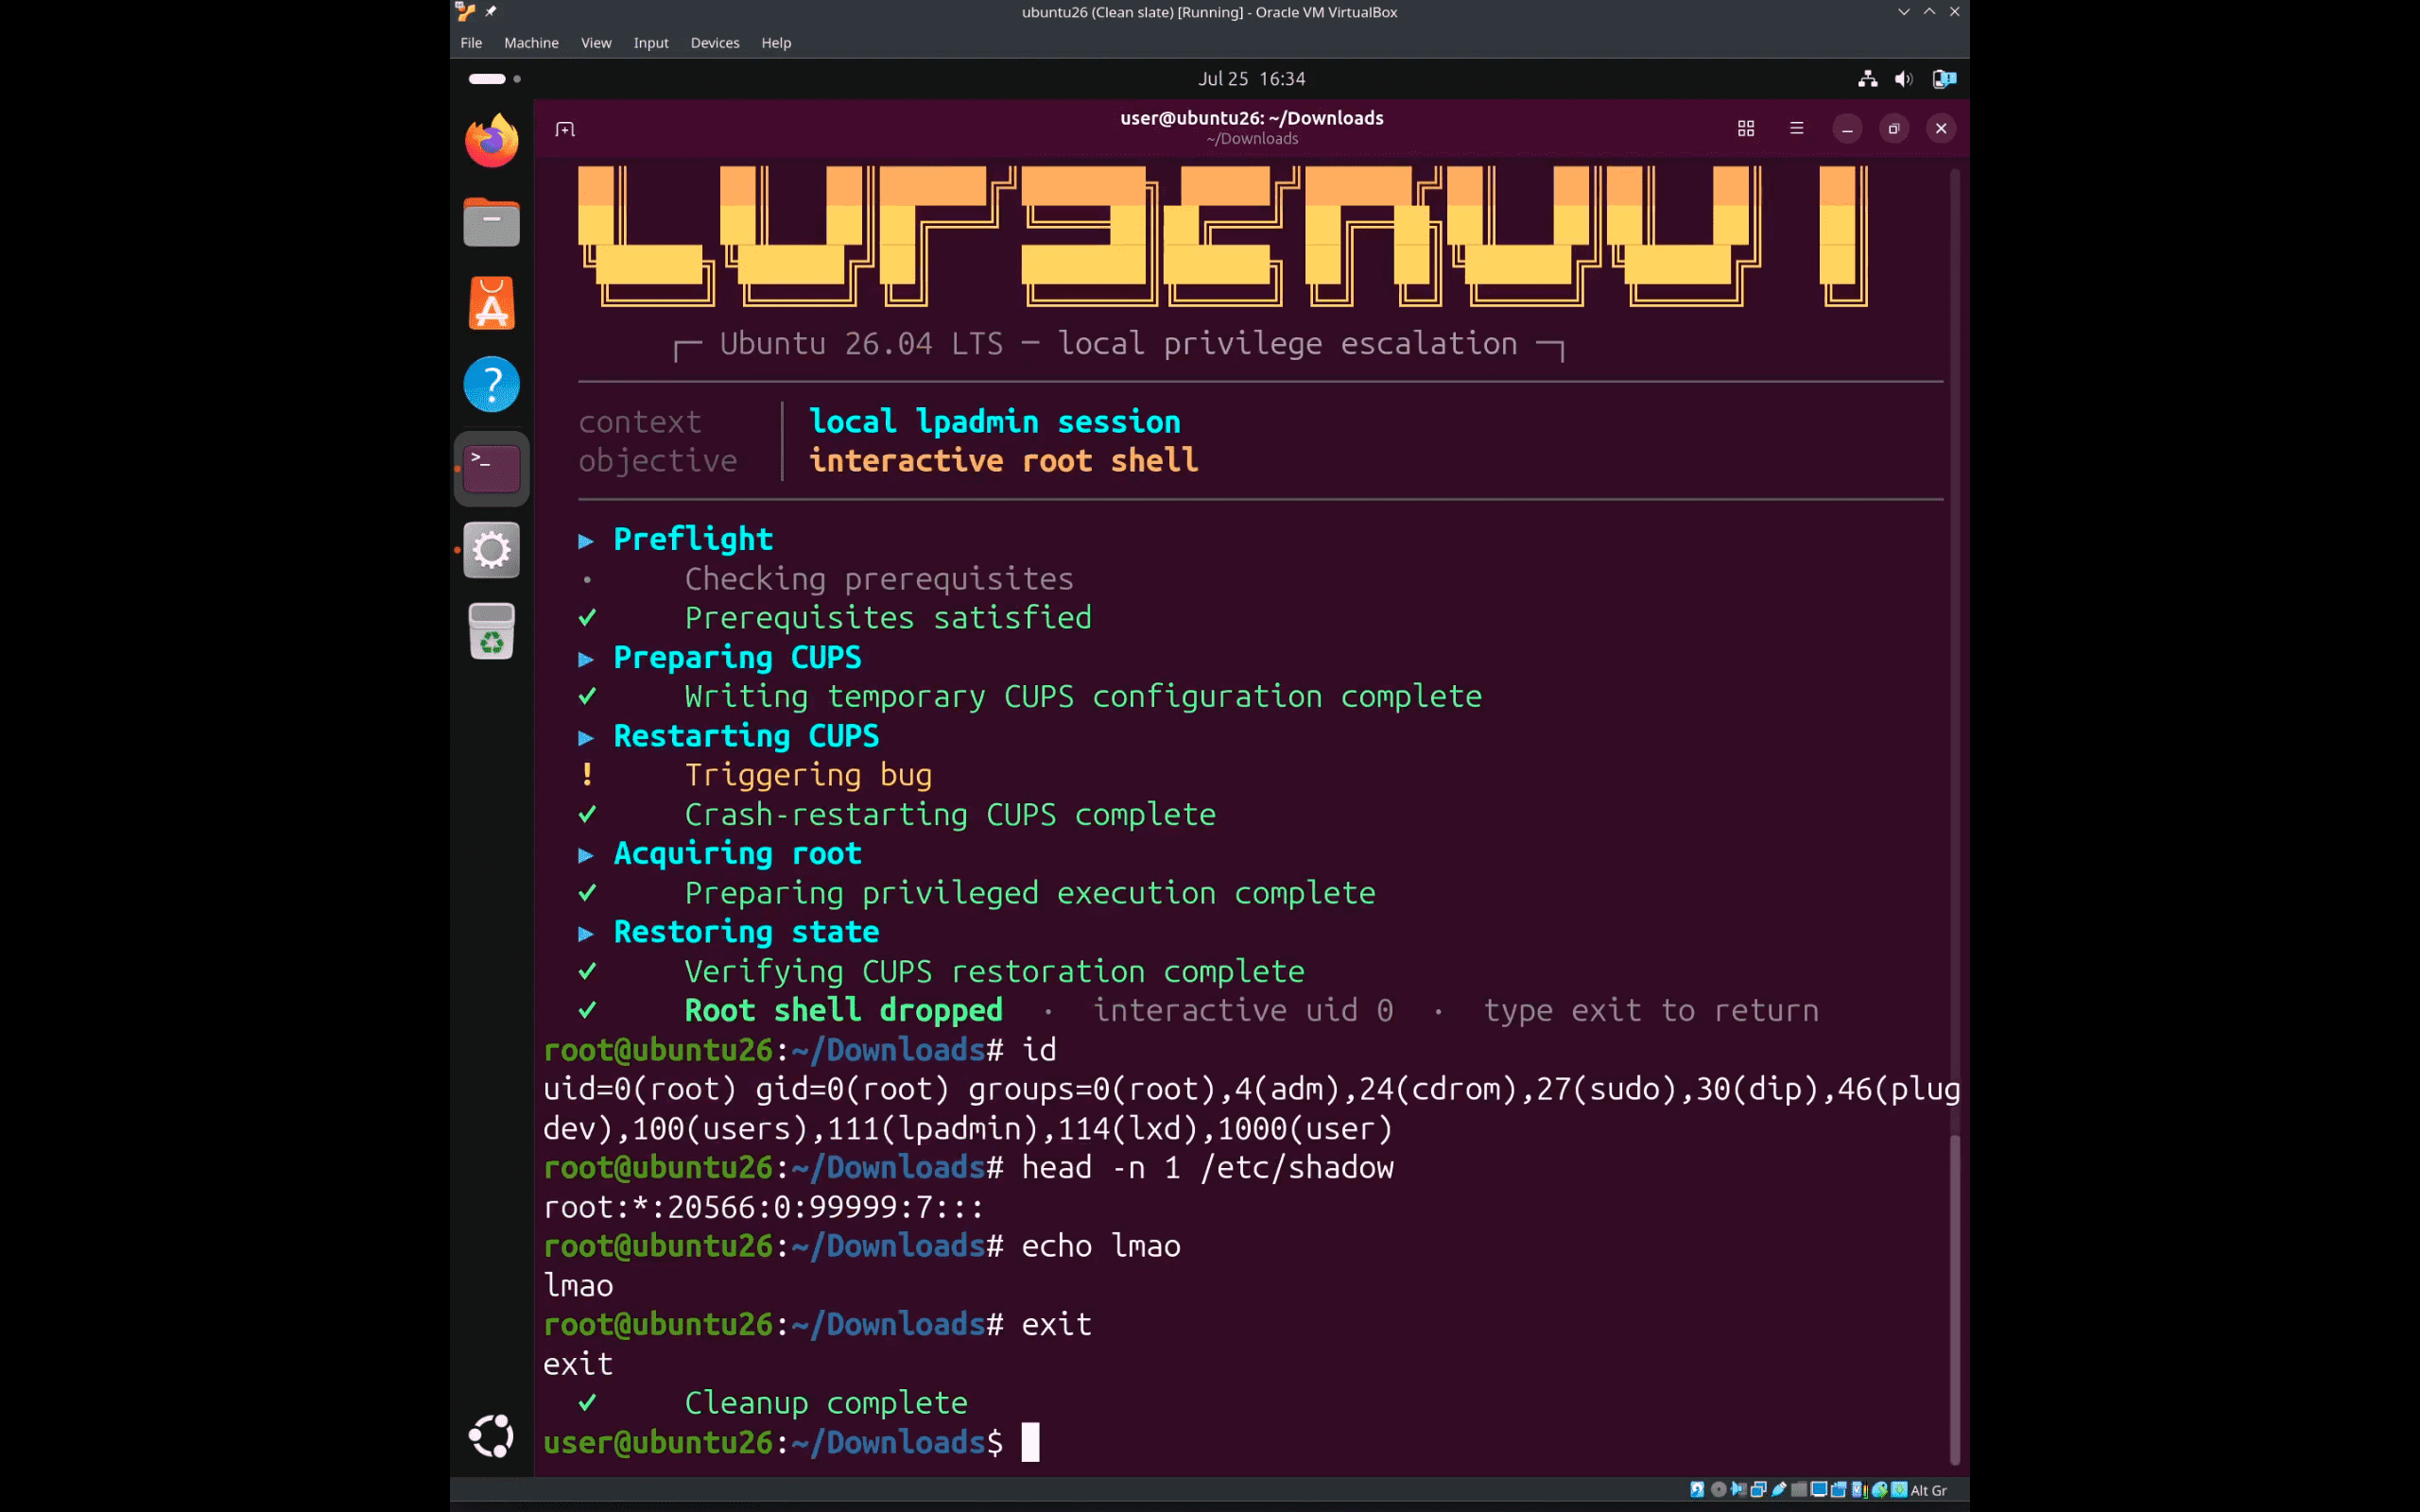
A researcher published cups2root, a working proof-of-concept that escalates a local lpadmin user to root on CUPS. The exploit chains several configuration and privilege-boundary flaws. No CVE, vendor advisory, or patch exists yet. The PoC code is already public on GitHub.
Track every CVE that hits your stack the moment it's exploited.
Get free email alertsWhy This CUPS Privilege Escalation Matters
CUPS ships on most Linux desktops and many servers. As a result, the lpadmin group is common on real systems. This CUPS privilege escalation turns that ordinary group membership into full root access. Rick de Jager of the V12 security team found the flaw and named it cups2root.
The disclosure stands out for one reason: the details and the exploit are already out. You can review the published cups2root proof-of-concept on GitHub. Because the code is public, the barrier to abuse is low on unpatched systems.
user → root privesc 0-day in CUPS
a free PoC while we wait for some bigger disclosures to go through 😇 pic.twitter.com/SvLxA1zurs
— V12 (@v12sec) September 17, 2026
How the Attack Works
The chain abuses the CUPS serial backend, which runs as root. First, the PoC creates a raw serial printer whose device URI points at the CUPS configuration file. Print data then overwrites that file from a fixed byte offset. That write redirects key CUPS paths, including ServerBin, into an attacker-writable directory.
Next, a malformed IPP request crashes the daemon. systemd restarts CUPS with the modified configuration. Finally, the daemon runs a replacement helper binary as root, which installs a setuid shell and restores the original files. The result is an interactive root shell that cleans up its own artifacts on exit.
Affected Versions and Exploitation Status
The PoC targets Ubuntu systems that use systemd, run a local CUPS service, and enable the serial backend. It supports both AMD64 and ARM64. No CVE has been assigned at the time of writing, and no CVSS score has been published. A public proof-of-concept exists, but no exploitation in the wild has been confirmed.
Patch and Mitigation Steps
No vendor patch is available yet. Until one ships, defenders should rely on configuration hardening. Restrict lpadmin membership to trusted administrators only. Disable the serial backend where printing does not need it. Keep CUPS bound to localhost, and watch OpenPrinting for a fixed release. Apply that update as soon as it lands.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
