CISA Warns of Critical Flaws in dcm4chee Medical Archive and Unpatched EseeCloud IP Cameras
 Do Son
TL;DR
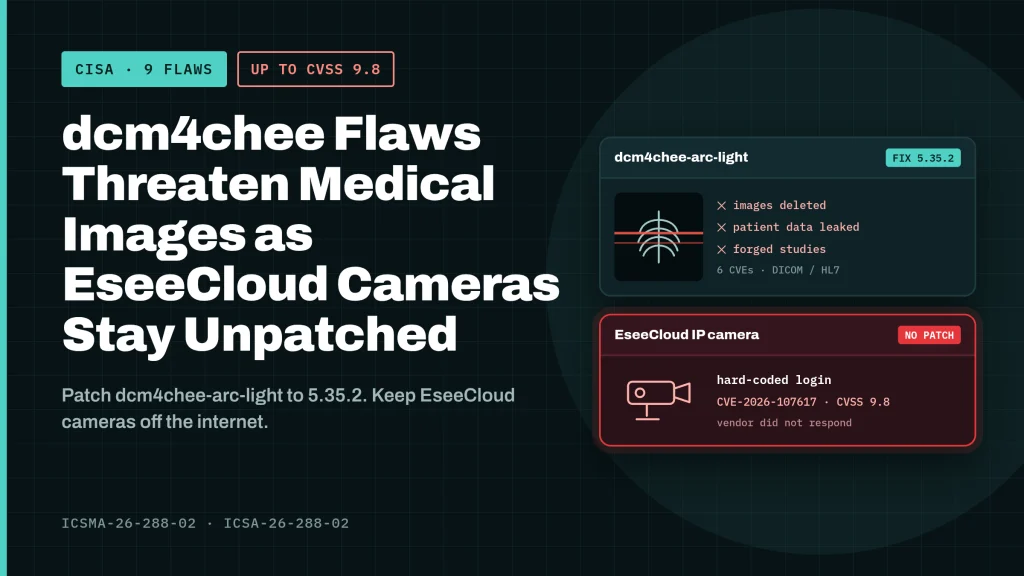
CISA published two advisories on October 15, 2026, covering nine flaws. Six dcm4chee vulnerabilities could expose patient data or wipe medical images, and J4Care has a fix. However, three EseeCloud IP camera flaws, including a CVSS 9.8 hard-coded credentials bug, remain unpatched.
- Total: 9 CVEs
- Severity: 3 Critical · 4 High · 2 Medium
- Actively exploited: None confirmed
- Highest severity: 9.8 (Critical · CVSSv3) — CVE-2026-107617
- Action: Apply the latest security updates now
Notable CVEs
| CVE | CVSS (CVSSv3) | Type | Fixed in | Status |
|---|---|---|---|---|
| CVE-2026-107617 | 9.8 | Guangzhou Juan IoT Technology EseeCloud Use of Hard-coded Credentials | — | Not exploited |
| CVE-2026-105279 | 9.1 | dcm4che Missing Authentication for Critical Function | 5.35.2 | Not exploited |
| CVE-2026-97851 | 9.1 | dcm4che Missing Authorization | 5.35.2 | Not exploited |
| CVE-2026-105667 | 7.5 | dcm4che Missing Authentication for Critical Function | 5.35.2 | Not exploited |
| CVE-2026-107621 | 7.5 | dcm4che Loop with Unreachable Exit Condition | 5.35.2 | Not exploited |
| CVE-2026-105273 | 7.5 | dcm4che Loop with Unreachable Exit Condition | 5.35.2 | Not exploited |
| CVE-2026-101021 | 7.5 | dcm4che Inefficient Algorithmic Complexity | 5.35.2 | Not exploited |
| CVE-2026-97858 | 5.3 | Guangzhou Juan IoT Technology EseeCloud Improperly Controlled Modification of Dynamically-Determined Object Attributes | — | Not exploited |
Why It Matters
dcm4chee-arc-light is an open-source DICOM archive. Hospitals and clinics use it to store and share medical images such as X-rays and scans. Tampered or missing images can delay care. In the CISA medical advisory ICSMA-26-288-02, the agency warns that exploitation “could allow an attacker to delete stored medical images, disclose patient information, inject forged studies, reassign patient records, overwrite files, and cause a denial-of-service condition.”
Meanwhile, EseeCloud cameras serve the energy, communications, transportation, finance and government sectors worldwide. CISA says these flaws “could allow an attacker to gain control over affected IP cameras.”
How the Attacks Work
dcm4chee: missing authentication and authorization
- CVE-2026-97851 (CVSS 9.1): a storage REST service lacks authorization checks. As a result, an attacker can mark stored objects for deletion while the database still lists them.
- CVE-2026-105279 (CVSS 9.1): by default, the archive accepts DICOM connections from unregistered systems. CISA says a remote peer can “enumerate and retrieve patient information and medical images.” It can also file fake studies under real patients.
- CVE-2026-105667 (CVSS 7.5): the HL7 listener accepts patient-merge messages without authentication. Notably, “the archive’s unmerge does not reverse this.”
dcm4chee: denial of service
Three more dcm4chee vulnerabilities (CVE-2026-107621, CVE-2026-105273 and CVE-2026-101021) each score 7.5. Crafted JPEG, MP4 or multipart input can trap the parser in a loop or burn CPU.
EseeCloud: hard-coded credentials
CVE-2026-107617 scores 9.8. According to CISA, “an attacker can use a hard-coded credential to log in to EseeCloud devices.” Two medium flaws (CVE-2026-97858 and CVE-2026-105664) let attackers rebind devices to their own accounts and discover registered devices at scale.
Exploitation status
For both advisories, CISA states that “no known public exploitation specifically targeting these vulnerabilities has been reported.” No public proof-of-concept has been confirmed either.
Affected Versions
- J4Care dcm4chee-arc-light: 5.35.1
- EseeCloud App: 4.9.6 and earlier
- EseeCloud Firmware: 4.9.86.0 and earlier
Patch and Mitigation Steps
dcm4chee
J4Care “recommends users implement release 5.35.2 or later.” Hospitals should also restrict DICOM and HL7 access to known, trusted systems.
EseeCloud
No fix exists. In the CISA advisory ICSA-26-288-02, the agency notes that Guangzhou Juan IoT Technology “did not respond to CISA’s coordination attempts.” Until a patch arrives, keep these cameras off the internet and place them behind firewalls. Where possible, consider replacing them.
Researchers Abhinav Agarwal and Donghyeon Lee reported the flaws to CISA. Given the critical scores, healthcare teams should treat the dcm4chee vulnerabilities as an urgent patch.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
