 Do Son
Critical HPE ALE vulnerabilities threaten enterprise networks. Update HPE ALE vulnerabilities now to prevent unauthorized access and remote code execution.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
IBM DataStage vulnerabilities expose cloud environments to RCE and DoS. Upgrade Cloud Pak for Data to version 5.4 patch 7 immediately.
Google Chrome 154 patches 108 security vulnerabilities, including critical memory corruption flaws. Update your browser immediately to stay secure.
SolarWinds Observability vulnerabilities allow RCE via CVE-2026-28324. Update to version 2026.2.3 to secure your monitoring infrastructure today.
Technical details and a PoC for the D-Link DAP-1360 vulnerability (CVE-2026-95675) are public. Learn how this unauthenticated flaw impacts legacy routers.
NVIDIA patched critical NVIDIA Infrastructure Controller vulnerabilities across Linux builds. Learn how CVE-2026-65113 impacts systems and update now.
An exploited BIG-IP APM vulnerability tracked as CVE-2026-94127 allows RCE attacks. Secure your BIG-IP APM vulnerability deployments with new F5 hotfixes.
A critical ManageEngine ADSelfService Plus vulnerability (CVE-2026-74849) allows system compromise. Update to build 7001 to secure your endpoints.
An exploited Check Point VPN vulnerability allows remote code execution. Patch this Check Point VPN vulnerability now to block active in-the-wild attacks.
WordPress 7.1.2 patches a critical WordPress RCE vulnerability (CVE-2026-87902). Update your site to prevent conditional remote code execution.
A critical exploited Check Point Management vulnerability (CVE-2026-93616) allows attackers to execute arbitrary scripts. Secure your servers now.
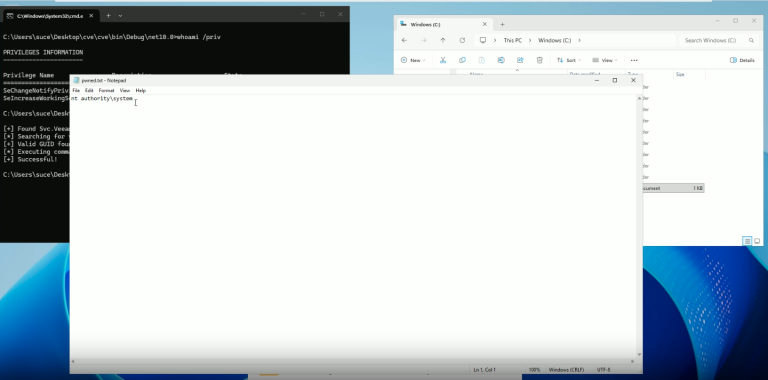
A critical exploited Veeam Agent vulnerability (CVE-2026-32996) is under active attack. Public PoC exploit code has been disclosed. Update systems now.
An exploited VeloCloud vulnerability with a 10.0 CVSS score hits Arista appliances. Patch the critical VeloCloud vulnerability to stop active attacks.
Public PoC exploit details emerge for critical D-Link DIR-822A vulnerabilities. Learn how these D-Link DIR-822A vulnerabilities impact unpatched devices.
Pega patched a SAML authentication bypass in Pega Platform, rated Critical 9.5 and High 7.0. No CVE, no known compromise. See affected versions and fixes.
CISA warned of an exploited Zyxel switch vulnerability in GS1900 devices. Patch the Zyxel switch vulnerability now to prevent network compromise.
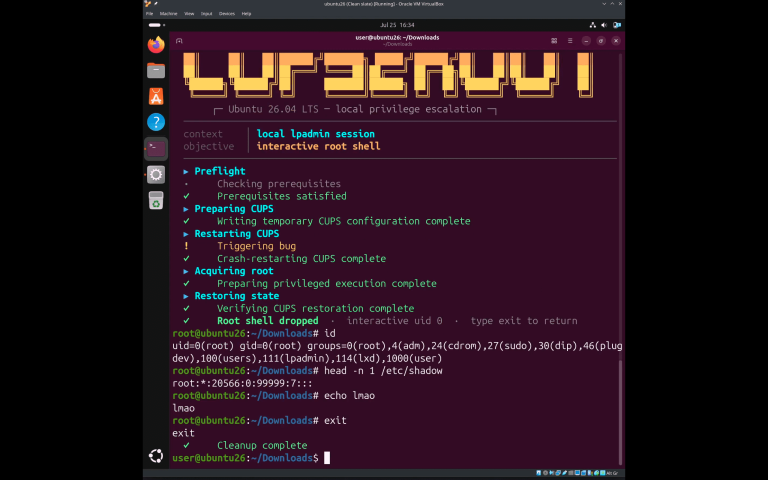
A public PoC exploit, cups2root, chains a CUPS privilege escalation to take lpadmin users to root. No CVE or patch yet. See the mechanism and mitigations.
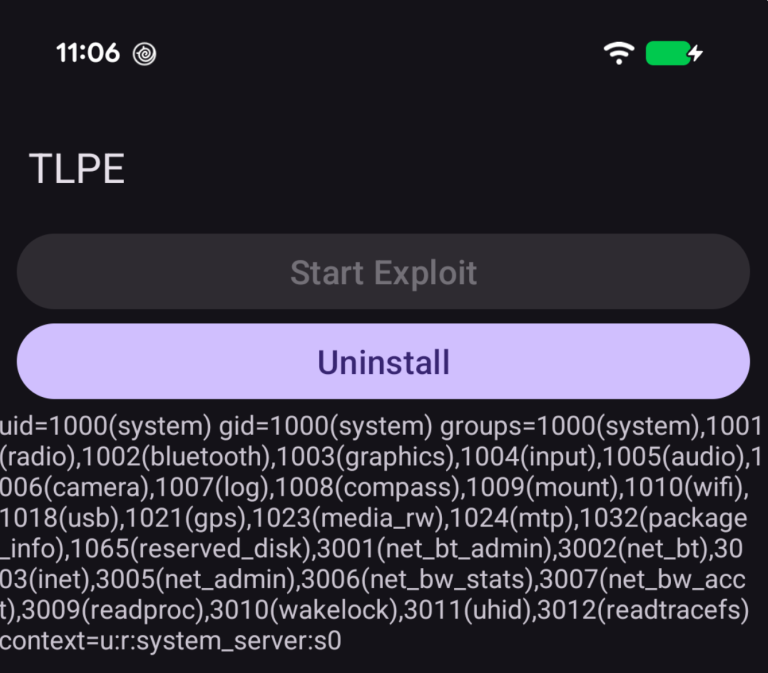
A critical Android Telecom vulnerability (CVE-2026-49881) allows remote code execution. Read the analysis and learn how to secure your device today.
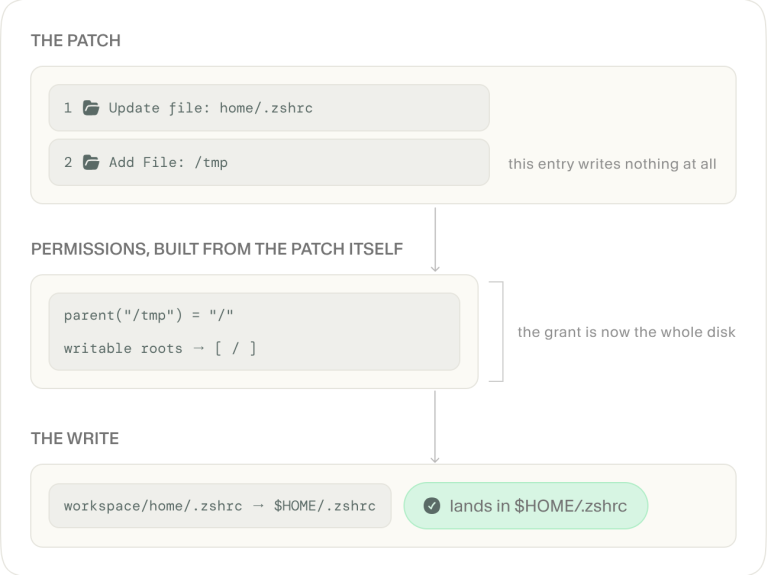
Discover the critical OpenAI Codex sandbox escape vulnerability. Learn how attackers bypass read-only modes and how to patch your CLI and desktop apps now.
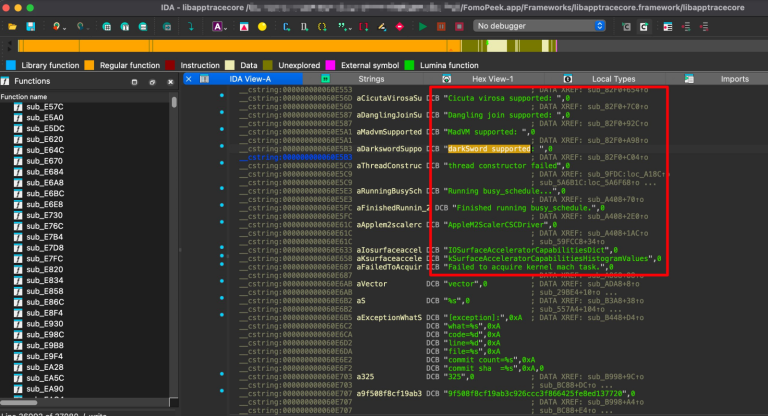
SlowMist warns the FomoPeek malware hides an iOS kernel exploit that steals crypto private keys and seed phrases. Update iOS and move funds now.
Multiple critical IBM Guardium vulnerabilities expose servers to remote attacks. Update to fix these IBM Guardium vulnerabilities and secure your data.
Critical MongoDB driver vulnerabilities, including CVE-2026-93762, expose systems to data loss and DoS. Learn about these flaws and patch immediately.