 Do Son
An ASUS Control Center vulnerability, CVE-2026-75754 (CVSS 10), gives unauthenticated attackers a root shell. Update to v3.1.0.9 now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Apache released version 1.21.0 to patch critical Apache Allura security vulnerabilities. Update now to protect against XSS, SSRF, and data exposure flaws.
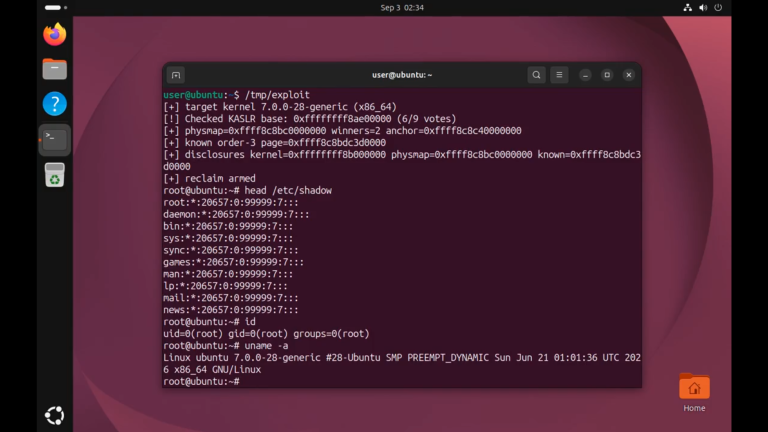
Security researchers released a Linux CVE-2026-52924 PoC exploit. Check flaw details and patch instructions to secure your systems against root takeovers.
A TP-Link Archer AX55 vulnerability (CVE-2026-18167) risks remote code execution via EasyMesh buffer overflow. Update to build 20260527 now.
Plex urges an urgent security update to Media Server 1.43.3 and Desktop 1.115.0. NAS and Docker users may need to patch manually.
CVE-2026-14894, a critical Super Forms vulnerability, is exploited in the wild. The 9.8 CVSS file upload flaw enables unauthenticated remote code execution.
A critical WHMCS security update fixes CVE-2026-67399 and CVE-2026-67398. Apply the patch now to prevent remote code execution and data leaks.
SonicWall patched critical SonicWall NSM vulnerabilities in on-prem software. Update now to protect your network against remote code execution.
Google patched a Chrome zero-day vulnerability currently exploited in the wild. The update resolves a severe V8 type confusion flaw (CVE-2026-85046).
A public announcement exists for the Cisco Secure Email vulnerability pair in S/MIME decryption, plus a Cisco phone SIP denial-of-service flaw.
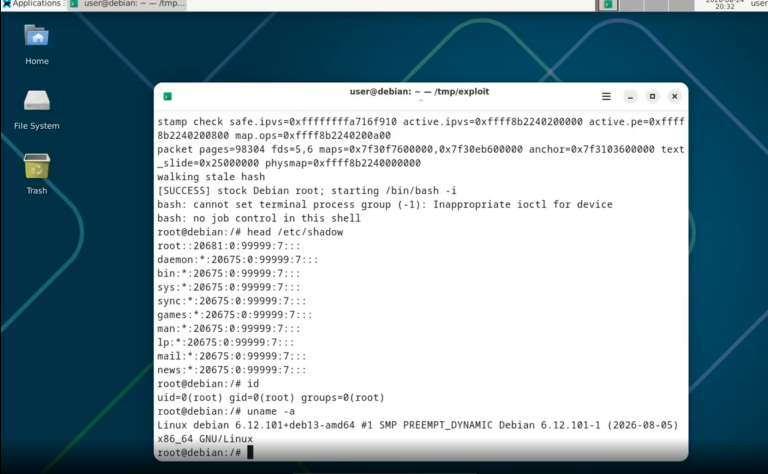
CVE-2026-80714 (CVSS 9.8) is a Linux kernel IPVS use-after-free with public PoC code enabling root privilege escalation on Debian. Patch now.
CVE-2026-59346, a critical VMware Workstation vulnerability, lets an attacker escape a guest VM and execute code on the host. Broadcom rates it 9.3 CVSS.
Cisco fixed critical Cisco IOS XR vulnerabilities discovered by AI models. Update systems to patch Cisco IOS XR vulnerabilities.
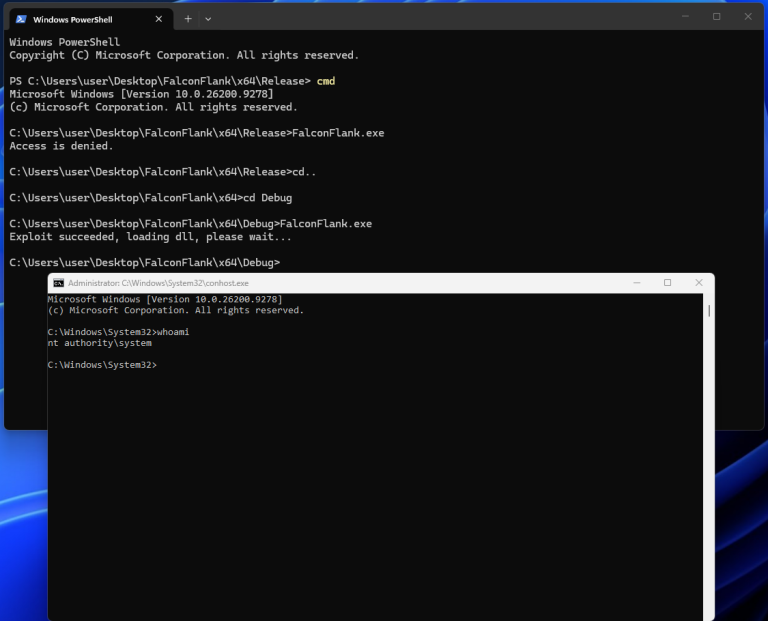
A researcher claims a CrowdStrike Falcon vulnerability enabling privilege escalation and published a PoC. CrowdStrike has not confirmed it; no CVE exists.
CISA added critical CISA KEV vulnerabilities to its list. Patch these CISA KEV vulnerabilities now to block ongoing cyberattacks.
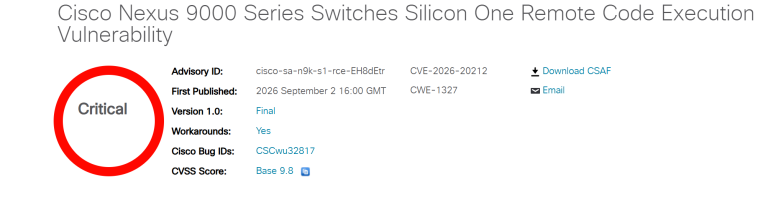
CVE-2026-20212, a critical Cisco Nexus 9000 vulnerability, lets an unauthenticated attacker gain remote code execution with root privileges. CVSS 9.8.
CVE-2026-43748 (CVSS 9.8) is an Apple ANE kernel out-of-bounds write reachable from a sandbox. Details and macOS/iOS PoC code are public. Update now.
CVE-2026-73749, a critical HPE AOS-CX vulnerability, enables unauthenticated remote code execution at CVSS 9.8. HPE patched 31 flaws across its switches.
Jenkins fixed a deserialization flaw leading to remote code execution, plus over 30 more CVEs across core and popular plugins. Update now.
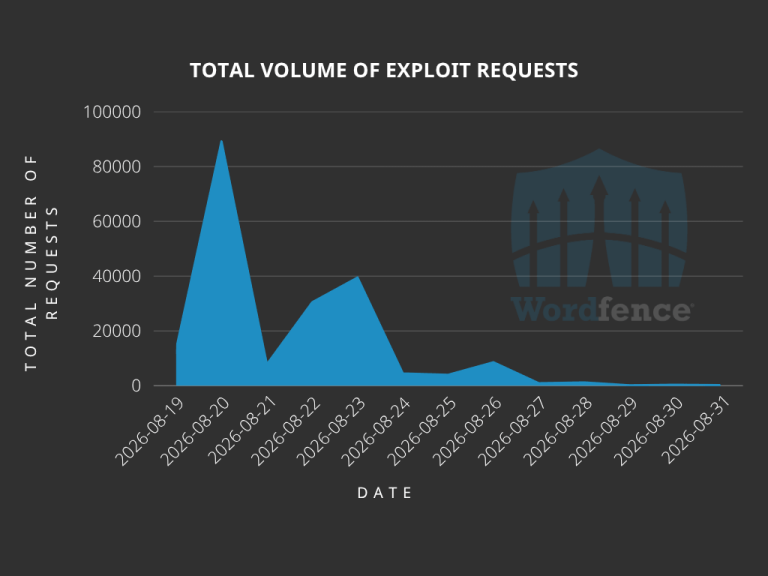
Attackers exploit a critical Elementor Pro vulnerability (CVE-2026-32475) in the wild. Patch this Elementor Pro vulnerability to prevent site takeover.
A Dropbox Lenovo ID SSO flaw let attackers take over accounts with just an email address, no password needed. Dropbox has revoked sessions and hardened login.
Google patched critical Google Chrome vulnerabilities, including CVE-2026-84353. Update your browser now to block potential remote attacks.