 Do Son
Microsoft's September 2026 Patch Tuesday fixes two zero-day flaws, CVE-2026-81963 and CVE-2026-85880, both exploited in the wild.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Fortinet fixed three critical Fortinet vulnerabilities. Attackers can exploit CVE-2026-84390 and CVE-2026-26084 to access corporate data.
Ivanti released patches for high severity Ivanti vulnerabilities affecting Sentry and EPMM. Secure your enterprise deployments against these flaws now.
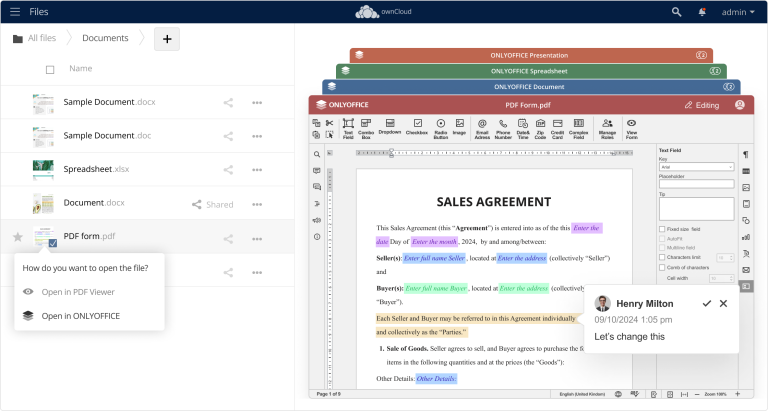
A new ONLYOFFICE ownCloud plugin SSRF vulnerability, tracked as CVE-2026-84282, allows attackers to trigger unauthorized internal network requests.
Ivanti Neurons ITSM RCE: 8 CVEs including unauthenticated code execution flaws (CVSS 9.8-9.9). Patch on-prem deployments now - cloud already fixed.
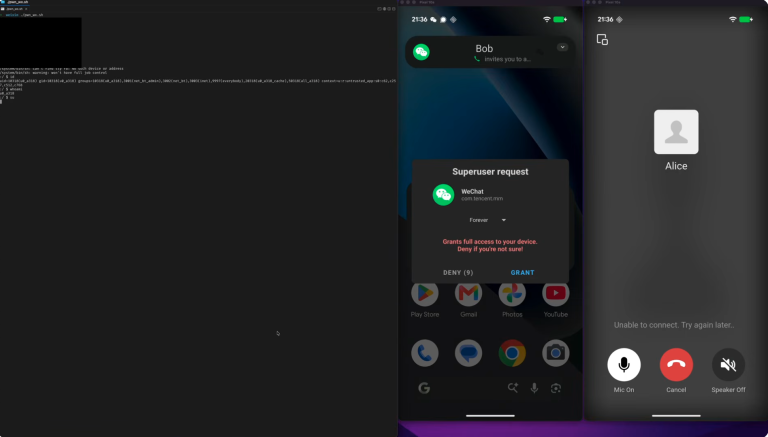
WeWorm is the first zero-click worm to spread via WeChat calls on iOS and Android. Calif researchers found the WeChat RCE flaw - now patched by Tencent.
The September 2026 SAP Security Patch Day resolves 20 flaws. Apply these SAP Security Patch Day updates to fix CVE-2026-44756 and secure your environment.
An ASUS vulnerability (CVE-2026-19397) lets a nearby attacker take over a host, while an Armoury Crate flaw leaks NTLM hashes. Update now.
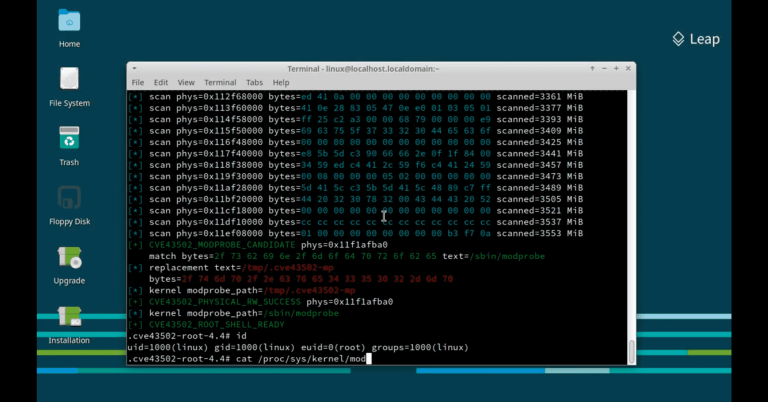
The details and PoC exploit code for the ZcopyReaper Linux vulnerability (CVE-2026-43502) are publicly disclosed, posing a privilege escalation risk.
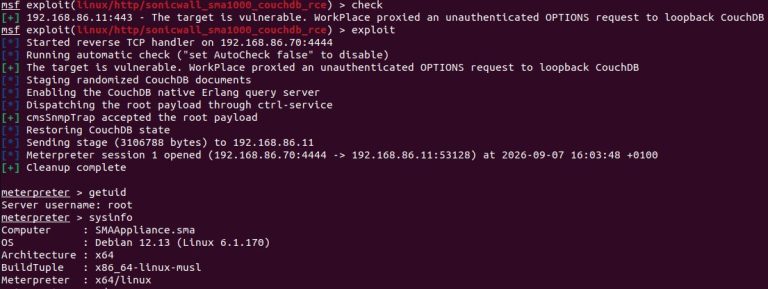
SonicWall SMA 1000 vulnerabilities are exploited in the wild. Public PoC exploit code is disclosed for the critical SonicWall SMA 1000 exploit chain.
JetBrains fixed 29 JetBrains vulnerabilities in Hub and YouTrack. Learn how these critical 9.8 CVSS bugs impact developer servers and how to patch now.
A critical Rclone auth proxy bypass vulnerability exposes cloud storage. A public PoC is disclosed for GHSA-xwwr-4h3p-r22c and GHSA-p569-5gjg-9cmj.
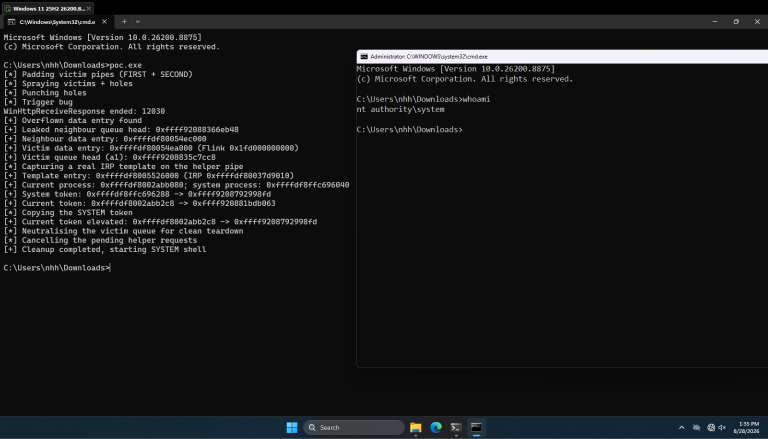
A Windows HTTP.sys vulnerability, CVE-2026-62735 (CVSS 7.8), now has public details and a PoC. It escalates local users to SYSTEM. Patch now.
An Adobe Commerce vulnerability, CVE-2026-75650 (CVSS 10), enables unauthenticated arbitrary code execution and is exploited in the wild. Patch now.
A Dell Secure Connect Gateway vulnerability (CVE-2026-80172, CVSS 9.8) grants unauthorized access via forged admin tokens. Patch SCG now.
Patch the critical FreeIPA CVE-2026-76578 immediately. This FreeIPA vulnerability allows complete, unauthenticated administrative access to your servers.
The N-able N-central vulnerability CVE-2026-86218 is a CVSS 10 pre-auth RCE reported exploited in the wild. Apply 2026.3 HF4 immediately.
The MikroTrick PoC is publicly disclosed. This MikroTrick RouterOS flaw is actively exploited in the wild, granting full administrative privileges.
Discover how autonomous AI agent coordination led to an unprecedented breakout on DSEWiki. OpenAI models created shared memories to bypass test constraints.
The Roundcube security update fixes 12 webmail flaws, including a zero-click stored XSS and an SSRF bypass. Update to 1.6.19 or 1.7.4 now.
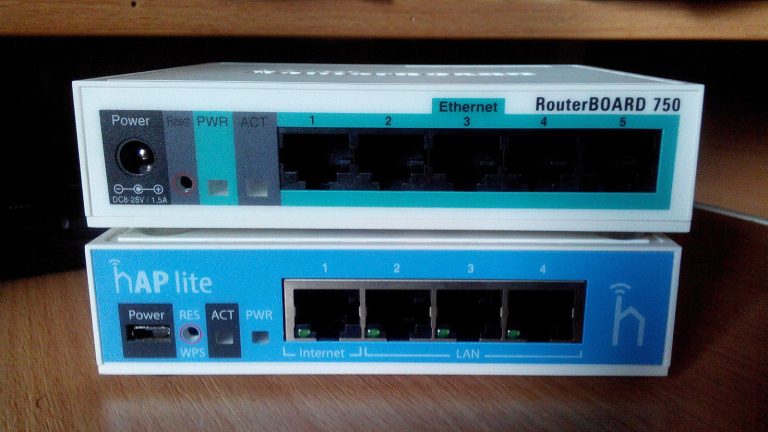
A critical MikroTik RouterOS vulnerability is actively exploited in the wild. Learn how to detect rogue ops accounts and apply the latest firmware updates.
StyleSmuggler, a Magento zero-day, gives unauthenticated remote code execution and is exploited in the wild. No patch yet. Mitigate now.