 Do Son
TL;DR
On September 22, 2026, Vercel published an emergency fix for a critical Next.js RCE vulnerability. Tracked as CVE-2026-94545, this flaw allows unauthenticated remote attackers to execute arbitrary code on Node.js runtimes. Developers should update their dependencies to Next.js version 16.3.6 immediately.
Track every CVE that hits your stack the moment it's exploited.
Get free email alertsWhy It Matters
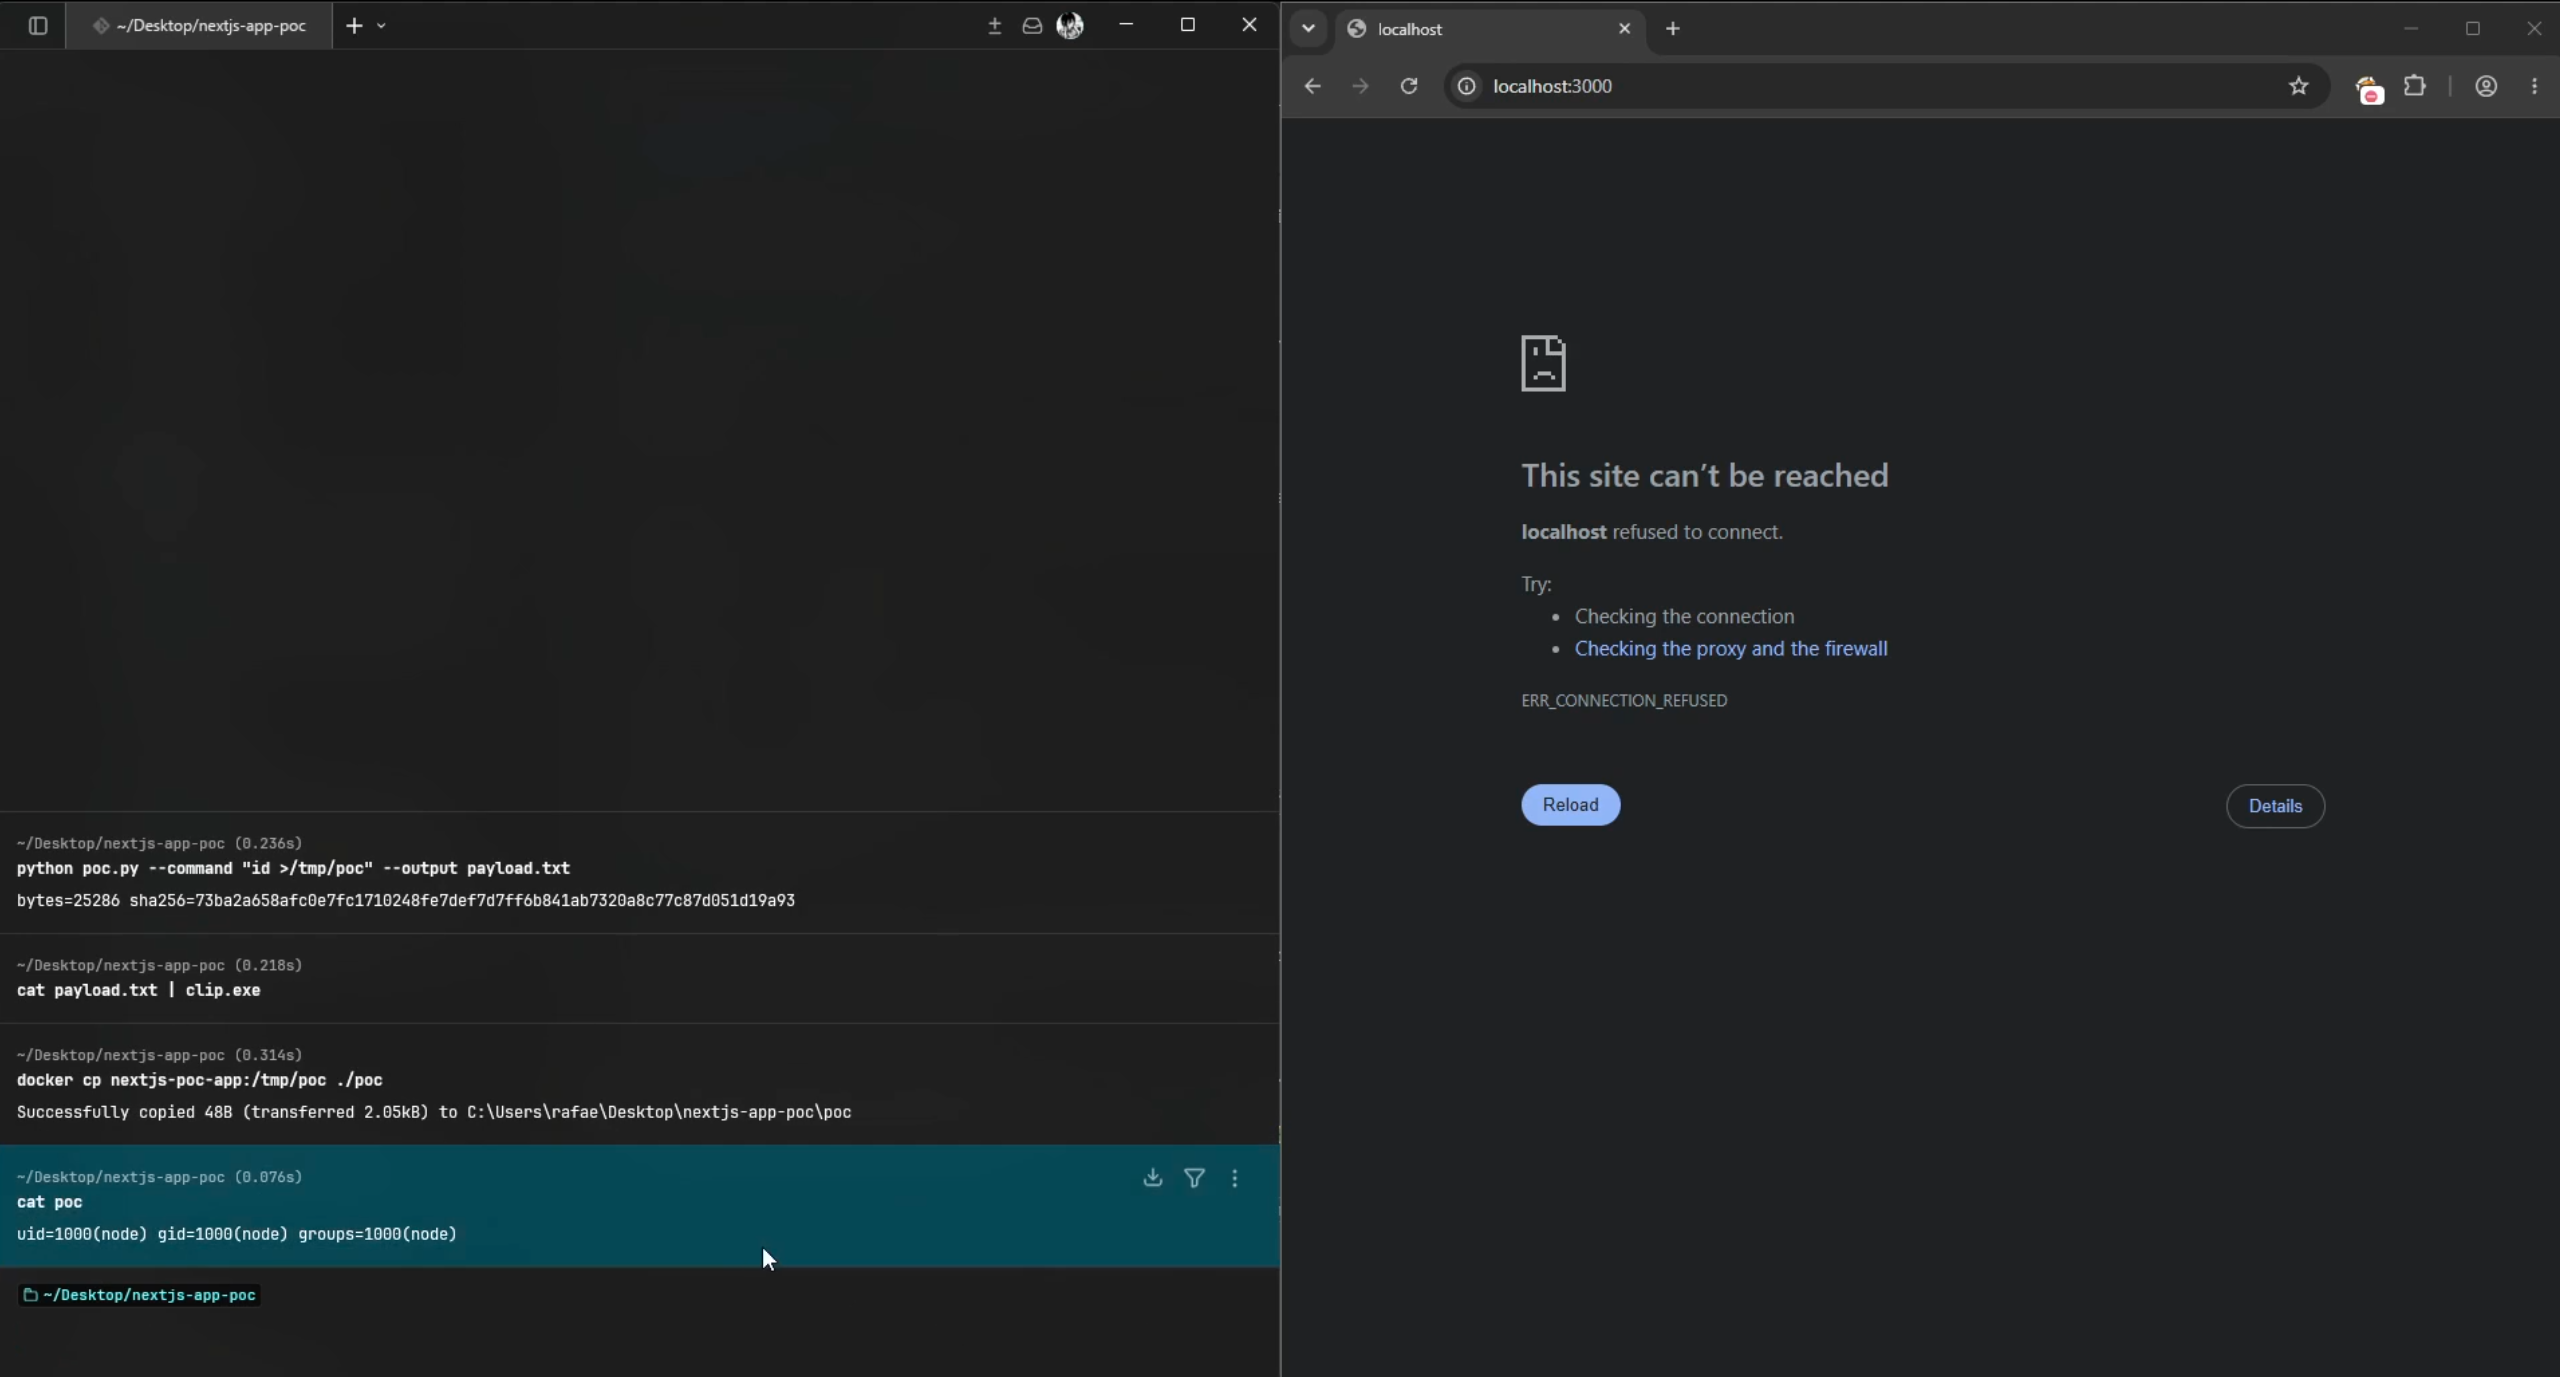
Next.js powers millions of modern web applications globally. Consequently, a severe vulnerability in its core packages threatens vast production environments. The flaw earned a critical CVSS base score of 9.5. If exploited, an attacker could compromise host servers and steal sensitive application data. Fortunately, security teams have confirmed no active exploitation in the wild. Furthermore, researchers have not released any public proof-of-concept exploit code. Nevertheless, teams must treat this critical Next.js RCE vulnerability as an urgent update priority.
How The Attack Works
The security weakness resides within upstream dependencies used for Open Graph image generation. In the official advisory, Vercel noted that “The issue affects the Node.js ImageResponse implementation in next/og.” Specifically, the vendor stated, “improper escaping in SVG output generated by Satori could lead to remote code execution.”
An attack triggers when an application renders user-supplied input into dynamic social cards. For instance, developers often pass query parameters directly into title tags within SVG graphics. Attackers provide crafted values that escape SVG boundary filtering. Then, underlying parsers process the unescaped markup, triggering code execution within the server runtime. In contrast, applications using the Edge runtime remain unaffected.
Affected Versions
This security defect affects Next.js versions 16.2.0 through 16.3.5. Branch 15.x releases do not contain the remote execution flaw. However, version 15.5.26 provides related defense-in-depth hardening.
Patch Or Mitigation Steps
Engineers should install the latest framework releases immediately. To patch your projects, review the official Next.js security update guidance. Upgrading to version 16.3.6 resolves the vulnerable dependencies. If you cannot update immediately, apply the vendor workaround. Avoid passing untrusted user parameters into SVG content or style properties rendered by the Node.js ImageResponse module.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
