 Do Son
A critical PHP security release lands November 19 and is expected to fix CVE-2026-115560, a session upload progress RCE. Conditions and mitigation.
Web Security
Patch now. Details and PoC exploit code are public for this critical CVSS 9.1 Vite Dev Server RCE flaw in exposed dev hosts.
PHP warns of CVE-2026-115560, a PHP session vulnerability that follows PHP2Shell. Disable session.upload_progress until the next bugfix release.
PHP fixes two critical PHP RCE vulnerabilities, CVE-2026-109618 and CVE-2026-109619, allowing remote code execution. Update to 8.5.12 or 8.4.27.
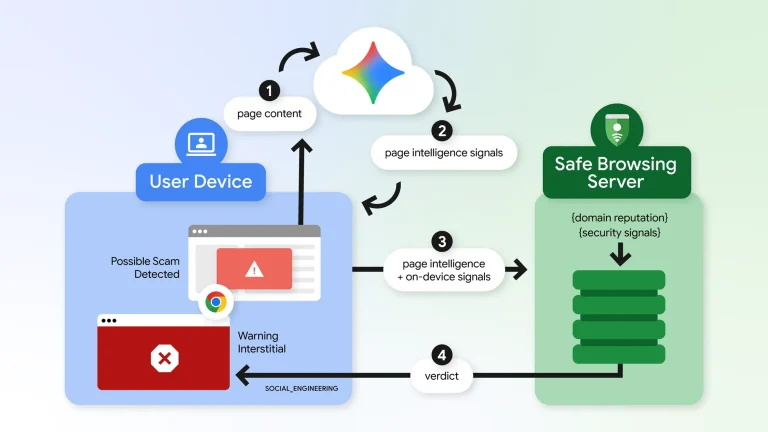
Chrome ClickFix protection in Enhanced Protection flags risky clipboard commands and uses cloud Gemini AI to block scam sites.
CVE-2026-109618 and CVE-2026-109619 are critical PHP RCE flaws rated CVSS 9.2. Cloudflare reports early attacks. See who is at risk and what to patch.
A critical Laravel authentication bypass (CVSS 9.2) in TokenGuard enables account takeover without a token. Upgrade to 13.29.0 or 12.68.0.
The Next.js security update fixes two critical unauthenticated remote code execution flaws, including CVE-2026-96889. Upgrade to 16.4.1 or 15.5.28.
A TanStack Start vulnerability, CVE-2026-102989 (CVSS 9.3), allows unauthenticated reflected XSS via crafted links. Upgrade to the patched packages.
The PHP project patched critical PHP vulnerabilities across multiple branches. Update now to resolve these PHP vulnerabilities and secure your web servers.
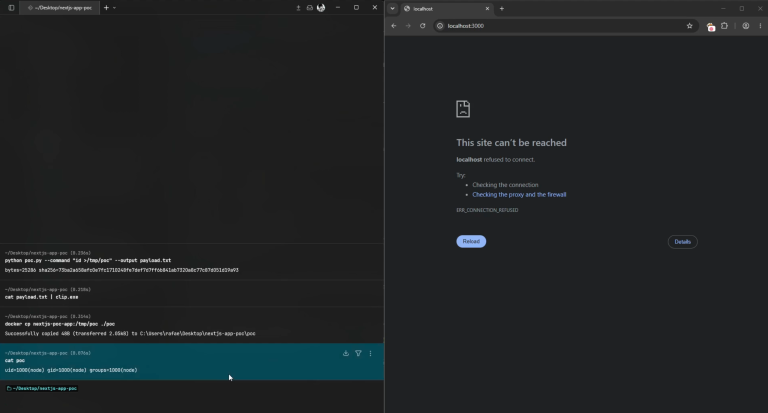
Vercel fixed a critical Next.js RCE vulnerability in image generation. Update to patch this Next.js RCE vulnerability and secure your apps.
The WordPress 7.1.1 security release fixes 11 flaws, including stored cross-site scripting and path traversal. Update your sites immediately.
Researchers discovered malicious Packagist themes iOS spyware infecting unpatched iPhones. This spyware targets crypto wallets and steals device data.
Two critical Next.js vulnerabilities, including CVE-2026-75604 (CVSS 9.0), enable unauthenticated remote code execution. Patch to 15.5.24 or 16.3.3 now.

WordPress 7.0.4 patches CVE-2026-65640, an Author-level remote code execution bug on sites using Imagick and Ghostscript. Update now.
A CodeIgniter4 RCE vulnerability, CVE-2026-63223 (CVSS 9.8), enables remote code execution via file upload. Patch to v4.7.4 to fix four flaws.
Australia's ACSC warns of a large-scale CMS exploitation campaign. Attackers exploit WordPress and CMS bugs to plant webshells on websites.

Discover why Apple restricts Siri URL summarization in iOS 27. Learn about the new security controls, prompt injection protection, and web traffic impacts.

Discover the Cloudflare PACT protocol, a privacy-first initiative with Chrome, Edge, and Firefox to eliminate CAPTCHAs and authenticate web traffic safely.

A major TinyMCE cross site scripting threat is uncovered. Patch this critical stored XSS vulnerability by updating your rich text editor now.

Concrete CMS dropped critical Concrete CMS security fixes in version 9.5.1 to eliminate remote code execution vulnerabilities. Update now.

A critical Angular hostname hijacking vulnerability allows SSRF attacks. Discover the impact on platform-server and how to patch your apps.