 Do Son
Urgent: PrestaShop patches a 9.3 severity XSS flaw (CVE-2026-44212) that allows unauthenticated attackers to hijack your store's back office. Update now!
Web Security
Critical Alert: CVE-2026-44211 (CVSS 9.6) in Cline AI allows malicious sites to hijack your terminal and steal data via WebSockets. Update your CLI tools now.
PHP releases urgent security patches for a 9.5 severity RCE in the SOAP extension and a PHP-FPM XSS flaw. Update to 8.2.31, 8.3.31, 8.4.21, or 8.5.6 now!
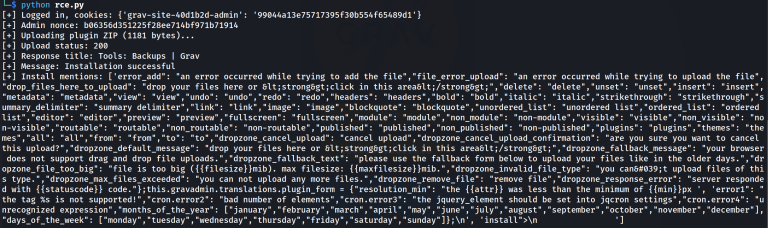
Protect your Grav CMS deployments. Attackers are chaining CVE-2026-42613 and CVE-2026-42607 to achieve unauthenticated remote code execution. Patch today!

May 13 Deadline: Let’s Encrypt launches 45-day certs, freezes mTLS, and moves to Gen Y intermediates. Is your automation ready for the triple-threat update?

Protect your app from CVE-2026-23870. Learn how this high-severity React Server Components DoS flaw crashes servers and how to patch your React 19 build today.

Apache releases v2.4.67 to fix an HTTP/2 Double Free RCE (CVE-2026-23918) and auth bypasses. Millions of servers are affected—upgrade your infrastructure now!
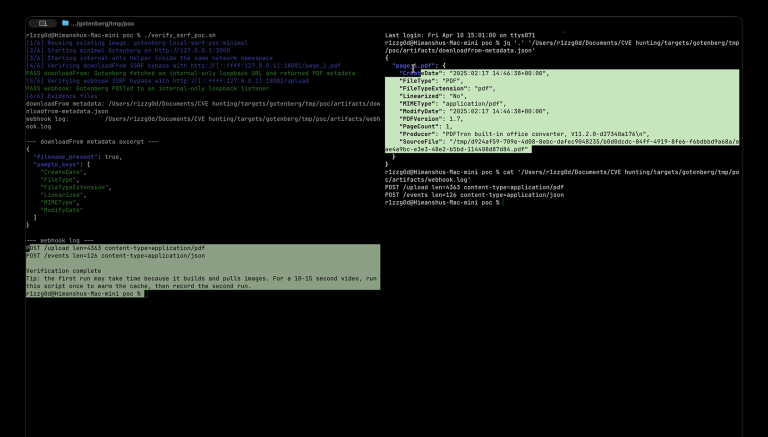
Gotenberg PDF API hit with a rare CVSS 10 flaw. Unauthenticated RCE, file overwrites, and SSRF bypasses discovered. Upgrade to version 8.32 immediately.

A critical 9.1 CVSS flaw in a Go auth library causes a Patreon "identity collision," merging all users into one account. Upgrade to v2.1.2 immediately!
libmodsecurity3 faces critical 8.2 & 7.5 CVSS flaws. A simple one-line script can crash WAF worker processes. Protect your server by upgrading to v3.0.15 now.
Unauthenticated attackers can hijack mailcow admin sessions via a critical CVSS 9.3 Stored XSS in Autodiscover logs. Patch to version 2026-03b immediately.
A critical 9.1 CVSS flaw in Budibase lets attackers bypass auth via unanchored regex. Protect your user database—update to version 3.35.4 immediately.

Angular patches a critical 8.7 SSRF flaw in @angular/platform-server. Attackers can hijack SSR origins via URL normalization. Patch v19, v20, or v21 now!
Krayin CRM faces a critical CVSS 10 RCE flaw in its TinyMCE upload endpoint. Authenticated users can seize server control. Patch version 2.2.x immediately!
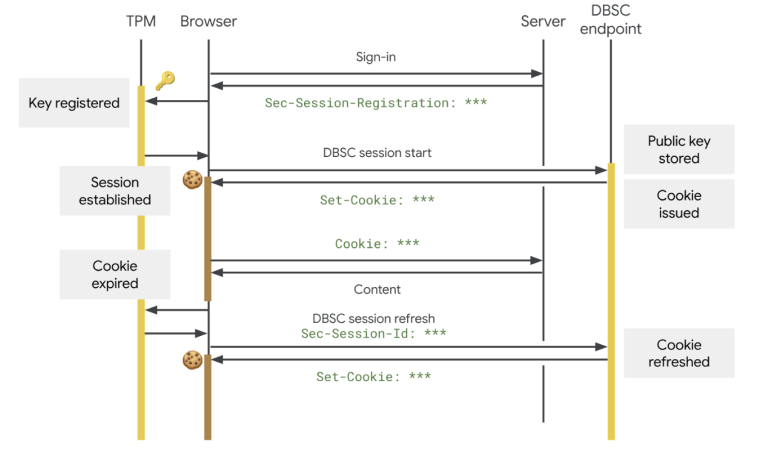
Google launches DBSC in Chrome 146, binding session cookies to hardware like TPM. Neutralize infostealers and stop session hijacking with this new standard.
Vite patches critical flaws (CVE-2026-39364 & CVE-2026-39363) allowing arbitrary file reads and .env leaks via WebSockets and query params. Upgrade to 8.0.5!

Cisco Talos uncovers UAT-10608, an automated campaign using "NEXUS Listener" to harvest Next.js credentials via React2Shell. Patch your cloud tokens now!

CVE-2026-34950: A critical 9.1 CVSS flaw in fast-jwt allows authentication bypass via leading whitespace. Learn how a regex error leads to algorithm confusion.
Payload CMS fixes a critical 9.1 CVSS flaw (CVE-2026-34751) in its password reset flow. Attackers could hijack accounts. Update to v3.79.1 immediately!
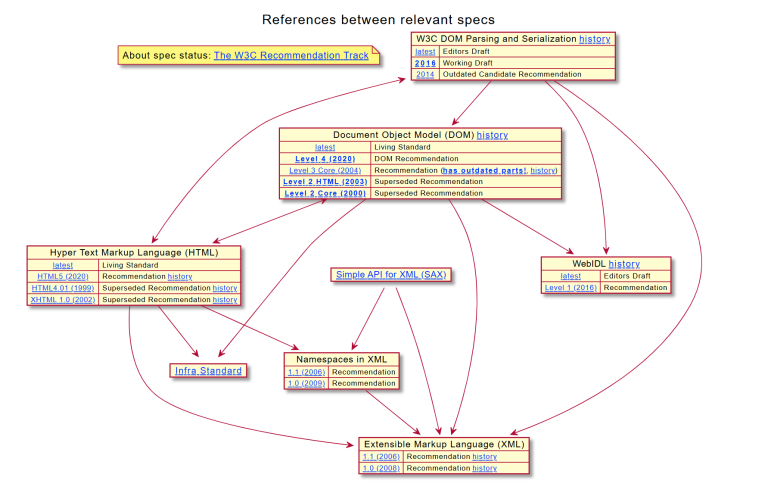
Fix CVE-2026-34601 in @xmldom/xmldom (CVSS 7.5). A CDATA injection flaw allows attackers to bypass "safe zones" and manipulate business logic. Update now!
Node-convict (CVE-2026-33864) faces a 9.4 CVSS Prototype Pollution flaw. Bypass filters and hijack Node.js apps. Update to version 6.2.5 now to stay secure.
Scriban’s 9.1 CVSS flaw allows sandbox escapes in .NET apps via a cache bypass. Over 40M downloads affected. Update to version 7.0.0 to secure your templates.