 Do Son
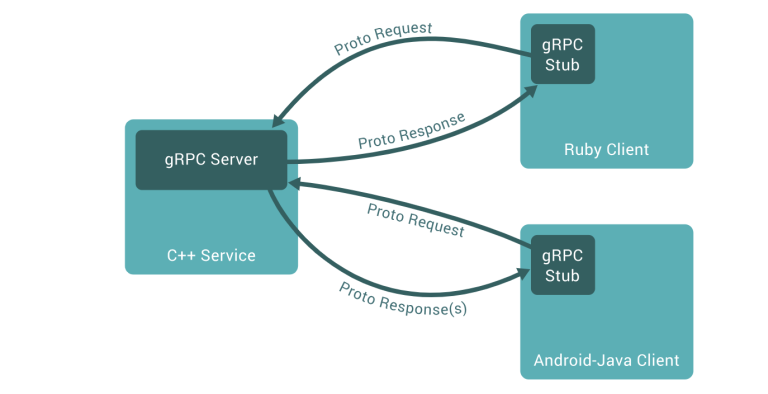
A critical 9.1 CVSS flaw in gRPC-Go (CVE-2026-33186) allows attackers to bypass authorization by omitting a leading slash. Upgrade to v1.79.3 immediately.
Web Security

Craft CMS patches CVE-2026-32267, a critical 7.7 CVSS flaw where a simple Live Preview token grants low-privilege users full admin access. Update today.

Django releases security updates (6.0.3, 5.2.12, 4.2.29) to fix a Windows DoS flaw (CVE-2026-25673) and file permission risks. Upgrade your framework now.
Qwik framework patches a critical 9.2 CVSS RCE vulnerability (CVE-2026-27971) where unsafe deserialization in server$ RPC allows total server takeover.

Angular patches a critical 9.2 CVSS SSRF vulnerability (CVE-2026-27739). Attackers can manipulate Host headers to steal credentials and probe internal networks.

Mozilla Firefox 148 launches the standardized Sanitizer API. Discover how the new setHTML() method systematically strips XSS attacks to protect web users.
CleanTalk flaw CVE-2026-1490 (CVSS 9.8) exposes 200k sites to RCE via DNS spoofing. Attackers bypass auth to install plugins. Update to v6.72 now.

Critical EverShop flaw CVE-2026-25993 (CVSS 9.3) allows Second-Order SQL Injection via URL keys. Update to v2.1.1 to prevent store takeover.

Critical Fiber framework vulnerability CVE-2025-66630 (CVSS 9.2) causes silent UUID failures, leading to session hijacking. Update to v2.52.11 now.

Critical SandboxJS flaw CVE-2026-25881 allows sandbox escape via prototype pollution. Malicious code can modify host logic & execute RCE. Update to v0.8.31.
Critical SandboxJS flaws (CVSS 10.0) allow sandbox escape & host takeover via prototype pollution. Update to v0.8.29 immediately to stop code execution.

Critical jsPDF flaws (CVE-2026-24133) allow XSS & DoS via malicious BMPs. Update to v4.1.0 immediately to prevent browser crashes and code injection.
Django patches 3 critical SQL injection flaws & DoS risks in versions 6.0.2, 5.2.11, & 4.2.28. Update immediately to secure your database.

Critical React flaw CVE-2025-55182 (CVSS 10.0) under mass exploitation. Two IPs drive 56% of attacks deploying miners & shells. Upgrade to v19.0.1+ now.

Critical backdoor CVE-2026-0920 in LA-Studio Element Kit is being exploited in the wild. Former employee planted the code. Update to v1.6.0 immediately.
High-severity ImageMagick flaw CVE-2026-23876 allows heap buffer overflows via XBM images. Update to v7.1.2-13 to prevent remote attacks.

Critical ACF Extended flaw CVE-2025-14533 (CVSS 9.8) lets attackers seize admin control. 100k sites at risk. Update to version 0.9.2.2 immediately.
ConnectWise patches critical Stored XSS (CVE-2026-0695) in PSA Time Entry notes. Vulnerability allows session hijacking. Update to version 2026.1 immediately.

Unpatched Livewire Filemanager flaw (CVE-2025-14894) allows unauthenticated RCE via malicious uploads. Check storage:link configurations immediately.

Urgent: Modular DS flaw CVE-2026-23550 (CVSS 10) is actively exploited in the wild. Attackers are creating fake admins. Update to the latest version now.

Urgent: Node.js patches CVE-2025-55131 (High Severity). "Dirty" memory flaw exposes secrets. Update to v20.20.0/v22.22.0 now to stop data leaks.