
 Do Son
Chrome 144 fixes 10 vulnerabilities, including high-severity V8 flaw CVE-2026-0899. Update Windows, Mac & Linux immediately to secure your browser.
Web Security

Angular CVE-2026-22610 (CVSS 8.5) allows XSS via SVG script attributes. Update to v21.0.7 or v20.3.16 immediately to secure your apps.

Urgent Patch: React Router CVE-2025-61686 (CVSS 9.1) exposes server files via session flaws. Fix XSS & Open Redirect bugs by updating to v7.9.6 now.

Synacktiv unmasks CVE-2025-54068, a critical Livewire hydration flaw, and Livepyre, a tool that achieves RCE even if the APP_KEY is known.

A normalization flaw in Better Auth's router allows attackers to bypass access controls and rate limits using simple double-slash URLs.

Following Apple's push, Let's Encrypt will cap all certificate validity at 45 days by 2028. Users must ensure automation is compatible with the significantly shorter lifetime.

CVE-2025-66035: Angular protocol-relative URLs leak XSRF tokens, bypassing CSRF protection. Update to v19.2.16, v20.3.14, or v21.0.1 now.

A Critical (CVSS 9.8) RCE flaw in Sneeit Framework is actively exploited. The bug allows unauthenticated attackers to run arbitrary code via call_user_func and take over WordPress sites. Update to v8.4 immediately.

Symfony patched a High-severity flaw (CVE-2025-64500) in its Request component. Improper PATH_INFO parsing allows attackers to bypass access control rules in vulnerable applications.

Google announced Chrome 154 (Oct 2026) will automatically enable “Always Use Secure Connections,” marking a major security push to combat MitM attacks by warning users before visiting unencrypted HTTP sites.

LiteSpeed Cache for WordPress (LSCWP) versions 7.5.0.1 are vulnerable to a Reflected XSS flaw, exposing 7M sites to account takeover. Update to 7.6 now.

A Critical flaw (CVE-2025-11230) in HAProxy’s mjson number parser allows unauthenticated attackers to cause a Denial of Service with a single crafted JSON payload. Update immediately.

Rack patches CVE-2025-59830 (CVSS 7.5), a flaw where attackers could use semicolon separators to bypass the parameter count limit and trigger DoS attacks.

Two WordPress Core vulnerabilities (XSS and Info Exposure) affecting versions up to 6.8.2 were accidentally exposed before patches were ready.

Security researcher Puja Srivastava from Sucuri uncovered two malicious files designed to guarantee persistent attacker access by...

Adobe has released an emergency patch for a critical Magento flaw, SessionReaper (CVE-2025-54236). The bug could allow automated attacks against thousands of online stores.

A high-severity flaw (CVE-2025-58179) in Astro's Cloudflare adapter allows attackers to bypass domain restrictions, leading to SSRF and XSS attacks.

A new report reveals a critical SSRF vulnerability in the PhpSpreadsheet library. The flaw could allow attackers to access internal networks and sensitive data.

Citing competition and rising costs, the popular Certificate Authority Buypass has announced it will stop issuing TLS/SSL certificates in October 2025.

A critical zero-day vulnerability (CVE-2025-5419) in Chrome's V8 engine is being actively exploited. Users must update their browser immediately to prevent attacks.
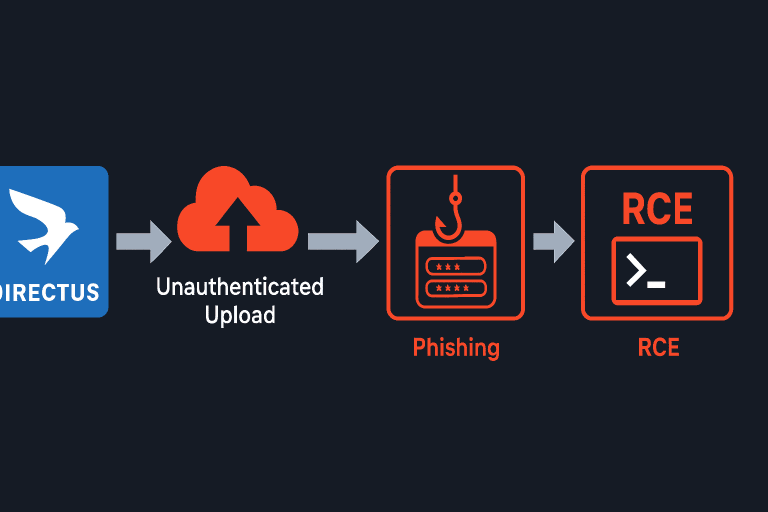
A critical vulnerability in the Directus API (CVE-2025-55746) allows unauthenticated attackers to silently upload and modify files, leading to webshells and RCE.

A critical flaw in the widely used sha.js library (CVE-2025-9288) can lead to hash collisions and private key extraction, threatening web applications.