 Do Son
Jenkins patched 20 plugin vulnerabilities, including 7 Script Security sandbox bypasses that allow remote code execution on the controller. Update now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
An exploited Cisco ISE vulnerability (CVE-2026-76460) allows remote root access. Patch this critical Cisco ISE vulnerability to secure networks.
Check Point fixed a critical Check Point login flaw (CVE-2026-91843). Patch this Check Point login flaw now to block unauthenticated remote root takeovers.
Patch critical industrial firmware vulnerabilities and authentication bypass flaws like CVE-2026-27565 in Pepperl+Fuchs, Phoenix Contact & Carlo Gavazzi.
An Issabel PBX vulnerability exploited in active attacks allows remote code execution. Patch this Issabel PBX vulnerability to secure systems.
Octopus Deploy addressed critical Octopus Server vulnerabilities involving a CVSS 8.7 remote code execution. Apply the security patches to prevent attacks.
A Google Pixel vulnerability exploited in targeted attacks allows privilege escalation. Update your device to patch this Google Pixel vulnerability now.
Apache resolved critical Apache ZooKeeper vulnerabilities. Patch Apache ZooKeeper vulnerabilities to block unauthorized znode deletion and audit spoofing.
Discover the latest mySCADA myPRO Manager vulnerabilities, including CVE-2026-73807, and learn how to patch your systems to prevent remote attacks.
A critical HPE EdgeConnect authorization bypass (CVE-2026-76670) enables full system compromise. Patch this HPE EdgeConnect authorization bypass now.
Six Apache Syncope vulnerabilities, including CVE-2026-82232, expose severe identity management flaws. Patch your Apache Syncope servers immediately.
A new Google Chrome security update patches 42 Chrome Stable channel vulnerabilities. Install version 153 immediately to protect against remote attacks.
A critical proxy-addr IP spoofing flaw (CVE-2026-90711) exposes Node.js apps to access control bypasses. Patch this proxy-addr IP spoofing bug today.
A critical Langflow SSRF flaw (CVE-2026-12944) exposes cloud credentials and internal networks. Patch your Langflow OSS servers immediately.
Multiple critical Squid proxy vulnerabilities, including CVE-2026-61642, allow request smuggling and buffer overflows. Patch your servers immediately.
WHMCS released patches for critical WHMCS vulnerabilities. Update your billing portal now to prevent data theft and remote code execution attacks.
Cisco patched critical Cisco Secure Email vulnerabilities. Update to fix Cisco Secure Email vulnerabilities and prevent unauthorized system access.
CVE-2026-76461 (CVSS 9.8) is a Cisco Secure Email Gateway vulnerability exploited in the wild. SQL injection grants root command execution. Patch now.
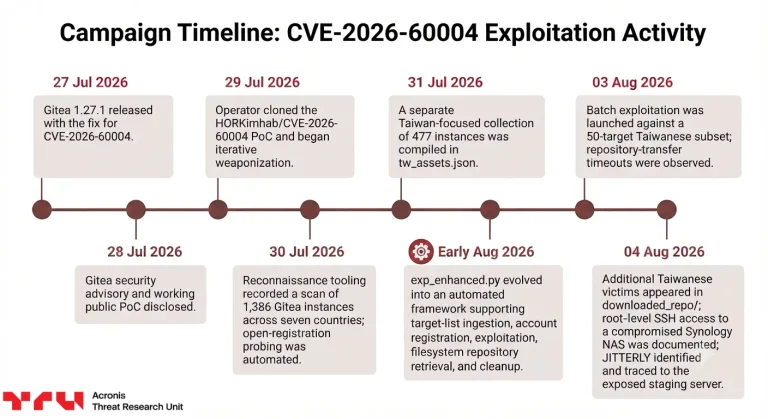
A critical Gitea RCE vulnerability exploited in wild attacks exposes servers. Patch this Gitea RCE vulnerability now to prevent full system compromise.
A critical The Events Calendar vulnerability is exploited in the wild. Patch The Events Calendar vulnerability now to stop remote code execution.
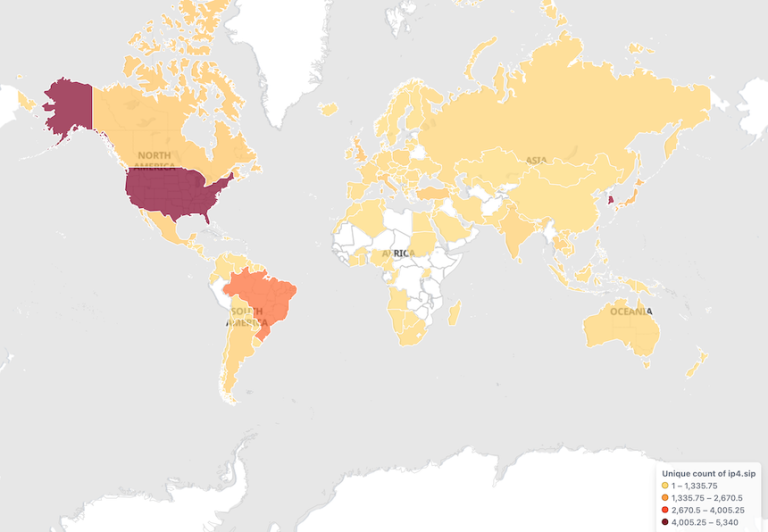
CVE-2026-87827 (CVSS 10) is a KGUARD DVR vulnerability exploited by the Mirai botnet for unauthenticated RCE and complete device compromise.
The Vite development server vulnerability CVE-2026-39364 is exploited in mass scanning for credential harvesting. F5 Labs logged 32,000 events. Patch now.