 Do Son
TL;DR CVE-2026-19598 is a CVSS 9.8 privilege escalation flaw in the Pods WordPress plugin. It lets unauthenticated...
Vulnerability Report
TL;DR Apache CloudStack shipped releases 4.20.3.1 and 4.22.1.1. They fix 20 CVEs across the platform. The most...
TL;DR IBM patched a large batch of IBM AIX vulnerabilities on August 15, 2026. Many allow remote...
TL;DR A uutils coreutils vulnerability affects the stdbuf tool in the Rust rewrite of GNU coreutils. By...
TL;DR CERT/CC disclosed five RDK-B WebUI vulnerabilities on August 19, 2026. The worst flaw lets a remote,...
TL;DR Keycloak 26.7.2 fixes five flaws, released on August 19, 2026. The most severe, CVE-2026-18963, allows a...
TL;DR Red Hat disclosed three high-severity flaws that enable privilege escalation. The worst, CVE-2026-67567 (CVSS 9.9), hits...
TL;DR CVE-2026-32475 is a CVSS 9.8 unauthenticated arbitrary file upload flaw in Elementor Pro. It affects an...
TL;DR CVE-2026-77647 is a CVSS 9.8 unauthenticated remote code execution flaw in the SPIP CMS. It affects...
TL;DR TP-Link patched three Omada gateway vulnerabilities. The most severe, CVE-2026-19586, is a pre-authentication OS command injection...
Update: Microsoft updated its safety alert on August 21, 2026. Initially, the report marked the bug as...
TL;DR VMware disclosed four Spring Security vulnerabilities. The most severe, CVE-2026-59270, rates CVSS 9.4 (CRITICAL). Its embedded...
TL;DR CVE-2026-77176 is a CVSS 8.1 flaw in Kata Containers genpolicy. A malicious operator can mount arbitrary...
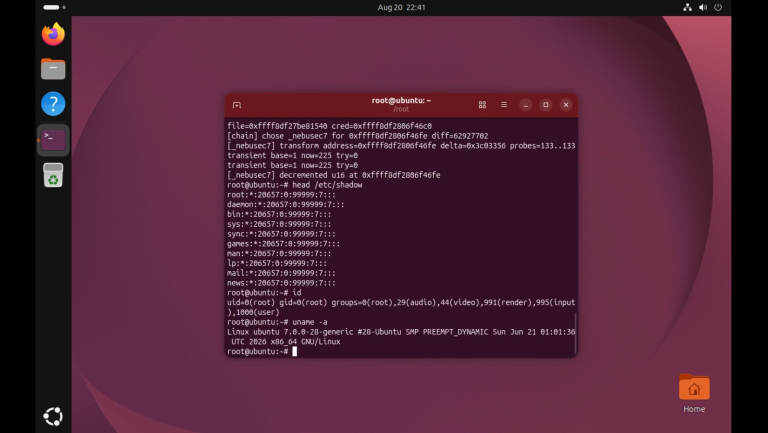
TL;DR A researcher published proof-of-concept exploit code for CVE-2026-52929, a Linux kernel SCTP flaw rated CVSS 7.5....
TL;DR VMware disclosed seven Spring GraphQL vulnerabilities and related Spring Cloud flaws on August 20, 2026. All...
TL;DR CISA added two TrueConf Server flaws to its Known Exploited Vulnerabilities catalog. Tracked as CVE-2026-72529 and...
TL;DR Google shipped a Chrome Stable channel update with seven security fixes. The most severe, CVE-2026-76017, is...
Two high-severity Spring Integration vulnerabilities threaten application security. Specifically, CVE-2026-59307 allows remote code execution via a deserialization...
TL;DR Frauscher patched eight flaws in its FDS102 railway diagnostic system on August 20, 2026. The most...
TL;DR Apache InLong patched three flaws in version 2.4.0. The most notable is an Apache InLong SQL...
TL;DR Dell patched three flaws in its PowerStore T storage family. The most severe, CVE-2026-67271, scores a...
TL;DR The maintainers of vm2 patched three critical flaws on August 17, 2026. The most severe, CVE-2026-47686,...