
 Do Son
NVIDIA patches a critical 9.0 CVSS vulnerability (CVE-2025-33244) in the Apex library. Protect your AI models from RCE—upgrade to PyTorch 2.6+ now.
Linux Security

Qualys discovers CVE-2026-3888, a critical Local Privilege Escalation (LPE) flaw in Ubuntu Desktop. Learn how a 30-day time window exposes root access.

A critical Sudo vulnerability in the exec_mailer function allows local attackers to bypass security restrictions and escalate privileges to root access.

CrackArmor exposes 12.6M Linux servers to root escalation. Qualys TRU discovers 9 AppArmor flaws letting users bypass security and escape containers.

A pre-auth flaw in OpenSSH's GSSAPI Key Exchange (CVE-2026-3497) exposes Ubuntu and Debian servers to heap corruption and data leaks. Patch now.
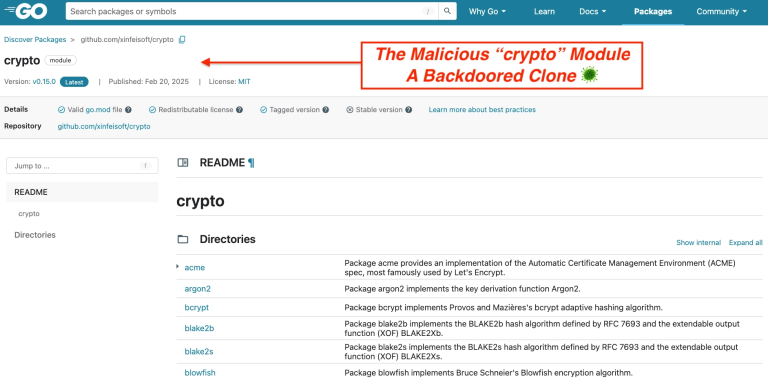
Socket uncovers a malicious Go module mimicking golang.org/x/crypto. It steals passwords via ReadPassword and deploys the Rekoobe backdoor on Linux systems.

Researcher Justin Swartz uncovers a regression of the 1999 telnetd flaw. Remote attackers can bypass authentication and seize root control via environment variables.
Critical Odoo on NixOS flaw (CVE-2026-25137) leaves databases exposed due to configuration immutability. Restarts wipe the master password.

NVIDIA patches high-severity flaws (CVE-2025-33217) in GPU drivers & vGPU software. Flaws allow code execution. Update Windows/Linux drivers now.
NVIDIA patches 4 high-severity flaws in CUDA Toolkit (up to v13.1). Vulnerabilities in Nsight Systems allow code execution & privilege escalation. Update now.

Attackers are hijacking Linux Snap Store apps by registering expired developer domains. Malicious updates target crypto wallets. Secure your accounts now.

NVIDIA fixes high-severity code injection flaws in Nsight Graphics and Merlin (CVE-2025-33206/33). Update to v2025.5 immediately to prevent compromise.

Critical GNU Inetutils telnetd flaw allows unauthenticated root access via "-f root". Affects v1.9.3-2.7. Disable telnet immediately to stay safe.

libheif flaw CVE-2025-65586 causes app crashes via malformed HEIF images. Update to v1.21.0 now to prevent Denial of Service attacks.

CVE-2025-13151: A one-byte overflow in GNU libtasn1 risks memory corruption during cert parsing. Patch now to secure your cryptographic applications.
High-severity ImageMagick flaw CVE-2026-23876 allows heap buffer overflows via XBM images. Update to v7.1.2-13 to prevent remote attacks.

glibc patches CVE-2026-0861 (CVSS 8.4) & CVE-2026-0915. High-severity heap corruption and a 20-year-old leak affect Linux systems. Patch now.

NVIDIA patches high-severity command injection in Nsight Graphics for Linux (CVE-2025-33206). Update to v2025.5 to prevent code execution.
HPE warns: Details of Aruba VIA root flaw (CVE-2025-37186) are public. Linux users exposed to LPE. No patch yet—apply the workaround now.

Critical Foomuuri flaws (CVE-2025-67603) allow local users to hijack firewall settings. SUSE urges immediate update to v0.31 to secure your system.

New GoBruteforcer variant targets 50k+ servers by exploiting weak passwords from AI-generated code. Learn how this crypto-stealing botnet operates.
CVE-2025-67859: TLP 1.9.0 flaw lets users bypass root auth. SUSE researchers urge Linux users to update to version 1.9.1 to fix this critical security gap.