
 Do Son
GnuTLS v3.8.13 fixes critical heap overwrites, identity truncation, and OCSP bypasses. Secure your Linux comms and upgrade to the latest version now.
Linux Security

libmodsecurity3 faces critical 8.2 & 7.5 CVSS flaws. A simple one-line script can crash WAF worker processes. Protect your server by upgrading to v3.0.15 now.

Linux "Copy Fail" (CVE-2026-31431) technical details and PoC are now public. Learn how a 732-byte script grants root access by corrupting the page cache.

glibc warns of critical flaws (CVE-2026-5435 & CVE-2026-6238) in deprecated DNS functions. Patch legacy apps to avoid buffer overflows and memory leaks.
Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection
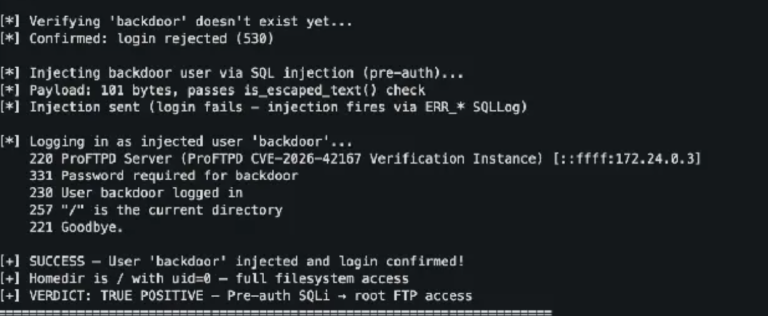
Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection
Critical SQLi in ProFTPD's mod_sql allows unauthenticated admin account injection. Full PoC code is public. Upgrade to v1.3.9a to secure your servers.

The critical "Pack2TheRoot" flaw (CVE-2026-41651) in PackageKit gives root access on Linux. It went undetected for 12 years. Update to version 1.3.5 now!
Microsoft's OOB update for .NET 10 (CVE-2026-40372) hits Linux/macOS users. Authentication is at risk. Stop the bypass and rotate your keys today.
glibc version 2.43 and older face heap overflows and memory leaks. Learn about CVE-2026-5358, CVE-2026-5450, and CVE-2026-5928. Update your Linux systems now.

Use-after-free flaw in Rsync versions 3.0.1–3.4.1 allows DoS and info leaks via malicious xattr traffic. Learn how a simple qsort fix secures your syncs.
Cockpit CVE-2026-4631 allows unauthenticated RCE on Linux servers via SSH injection. Stop the unauthorized takeover—upgrade to Cockpit version 360 now!
Nix patches a critical 9.0 CVSS sandbox escape. Learn how CVE-2026-39860 allows unprivileged users to seize root control via symlink manipulation. Update now!

Checkmk patches a critical 9.3 CVSS local privilege escalation flaw in the 'omd' command. Stop site users from seizing root access—update your sites today!

Critical 9.3 CVSS flaw (CVE-2026-34078) in Flatpak allows apps to escape sandboxes and access all host files. Secure your Linux system—update to v1.16.4 now!

GPUBreach: A new GPU Rowhammer attack from UofT that bypasses IOMMU and ECC to achieve full system root on NVIDIA systems. GitHub code arrives April 13.

Fenrisk releases full PoC exploit for CVE-2025-48703, a critical CWP RCE flaw. Learn how unauthenticated attackers hijack non-root users. Patch now!

Critical 8.8 CVSS flaw in libinput allows sandbox escape via malicious Lua plugins. Affects GNOME, KDE, and Fedora. Update to 1.31.1 or 1.30.3 now!
Artifex MuPDF faces a 7.8 CVSS integer overflow (CVE-2026-3308) allowing RCE via "crafted" PDFs. With no official patch, sandboxing is vital. Update now.

OpenSSH 10.3 fixes critical gaps, including client-side command execution and scp privilege escalation flaws. Update your remote access stacks immediately.

NVIDIA fixes high-severity vulnerabilities (CVSS 8.3) in Jetson Linux for Xavier, Orin, and Thor. Protect your autonomous systems—update to 36.5 or 35.6.4.
NVIDIA fixes high-severity flaws (CVE-2026-24164) in BioNeMo. Attackers could execute code or disrupt AI drug discovery. Update to commit e5e58c8 now.
Vim patches a critical 8.2 CVSS bug chain in modelines and tabpanels. Opening a malicious file triggers instant RCE. Update to 9.2.0272 now to stay safe.
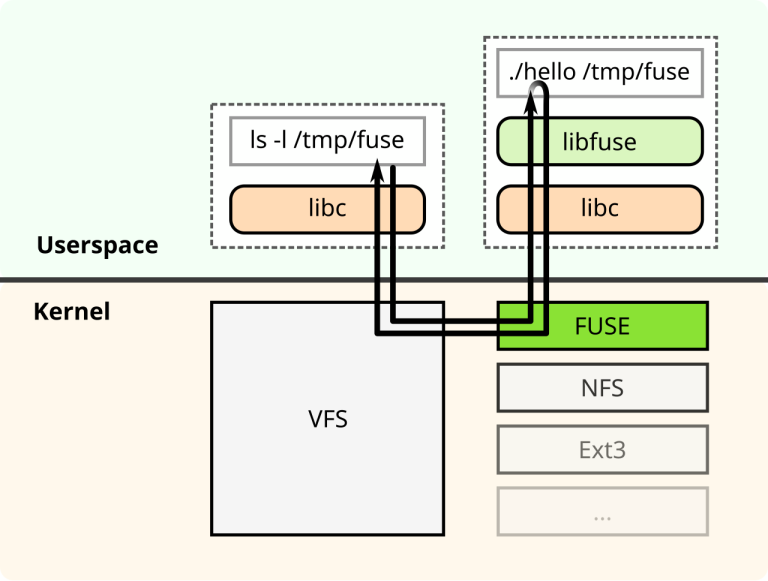
Researchers uncover two flaws in libfuse's io_uring transport (CVE-2026-33150 & 33179). Impacting Kubernetes CSI drivers, these bugs allow RCE and DoS. Patch now!