 Do Son
A critical TYPO3 Powermail RCE flaw (CVE-2026-77136) is actively exploited in the wild. Update immediately to prevent server compromise and data leaks.
rce
Metal Gear Online 3 RCE vulnerability CVE-2026-19874 fixed. Update the game to prevent attackers from executing remote code on your system.

A critical IBM remote code execution flaw (CVE-2026-17482, CVSS 9.8) allows attackers to compromise workstations. Discover how to apply the software patch.

PoC exploit code is public for a MariaDB remote code execution chain. A low-privilege account can run commands as mariadbd. Details inside.

IBM critical vulnerabilities hit App Connect, Power HMC, and webMethods. CVE-2026-12943 lets attackers execute arbitrary commands at CVSS 9.8.

A high-severity Django vulnerability, CVE-2026-15307, can enable remote code execution through spatial lookups. Update to Django 6.0.8 or 5.2.17 now.

A critical Veeam ONE vulnerability, CVE-2026-64633, allows remote unauthenticated code execution at CVSS 10.0. Update to build 13.1.0.7034 now.

A critical Gitea vulnerability, CVE-2026-59774, lets unauthenticated attackers read server files and reach remote code execution. Update to 1.27.1 now.
Adobe Campaign Classic flaw CVE-2026-48449 scores a perfect CVSS 10.0 and allows arbitrary code execution. Update to build 9398 now.
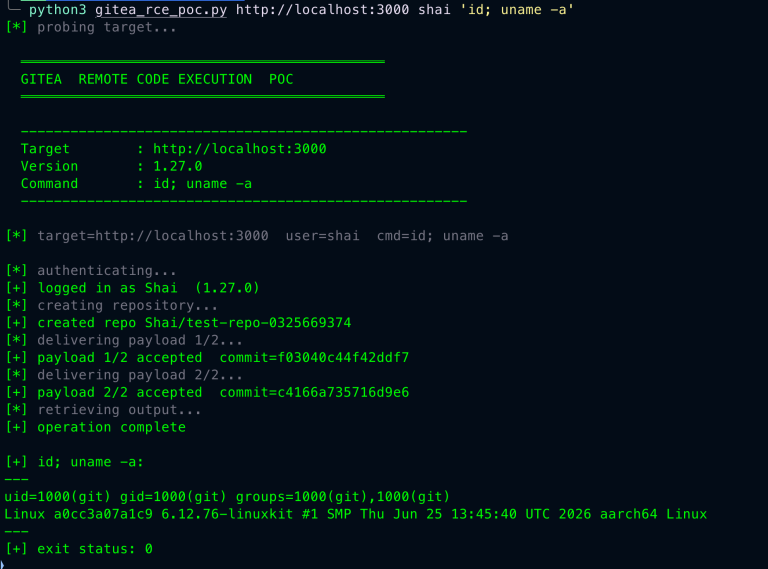
CVE-2026-60004 is a critical Gitea RCE via a diffpatch Git hook, rated CVSS 9.8. Full details and a public PoC are out. Update to Gitea 1.27.1 now.
CVE-2026-63077 is a critical TeamCity RCE rated CVSS 9.8. Unauthenticated attackers can run OS commands. Update TeamCity On-Premises to a fixed build.

SolarWinds patched 15 critical Serv-U vulnerabilities enabling privilege escalation, account takeover, and RCE as root. Update to Serv-U 2026.3 now.

CISA added four flaws to its KEV catalog, including WordPress RCE (CVE-2026-63030) and Langflow RCE (CVE-2026-0770). All are exploited in the wild.
Metabase patched CVE-2026-59827 (CVSS 9.9) and CVE-2026-59826 (CVSS 9.1). These flaws enable remote code execution via unsafe H2 deserialization.
Dell patched CVE-2026-56688, a PowerFlex command execution bug. This OS command injection flaw lets a privileged attacker run code as root.
A critical Veeam Backup vulnerability (CVE-2026-44963) allows remote code execution. Patch immediately to avoid ransomware targeting CVE-2023-27532.
A critical Feast Feature Server flaw (CVE-2026-23537) lets unauthenticated attackers perform arbitrary file write and risk remote code execution. Act now.
A Network UPS Tools RCE (CVE-2026-54161) lets a malicious upsd trigger upsmon command injection as root. No patch exists yet, so mitigate now.

Discover the new Cursor IDE RCE vulnerability called DuneSlide. This critical sandbox escape flaw assigned CVE-2026-50548 threatens developer environments.

A critical IBM Db2 RCE flaw (CVE-2026-10109) allows pre-auth code execution. IBM patched it plus two other Db2 bugs. Update 11.5 and 12.1 now.

A critical OpenAM WebAuthn RCE flaw (CVE-2026-45051) allows code execution via Java deserialization. Update OpenAM to 16.1.1 to stay protected.

Four Fluentd vulnerabilities are fixed in v1.19.3, including a 9.8 RCE (CVE-2026-44024) and SSRF (CVE-2026-44161). Patch now.