 Do Son
A disclosed OnePlus session takeover vulnerability threatens OnePlus 13R Android security, allowing malicious apps to steal tokens and modify user data.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
NVIDIA fixed critical Triton Inference Server vulnerabilities. Patch your Triton Inference Server vulnerabilities now to stop denial of service attacks.
Critical Apache Artemis vulnerabilities, including CVE-2026-67593 and other ActiveMQ Artemis flaws, expose systems to denial of service and data exposure.
Arista released fixes for critical Arista EOS vulnerabilities. Learn how these Arista EOS vulnerabilities impact enterprise switches and edge devices.
A critical Secure Boot bypass vulnerability via a UEFI Shell flaw exposes servers to code execution. Discover how CVE-2026-33197 impacts devices.
MongoDB fixed 24 MongoDB Server vulnerabilities, including a critical auth bypass (CVE-2026-82067) and unauthenticated denial of service flaws. Patch now.
Okta fixed critical Okta vulnerabilities across multiple tools. Patch these Okta vulnerabilities today to prevent code execution and authorization bypass.
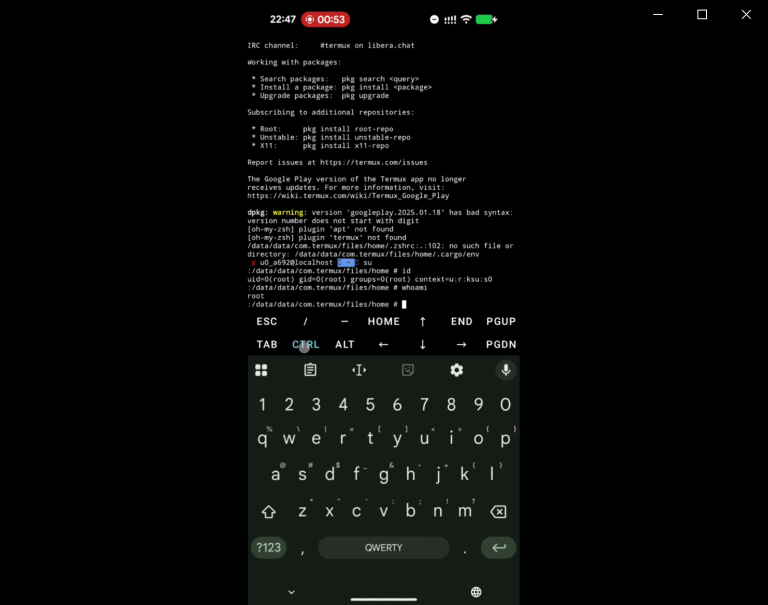
The LSPromise exploit chain provides a 100% success rate for local privilege escalation to root on Android 17. Details and PoC are publicly disclosed.
A new PAN-OS buffer overflow flaw, tracked as CVE-2026-0310, exposes firewalls to remote code execution. Patch your network devices immediately.
Cisco Talos warns of Cisco FMC vulnerabilities actively exploited in the wild. Attackers chain CVE-2026-20079 and CVE-2026-20316 to deploy ransomware.
Check Point fixed critical Check Point VPN vulnerabilities. Update gateways to prevent remote code execution under CVE-2026-85102 and CVE-2026-85103.
Details and PoC for a Cisco Secure Boot bypass vulnerability are public. Learn how this Cisco Secure Boot bypass affects UCS servers and appliances.
The September 2026 Android Security Bulletin patches critical RCE flaws like CVE-2026-28604 in the System component. Update to patch level 2026-09-05.
Four Apache Impala vulnerabilities expose systems to remote code execution and authentication bypass. Upgrade to Impala 4.5.2 to secure your clusters now.
Details and PoC for CVE-2026-84372 are publicly disclosed. This Predis command injection flaw via CRLF smuggling allows complete cluster compromise.
A critical MapLibre XSS vulnerability allows zero-click code execution in 2.7M weekly downloads. Discover how CVE-2026-85061 works and how to patch now.
A critical CVE-2026-67401 cPanel SQL injection flaw in EmailTrack allows authenticated users to gain full control of the server. Patch your system today.
Apache Nutch vulnerabilities include CVE-2026-41870, an unauthenticated remote code execution flaw. See affected versions and fixes.
Two critical Siemens vulnerabilities (CVE-2026-18963, CVE-2026-50093) allow account takeover and root access. See affected versions and fixes.
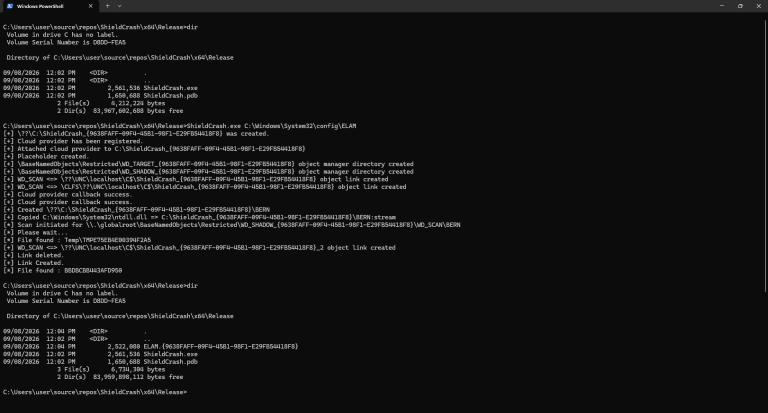
A Windows Defender 0day, CVE-2026-69414, has public PoC exploit code. ShieldCrash reads files as SYSTEM on all supported Windows versions.
A critical Hawtio Operator vulnerability, tracked as CVE-2026-78234, allows in-cluster service impersonation. Discover the impact and mitigation steps.
Google patched a Chrome zero-day, CVE-2026-87491, exploited in the wild. Chrome 153 fixes 230 flaws including critical WebGL bugs. Update now.